Choosing a penetration testing company comes down to five checks: confirm the work is manual (not just automated scanning or AI-generated findings), verify tester credentials include hands-on certifications like OSCP, HTB CPTS, or PNPT, review a sample report, check for SOC 2, ISO 27001 or other compliance frameworks and liability insurance, and get quotes from at least three vendors before signing.
Cybersecurity is a critical part of any modern business, and with regulatory frameworks such as GDPR, PCI DSS, and SOC 2 now standard expectations from customers and auditors, a solid security testing program isn't optional for managing security risks.
But with so many penetration testing vendors on the market, selecting a reputable one that will actually meet your requirements is hard. Below are our top 10 tips for choosing a reliable partner, and the factors that separate a reputable penetration testing company from a risky one.
Ensure your pentest provider offers manual penetration testing, not just automated vulnerability scanning
It is crucial to be aware that some cybersecurity companies might provide automated vulnerability scanning under the guise of manual penetration testing.
To support your goals, you must be mindful of the differences between vulnerability scanning and penetration testing and make sure you receive the right service.
Manual penetration testing requires a skilled tester to actively exploit vulnerabilities using real-world attack scenarios. In contrast, automated vulnerability scanning relies on signatures and known vulnerability patterns to identify potential security weaknesses, often yielding a high rate of false positives.
Manual penetration testing is superior, relying on human expertise to allow for a more thorough and customized assessment of the system's vulnerabilities.
While an automated vulnerability scan can still be useful for identifying vulnerabilities, it is not a substitute for a penetration test led by security experts.
There's a newer wrinkle to watch for in 2026: some vendors now market AI-assisted or "autonomous" penetration testing, where a large language model drives part of the exploitation process. That can be a legitimate productivity aid, but ask the vendor to disclose exactly which parts of the engagement were AI-led versus human-validated. An AI agent chaining exploits without a human confirming each finding has the same false-positive and business-context blind spots as other automated tools.
| Manual penetration testing | Automated scanning | |
|---|---|---|
| Who drives it | A skilled pentester actively exploiting flaws | Signature-based tools, with or without AI assistance |
| False positive rate | Low: findings are validated by exploitation | Medium to high: can flag patterns without confirming exploitability |
| Business logic flaws | Testers reason like an attacker | It's harder for tools to identify real-world threats |
| Best used for | Compliance-grade pentests, high-risk systems | Continuous baseline monitoring between pentests |
What certifications should the penetration testers I am looking to hire have?
There is no shortage of certifications related to penetration testing. Some are well respected in the industry for having a high bar, focusing on practical and hands-on assessments. Others are far from challenging and don’t adequately assess a candidate’s ability to perform penetration tests and security audits professionally.
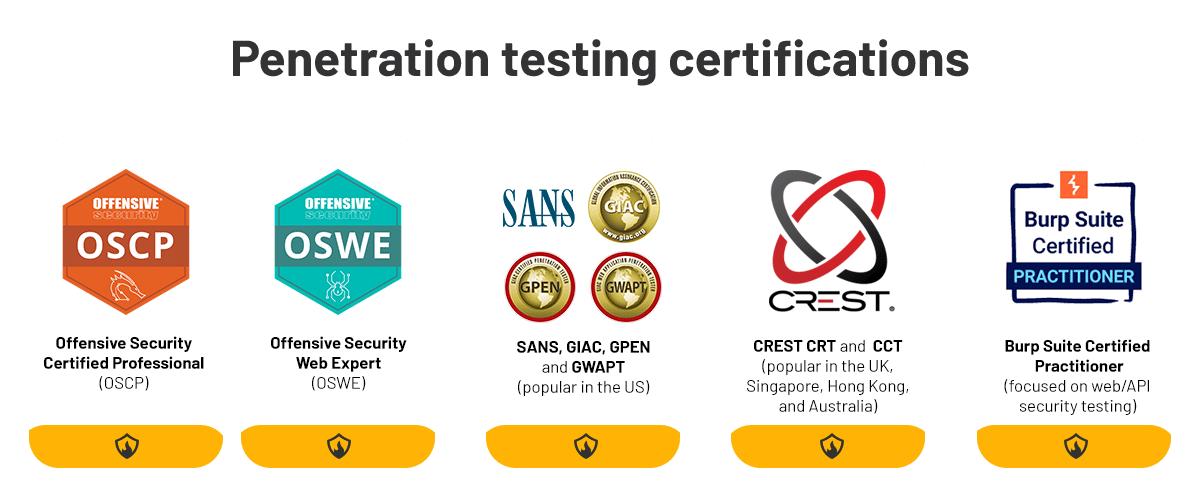
Below are some of the certifications that ensure a penetration tester is certified with practical skills to conduct a pentest assessment:
- Offensive Security Certified Professional (OSCP) and Offensive Security Web Expert (OSWE)
- Burp Suite Certified Practitioner (focused on web/API security testing)
- SANS GIAC GPEN and GWAPT (popular in the US)
- CREST CRT and CREST CCT (popular in the UK, Singapore, Hong Kong, and Australia)
- HTB CPTS(Hack The Box Certified Penetration Testing Specialist): a fully practical, exam-based credential that's gained fast recognition as an OSCP alternative or precursor
- PNPT(Practical Network Penetration Tester from TCM Security): notable for putting candidates through a full simulated engagement, including a findings debrief
It's important to note that the popular Certified Ethical Hacker (CEH) certification is often mocked by experienced practitioners and seen as low-quality; it is not hands-on and is considered easy to pass.
What methodologies should my vendor employ in the pentesting process?
When considering a company that can provide penetration testing services, it is essential to ensure they use best practices and proven methodologies.
On the other hand, it is desirable that the provider has a hacker mindset and "think out of the box" creativity to go beyond common checklists.
Popular methodologies include the PTES, OSSTMM, SANS CWE 25, NIST SP 800-115, or the OWASP Top 10; the latter has specific methodologies for pentesting web applications, mobile apps, API, and IoT devices.
Google's Pentest Guidelines provide invaluable insights into how they recommend business partners evaluate a pentest vendor's proposed methodology and approach for penetration testing.
The right experience and technical expertise for the job
The right partner company should have staff that stays up-to-date with the latest tools and techniques and often showcases their technical capabilities in the form of blog posts, open-source tools, and presentations at industry events.
It is important to ask questions about the company's experience with your scope of work to ensure they have the required expertise for the assessment. If you are looking for an internal penetration test of your internal network, a company with solid knowledge of Active Directory, for example, is preferred. Or if you are looking for an SAP security assessment, hiring a pentest company that is strong in pentesting web applications makes little sense.
Ask to review sample reports and other deliverables
Ask the pentest company to provide sample reports, attestation letters, and other deliverables they might have. These documents are required to understand their findings' quality and the testing depth. Look for clear and actionable insights and recommendations for addressing vulnerabilities. Quality of reporting is key; after all, a report is the main deliverable you will receive as part of your penetration testing engagement.
For additional checks when shortlisting providers, our analysis of best penetration testing company rankings explains why a list position alone is weak evidence of technical quality. If a vendor offers AI-led testing, our research on attacks against LLM pentest agents provides examples to discuss during technical due diligence.
We have written a blog post titled What To Expect From a Penetration Testing Report that explains all the details about this topic.
Ask for references from past and existing customers
When evaluating potential vendors for penetration testing services, getting feedback from past and existing customers is invaluable. Requesting references from these sources should be a critical part of your evaluation process – this will provide you with important information about the quality of service delivered by the penetration testing firm and bring additional insight into the vendor.
Pricing – what is the fair cost of a pentest?
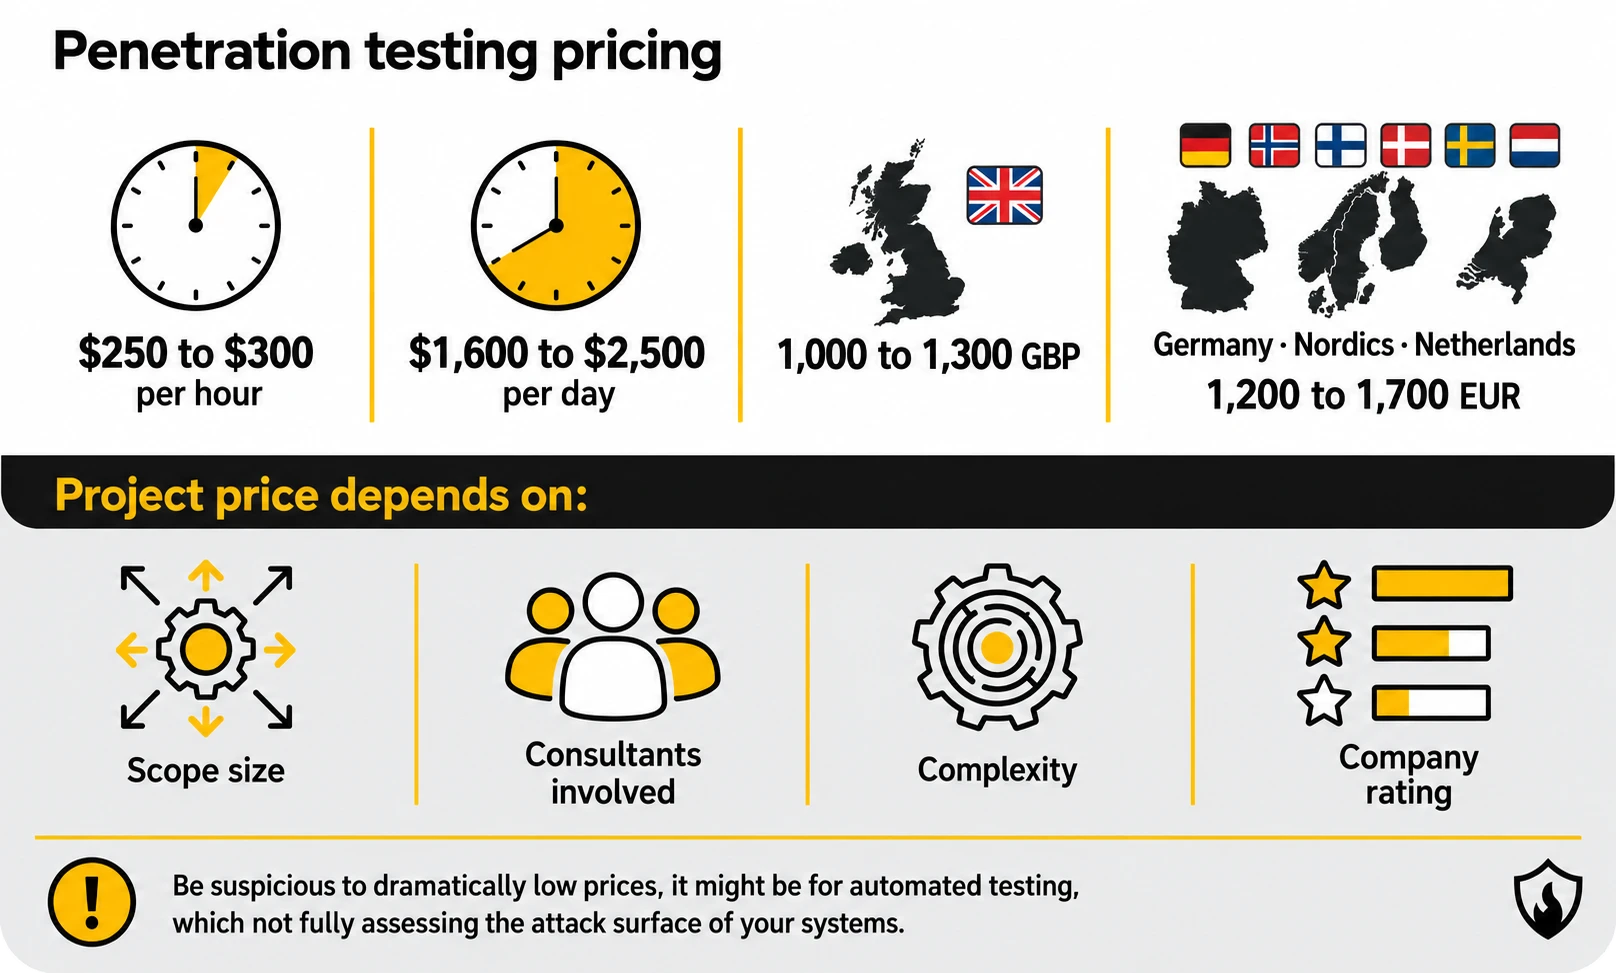
In our experience, the final cost of a penetration test can vary depending on the scope, size, complexity and the number of consultants involved in the project, with rates per penetration tester employed by a reputable firm averaging between $1,600 to $2,500 per day in the United States.
Many pentest providers start at a ballpark figure of $200 to $300 per hour – with niche and specialized work often having a higher hourly price tag. We have written a comprehensive blog post about how much a penetration test costs, how to understand the nuances in comparing a pentest quote, and all the factors influencing it.
The average rate per pentester in the United Kingdom is between 1,000 GBP to 1,300 GBP per day, varying more or less among pentest providers. In European countries with strong economies, such as Germany, The Netherlands, and Nordic countries, average daily rates range from 1,200 to 1,700 EUR. Niche work, and the reputation of the brand of the penetration testing vendor, are factors that influence pricing.
Be suspicious of a penetration testing provider charging dramatically low prices. It is highly likely they mainly use automated testing and perform a vulnerability scan disguised as a manual pentest, not fully assessing the attack surface of your systems.
Does your pentest provider have data protection measures in place?
Data protection and security standards must be upheld to the highest degree when selecting a supplier for penetration testing. It is essential that mature penetration testing providers are compliant with data protection standards such as the ones outlined in ISO 27001 certification, a popular international information security standard, or SOC 2, both of which provide assurance of best practices when it comes to handling sensitive data.
Surprisingly, many cybersecurity service providers do not have strong data protection controls in place and lack the right certificates to demonstrate they are suitable to handle third-party sensitive data.
Does the company have adequate liability insurance?
Professional liability insurance is essential for any business, including those offering data protection and cybersecurity services.
When procuring pen testing services, ensure your supplier has adequate liability insurance to cover any potential damages in the unlikely event something goes wrong in an assessment.
Organizations have different requirements in setting a minimum amount for coverage for professional liability insurance. In our experience, many are comfortable with an insurance cover of $2,000,000 or €2,000,000; however, this can change depending on the contract and industry, with financial services and banks requiring significantly more coverage. Here at Blaze, we opted to have higher worldwide insurance coverage of €5,000,000 due to the requirement of enterprise customers.
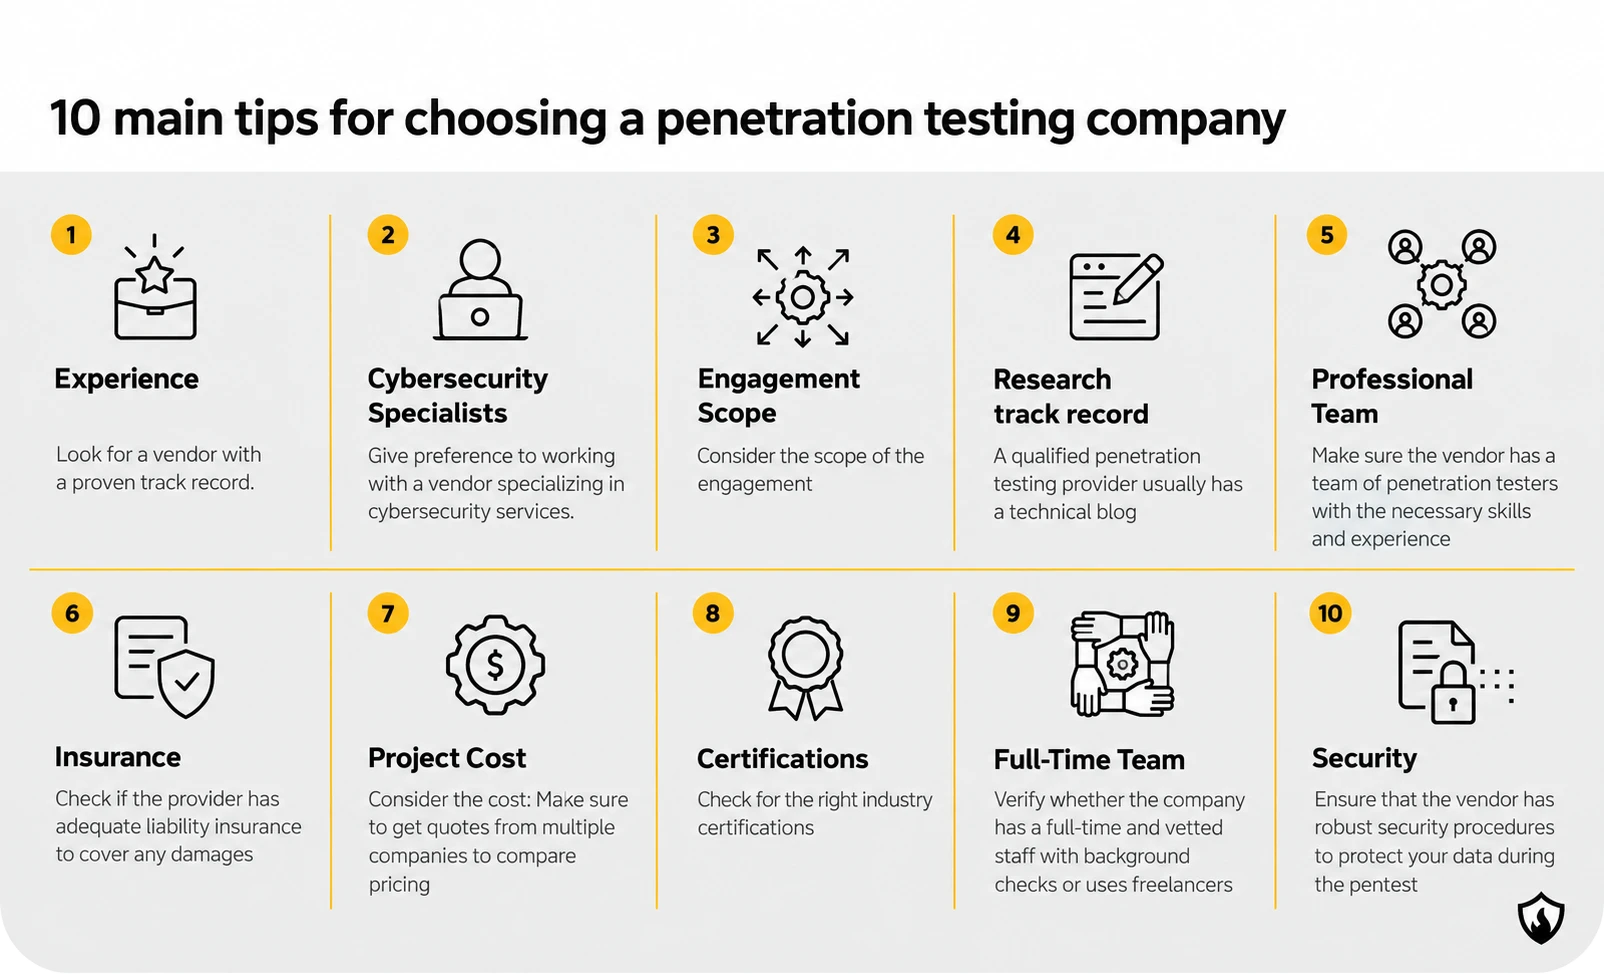
Top 10 tips for choosing the right penetration testing company
- Look for a vendor with a proven track record of security research, experience in penetration testing similar organizations, and the ability to provide client references.
- Give preference to working with a vendor specializing in cybersecurity services. These often provide superior pentest assessments than firms with a more extensive portfolio of services, many of which are not directly related to cyber (e.g., accounting and audit firms, managed IT services providers, etc.).
- Consider the scope of the engagement: It's important to define the scope so you can choose a company with the necessary expertise and resources. For example, suppose you need a penetration test of an IoT product. In that case, you'll want to choose a company with experience in product security testing for IoT devices, or if you want a complex mobile app assessed, look for a vendor with a track record in mobile app security testing.
- A qualified penetration testing provider usually has a technical blog, GitHub, or other channels to display their technical capabilities, vulnerabilities they have found, and original cybersecurity research.
- Ensure the supplier has a team of penetration testers with the necessary skills and experience to conduct a comprehensive assessment, uses state-of-the-art tools and follows industry-standard methodologies.
- Check if the penetration testing company has adequate liability insurance to cover any damages if something goes wrong during the security testing assessment.
- Consider the cost: Make sure to get pentest quotes from multiple providers to compare pricing and ensure that you're getting a fair price for the services you need. It's important to remember that dramatically low prices may hint that the company isn't suitable for the job, or performs vulnerability scans instead of manual pentests.
- Check for the right certifications: Consider a penetration testing company with qualified staff with credentials such as OSCP, OSCE, OSWE, and SANS GIAC, as these can be indicators of the company's expertise and commitment to professionalism.
- Verify whether the company has a full-time and vetted staff with background checks or uses only freelancers. While some organizations don't mind contractors, some have strict policies not allowing freelancers access to sensitive systems and data. Surprisingly, many vendors, especially those operating in the crowdsourced security field, work exclusively with freelancers, not full-time pen-testers.
- Ensure the vendor has robust security procedures to protect sensitive data during the pentest, such as being SOC 2 or ISO 27001. Ironically, many penetration testing vendors are not compliant and don't have auditable data security procedures.
Don't take our word for it alone: many of the recommendations above have been developed by Google to help companies undergoing Vendor Security Assessment with penetration testing provider selection.
Below is a penetration testing company selection checklist infographic.
Final words
Choosing the best penetration testing provider for your needs can be a complex task. With a market full of different options and similar offerings, buyers hardly have clear guidance to select a penetration test provider that is the perfect fit for what they are looking for.
When exploring the realm of pen testing companies, it is crucial to look beyond the surface. By focusing not just on cost but also on factors such as team expertise, methodology, comprehensive penetration test report, and communication, you can better discern each contender's value. Remember, pen testing should not be seen as just a compliance exercise, so selecting from the top penetration testing providers should be a priority. For a broader look at how today's vendor landscape breaks down: from boutique specialists to the large consultancies, see our buyer's guide to penetration testing companies.
The best penetration testing companies for your organization are the ones that can tailor their approach to your unique needs. This includes not only being able to identify vulnerabilities within your systems but also advising on how to rectify them most efficiently. The top providers offer comprehensive penetration testing services and a custom approach backed by experience and certifications. Proven track record in security consulting, helping businesses improve their security and compliance posture, is a testament to their capabilities.
By following the tips outlined in this article, you should be well on your way to finding a reputable and competent penetration test partner that will suit your needs. If your organization is looking for a new provider and wants to engage with a CREST-accredited qualified vendor founded by experienced cybersecurity engineers, contact us today.