ISO 27001 penetration testing, scoped to your ISMS
Test the applications, APIs, cloud, and infrastructure inside your ISMS scope. Blaze validates exploitable weaknesses and delivers clear technical reporting to support risk treatment, certification, and surveillance audits.
Testing that fits your ISMS scope
Share your audit date, the systems you need tested, and any evidence your auditor requested. If you have a Statement of Applicability, we’ll use it to help scope the test.
Test the right systems
For example, a SaaS test might cover the customer app, its API, and the cloud services that run them.
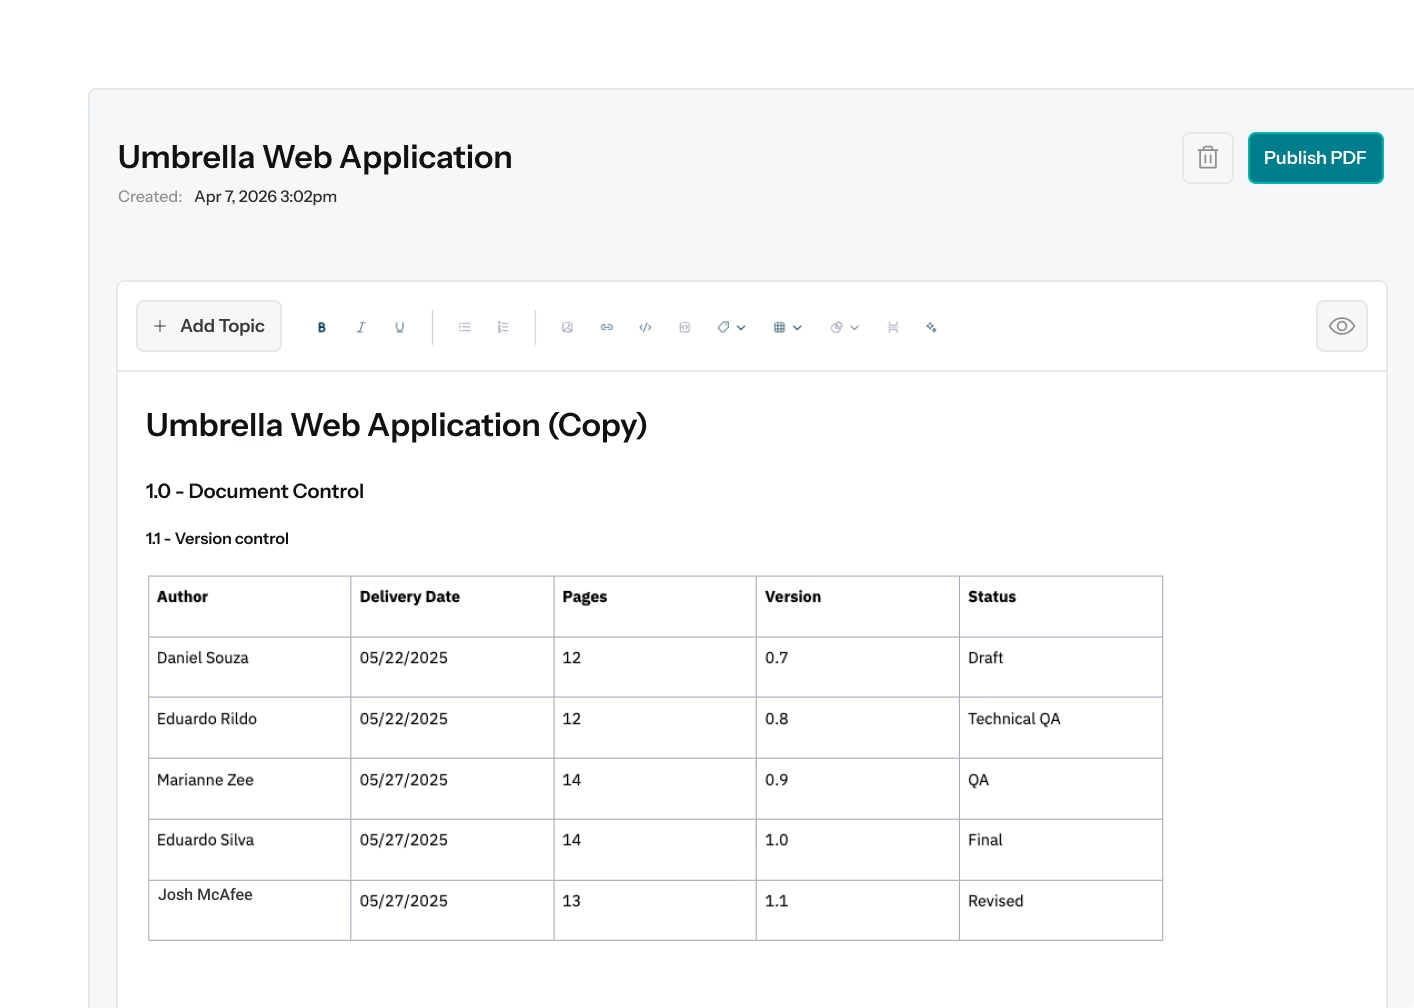
Prove which weaknesses are exploitable
Manual testing goes beyond vulnerability scanning to confirm real attack paths, business impact, and the fixes that deserve priority.
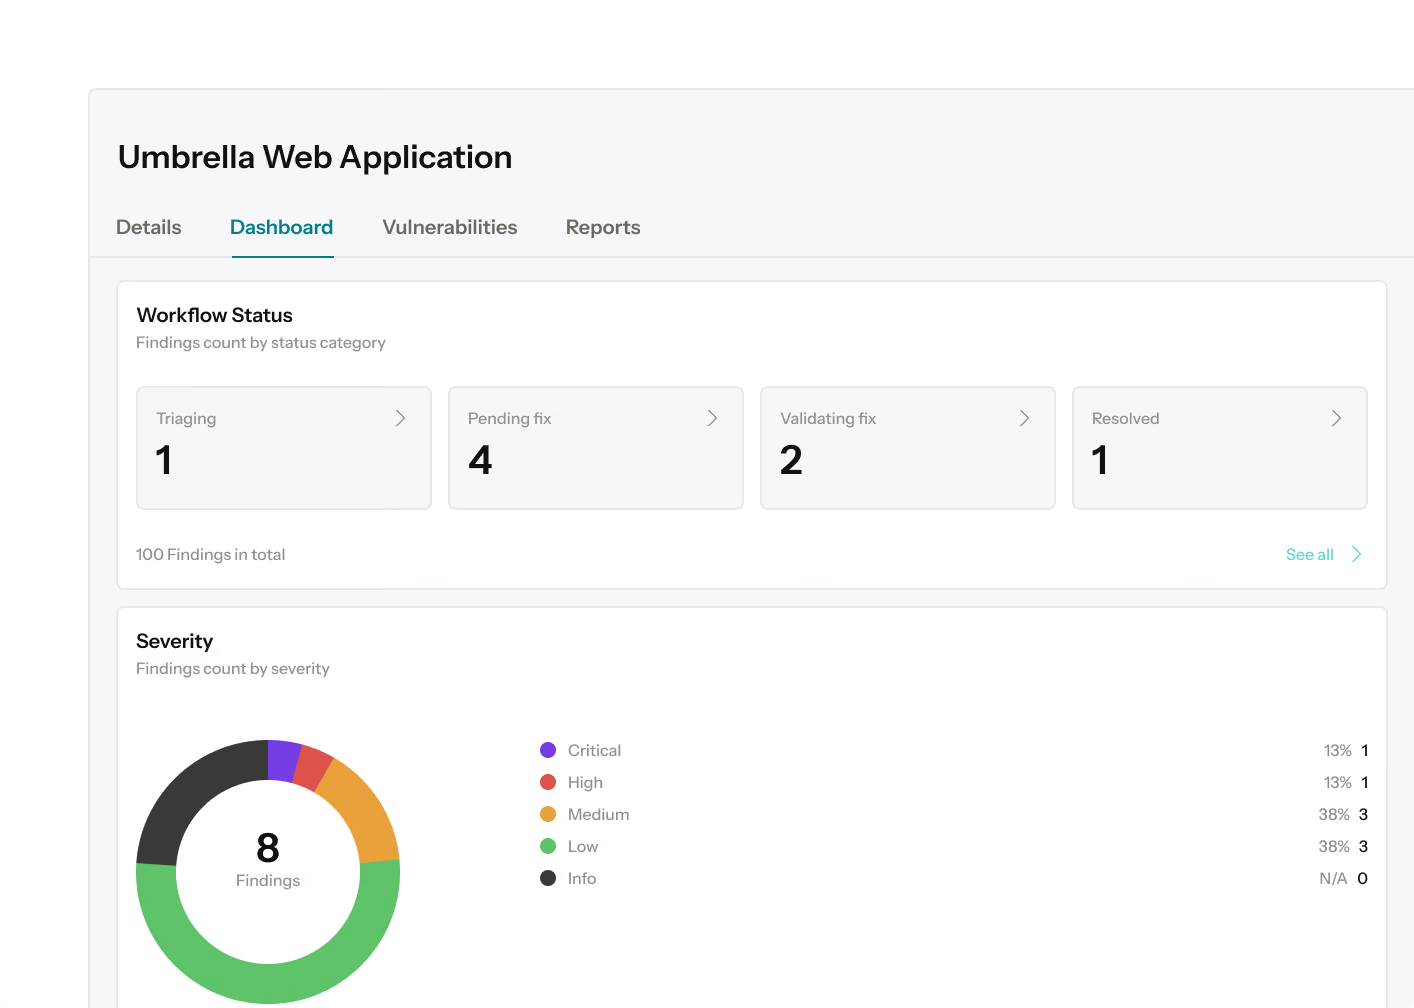
Feed findings into risk treatment
Use validated findings, severity, remediation guidance, and optional fix validation to support treatment decisions and track progress after the test.
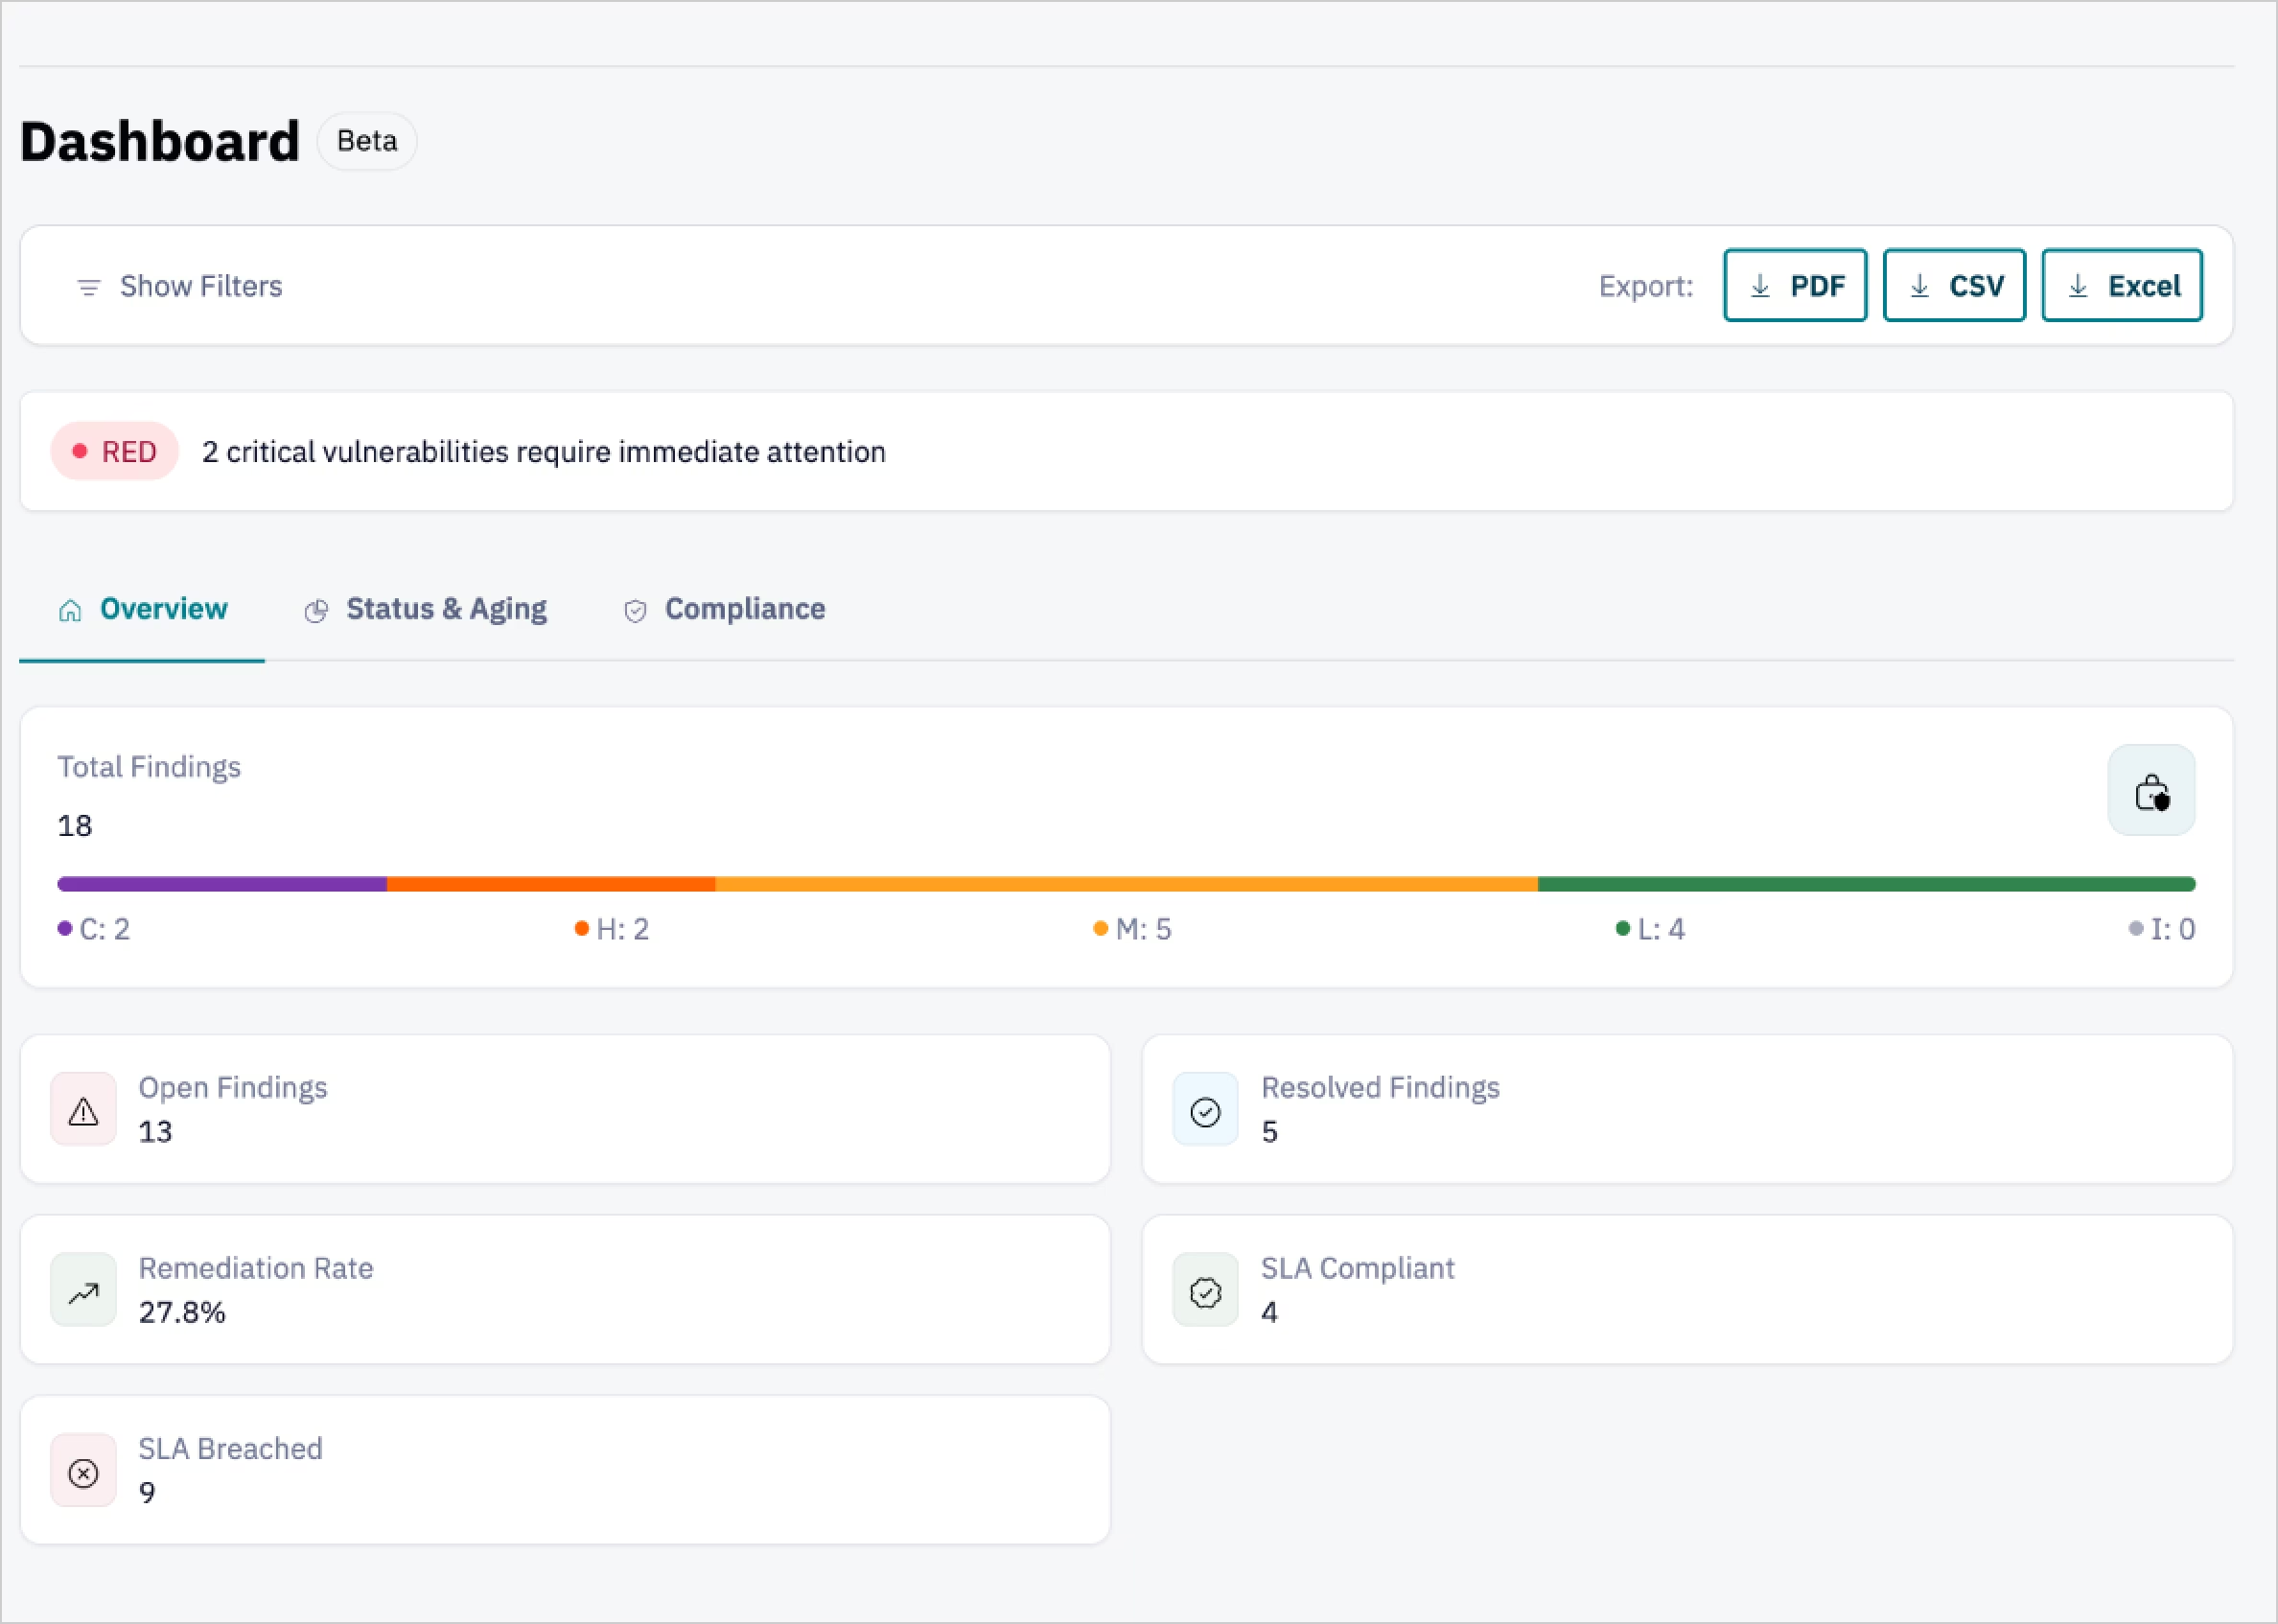
How penetration testing supports ISO 27001
Penetration testing can support controls such as A.8.8 and A.8.29 when they apply to your risk treatment plan and Statement of Applicability. Your organization and certification body determine the final control interpretation.
Requirement
How Blaze helps support it
A.8.8
Management of technical vulnerabilities
Independent penetration testing to identify, validate, prioritize, and remediate exploitable vulnerabilities.
A.8.25
Secure development life cycle
Tests applications, APIs, and product changes to validate whether security is built into development and release workflows.
A.8.29
Security testing in development and acceptance
Evidence of application, API, infrastructure, and cloud security testing before or after systems enter production.
A.5.35
Independent review of information security
Provides technical testing evidence to support the organization’s independent review of information security.
A.5.36
Compliance with policies, rules and standards
Assesses applicable internal technical requirements within the agreed scope and documents identified deviations.
Practical outputs for security, risk, and audit teams
Clear technical findings, remediation context, and reporting that can support your wider ISO 27001 program—without pretending one pentest certifies the ISMS.

Scope aligned to your ISMS
We scope testing around relevant assets, data flows, risk priorities, and the systems covered by your ISMS.

Validated technical findings
Each delivered finding is reviewed for exploitability, business impact, and clear remediation steps.

Reporting for different audiences
Share technical detail with engineering and concise context with risk owners, leadership, customers, or auditors.

Independent security testing
Blaze is CREST-accredited. Testing is delivered by qualified researchers, with findings reviewed before delivery.

Remediation workflow
Assign each finding to an owner in the Blaze Portal. Track severity, fix status, and retest results in one place for your audit records.

Optional fix validation
When included, we retest agreed fixes and document the updated state for your remediation records.
Put the same findings to work
Where scope and requirements overlap, the same validated findings may support other security reviews without replacing each framework’s separate obligations.
SOC 2
Use relevant application, cloud, and network findings in customer assurance and SOC 2 readiness workflows.
HIPAA
Support risk analysis and technical assurance for systems that handle electronic protected health information, where applicable.
ISO 27001 pentesting questions
Extend your ISO 27001 security program
Add broader testing or ongoing security leadership where your risk assessment, customer commitments, or internal priorities call for it.
Penetration Testing
Test web applications, APIs, mobile apps, cloud environments, and networks for exploitable security weaknesses and actionable remediation.
Red Teaming
Challenge detection and response against agreed attack objectives when deeper adversary simulation fits your risk program.
Fractional CISO
Add ongoing security leadership for risk, governance, audit preparation, customer assurance, and coordination across technical workstreams.
Plan your ISO 27001 pentest
Share your audit deadline and what needs testing. Your quote will confirm the scope, test start date, report date, and fix-validation options.
