ISO/IEC 27001:2022 does not set one universal, standalone penetration-testing requirement or fixed testing schedule. Testing should address the information-security risks, controls, commitments, and evidence needs of the organization’s ISMS.
This buyer’s guide explains how to define the scope, choose a provider, plan testing effort, and use findings and retest results as evidence. For a focused discussion of requirements and cadence, see our ISO 27001 testing requirements article.
ISO/IEC 27001:2022 defines requirements for establishing, maintaining, and improving an information security management system. A penetration test is one possible source of technical evidence within that system. It is not an ISMS audit, a certification decision, or proof that every relevant control is effective.
Who will benefit from this ISO 27001 penetration testing guide?
We crafted this guide with the intention of being an authoritative source of information offering relevant insights into pen testing for ISO 27001 audits to the following groups of individuals who may need to procure penetration testing services:
- Executive personnel in charge of IT security in an organization (CISO, VP of security, CIO)
- Upper management, such as C-level executives (CEO, CTO, COO, CFO, board members)
- Key individuals of an audit team and audit committees
- Auditors and compliance officers
- Cybersecurity professionals, including engineers and analysts (AppSec, SecOps, InfraSec, etc.)
- Engineering managers and product owners who were involved in the organization’s ISO 27001 compliance project
What is ISO 27001 compliance, and why is it important?
ISO/IEC 27001 is perhaps the most recognizable of all existing information security standards. ISO 27001 outlines a framework for an organization’s information security management system (ISMS), providing a set of guidelines and requirements for establishing, implementing, maintaining, and continually improving information security.
The standard is based on a risk management approach, which helps organizations identify, assess, and prioritize the risks to their sensitive information and implement controls to reduce those risks to an acceptable level. ISO 27001 specifies the requirements for an ISMS, including the policies, procedures, and controls an organization should have to protect its sensitive information.
Being ISO 27001 compliant is an important step for a company from a data security and information security policies point of view. A certified organization is in a much better position to not only protect customer data and avoid data breaches but also is able to demonstrate to clients and business partners that they have solid and auditable security processes in place, helping them to gain the confidence of these stakeholders and close deals where risk assessments and compliance play a definitive role.
What is ISO 27001 penetration testing?
An ISO 27001-focused penetration test evaluates defined applications, APIs, networks, or cloud systems in the context of the organization’s ISMS risks. Its findings can support control evaluation and risk treatment; the test does not satisfy an entire control or establish certification by itself.
There are multiple types of penetration testing, and such assessments can be conducted through various approaches, each of which considers a different viewpoint:
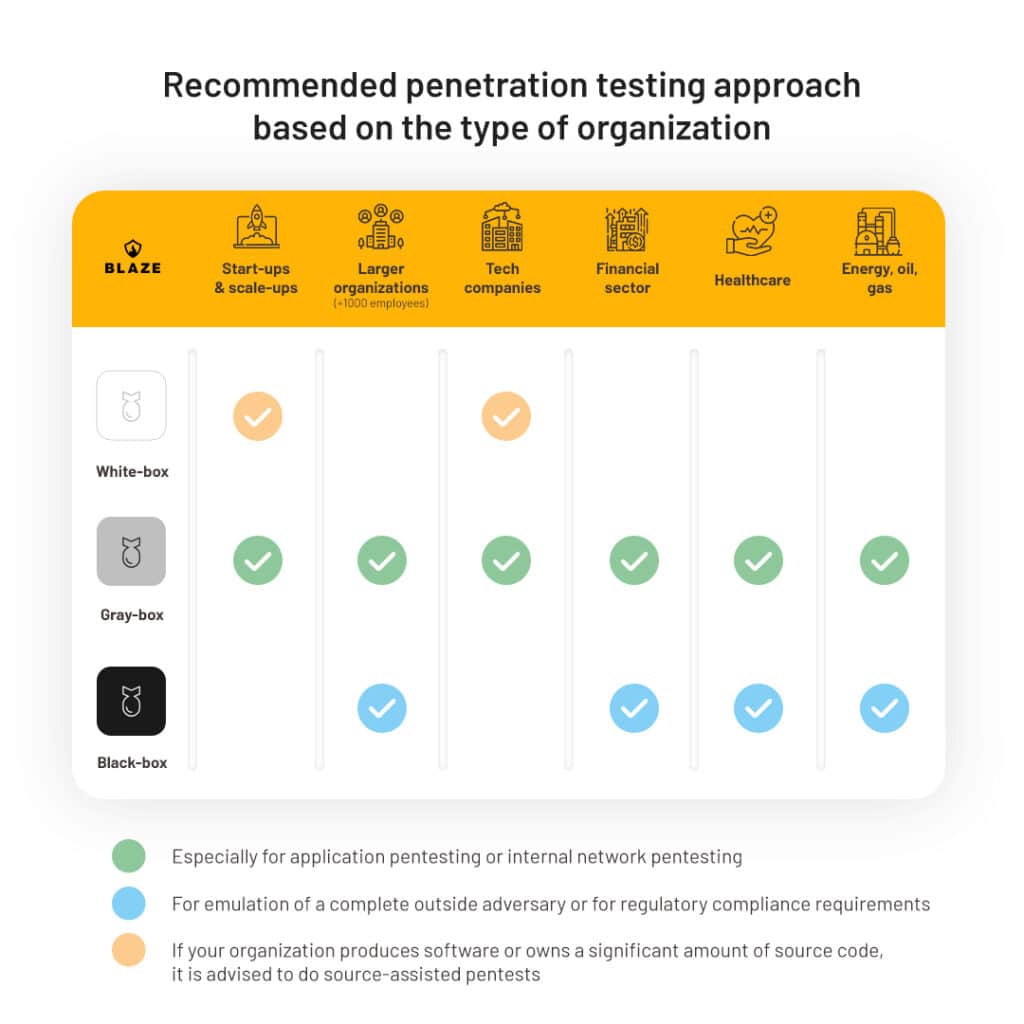
Most professional cybersecurity firms discourage pentests based on a purely black-box approach unless it is the threat model and level of adversary your company wants to emulate. Our experience says that gray-box testing is preferred for most ISO 27001 penetration testing engagements.
Penetration tests can be enhanced with automated tools, but skilled and professional pentesters will go beyond automation and conduct manual tests. Although more time-consuming, manual tests often uncover hidden security vulnerabilities that scanning tools miss. Automated tools are useful for routine tasks, such as scanning for open ports or checking for known vulnerabilities, but they cannot replace the expertise of a seasoned, ethical hacker trained to identify vulnerabilities and risks.
How penetration testing supports ISO/IEC 27001:2022
The risk assessment, risk treatment plan, Statement of Applicability, and relevant commitments should explain why testing is needed and what it must evaluate. Annex A controls relevant to this work include A.8.8, Management of technical vulnerabilities, and A.8.29, Security testing in development and acceptance. The old A.12.6.1 and A.14.2.8 numbering belongs to the 2013 edition.
A pentest can provide evidence about exploitable weaknesses and security behavior within its agreed scope. That evidence must be considered alongside vulnerability management, development practices, remediation, and other controls. Avoid describing one assessment as automatically satisfying either control.
Where vulnerability scanning fits
Scanning helps teams identify known vulnerabilities and configuration issues at scale. Penetration testing adds investigation of exploitability, authorization, business logic, and attack paths. Select the combination and cadence through the ISMS risk process rather than assuming ISO 27001 prescribes a universal tool or quarterly scanning schedule.
How much testing time should you plan?
Testing effort depends on the scope and depth: applications, roles, endpoints, environments, integrations, network size, and access conditions all matter. Ask providers to explain the allocation of manual testing, reporting, and fix validation.
There is no universal minimum number of days for an ISO 27001-focused pentest. Compare equivalent scopes and deliverables; neither a short duration nor a higher price proves the quality of the assessment.
How to define the scope of an ISO 27001 penetration test?
The organization owns the assessment scope. Security, engineering, compliance, and the testing provider should connect the selected systems and attack scenarios to documented risks and the ISMS boundary. Clarify evidence expectations with the certification auditor where relevant; the auditor does not automatically define or approve every testing decision.
Based on our experience, organizations undergoing an audit typically consider the following elements for their ISO 27001 penetration testing scope:
- The organization’s flagship product, such as a SaaS platform
- Internet-facing server infrastructure (usually cloud-hosted)
- The organization’s internal network, servers, and key infrastructure, such as Active Directory, Kubernetes clusters, etc.
- APIs (REST, GraphQL, legacy web services) and microservices
- Security testing of mobile apps, if applicable
- Any administrative panel or back office supporting the user-facing SaaS
A representative staging environment can reduce production disruption. Document differences in configuration, identity, data flows, integrations, and deployed versions, and explain which risks remain untested. Agree authorization, safety limits, emergency contacts, and evidence requirements before execution; do not assume a staging assessment proves the live environment is secure.
Keep an evidence chain from scope to fix validation
Retain the agreed scope, methodology, test dates, access conditions, findings, remediation ownership, risk-treatment decisions, and retest results together. Distinguish verified fixes from accepted risks and work that was outside scope. For empirical issue patterns, see common ISO 27001 penetration testing findings.
How to compare ISO 27001 pentest pricing
Compare quotes for the same scope, testing depth, access conditions, reporting, and retest terms. Confirm exclusions, scheduling assumptions, data handling, and what happens if the scope changes. Avoid treating an unsourced market range or hourly rate as a reliable estimate for your environment.
Use our penetration testing cost guide for budget factors, then request a scoped proposal. The assessment objective and deliverables should drive the quote.
Which testing methods should the provider use?
Ask for a documented method appropriate to the target. For web applications and APIs, the OWASP Web Security Testing Guide supports test planning, while OWASP ASVS provides verification requirements. The OWASP Top 10 is an awareness list, not a complete penetration-testing methodology.
NIST SP 800-115 provides guidance on technical security testing. A provider should explain how its approach covers your assets, roles, trust boundaries, and business workflows, and how it handles manual investigation, evidence, reporting, and retesting.
Should I perform penetration testing and vulnerability scanning as part of my ISO 27001 audit?
Even though pen tests and vulnerability assessments are not mandatory to achieve compliance with ISO 27001, there are still several benefits to performing such activities to achieve your industry and regulatory compliance audit goals and improve your cyber defenses:
- Identification of vulnerabilities: Penetration testing is crucial for organizations to identify security issues in their systems and networks that malicious hackers might exploit.
- Risk reduction and effort prioritization: Pentesting findings highlight security gaps, expose risks, and allow organizations to prioritize their efforts in remediating these vulnerabilities, improving their overall security defenses, and reducing cyber risks.
- Challenging the effectiveness of security controls: Performing technical security assessments allows organizations to evaluate the effectiveness of their security controls in detecting and preventing attacks. Ultimately, this can help organizations identify gaps in their security measures and spot weaknesses in their defenses.
- Supporting audit evidence: Link test results to the documented risks and controls being evaluated. Other frameworks, including SOC 2 and PCI DSS, have different requirements and evidence expectations; do not assume one report establishes compliance across them.
- Protecting against cyber-attacks and data breaches: A professional penetration test can help organizations anticipate real-life adversaries by identifying and addressing vulnerabilities before they are exploited by threat actors, going beyond a checkbox in compliance.
- Increased security awareness: Pen testing can also serve as a practical learning opportunity for organizations, helping to improve security awareness and understanding among employees and management and making a business case for increased investments in cyber defense.
How to set a testing cadence
Set the cadence from risk, material changes, customer commitments, and the evidence needed for the ISMS. An annual assessment can be a planning baseline, but it is not a universal ISO 27001 rule. Consider earlier testing after significant changes to authentication, authorization, APIs, cloud architecture, sensitive-data flows, or the system boundary.
Document the rationale and revisit it when the environment changes. Our requirements and frequency guide covers that decision in more detail.
Closing thoughts
ISO 27001 is certainly a very useful resource for businesses seeking to improve their information security processes, safeguard customer data, and show they have an information security management system with strong controls in place.
While penetration testing and scanning are useful for discovering security vulnerabilities and uncovering associated risks to information systems, they are not required for ISO 27001 compliance purposes. Whether or not to conduct a penetration test or a vulnerability assessment as part of your ISO 27001 audit should be based on your organization’s specific risk profile and security objectives.
A useful penetration test report connects scope, findings, remediation decisions, and retest results. Present it as bounded technical evidence within the ISMS, together with the other records needed to evaluate control effectiveness.
If you need penetration testing to support your ISO 27001 evidence plan, talk to an expert about the systems, risks, and deliverables in scope. Blaze provides security testing; the certification body makes the certification decision.