Fractional CISO Services
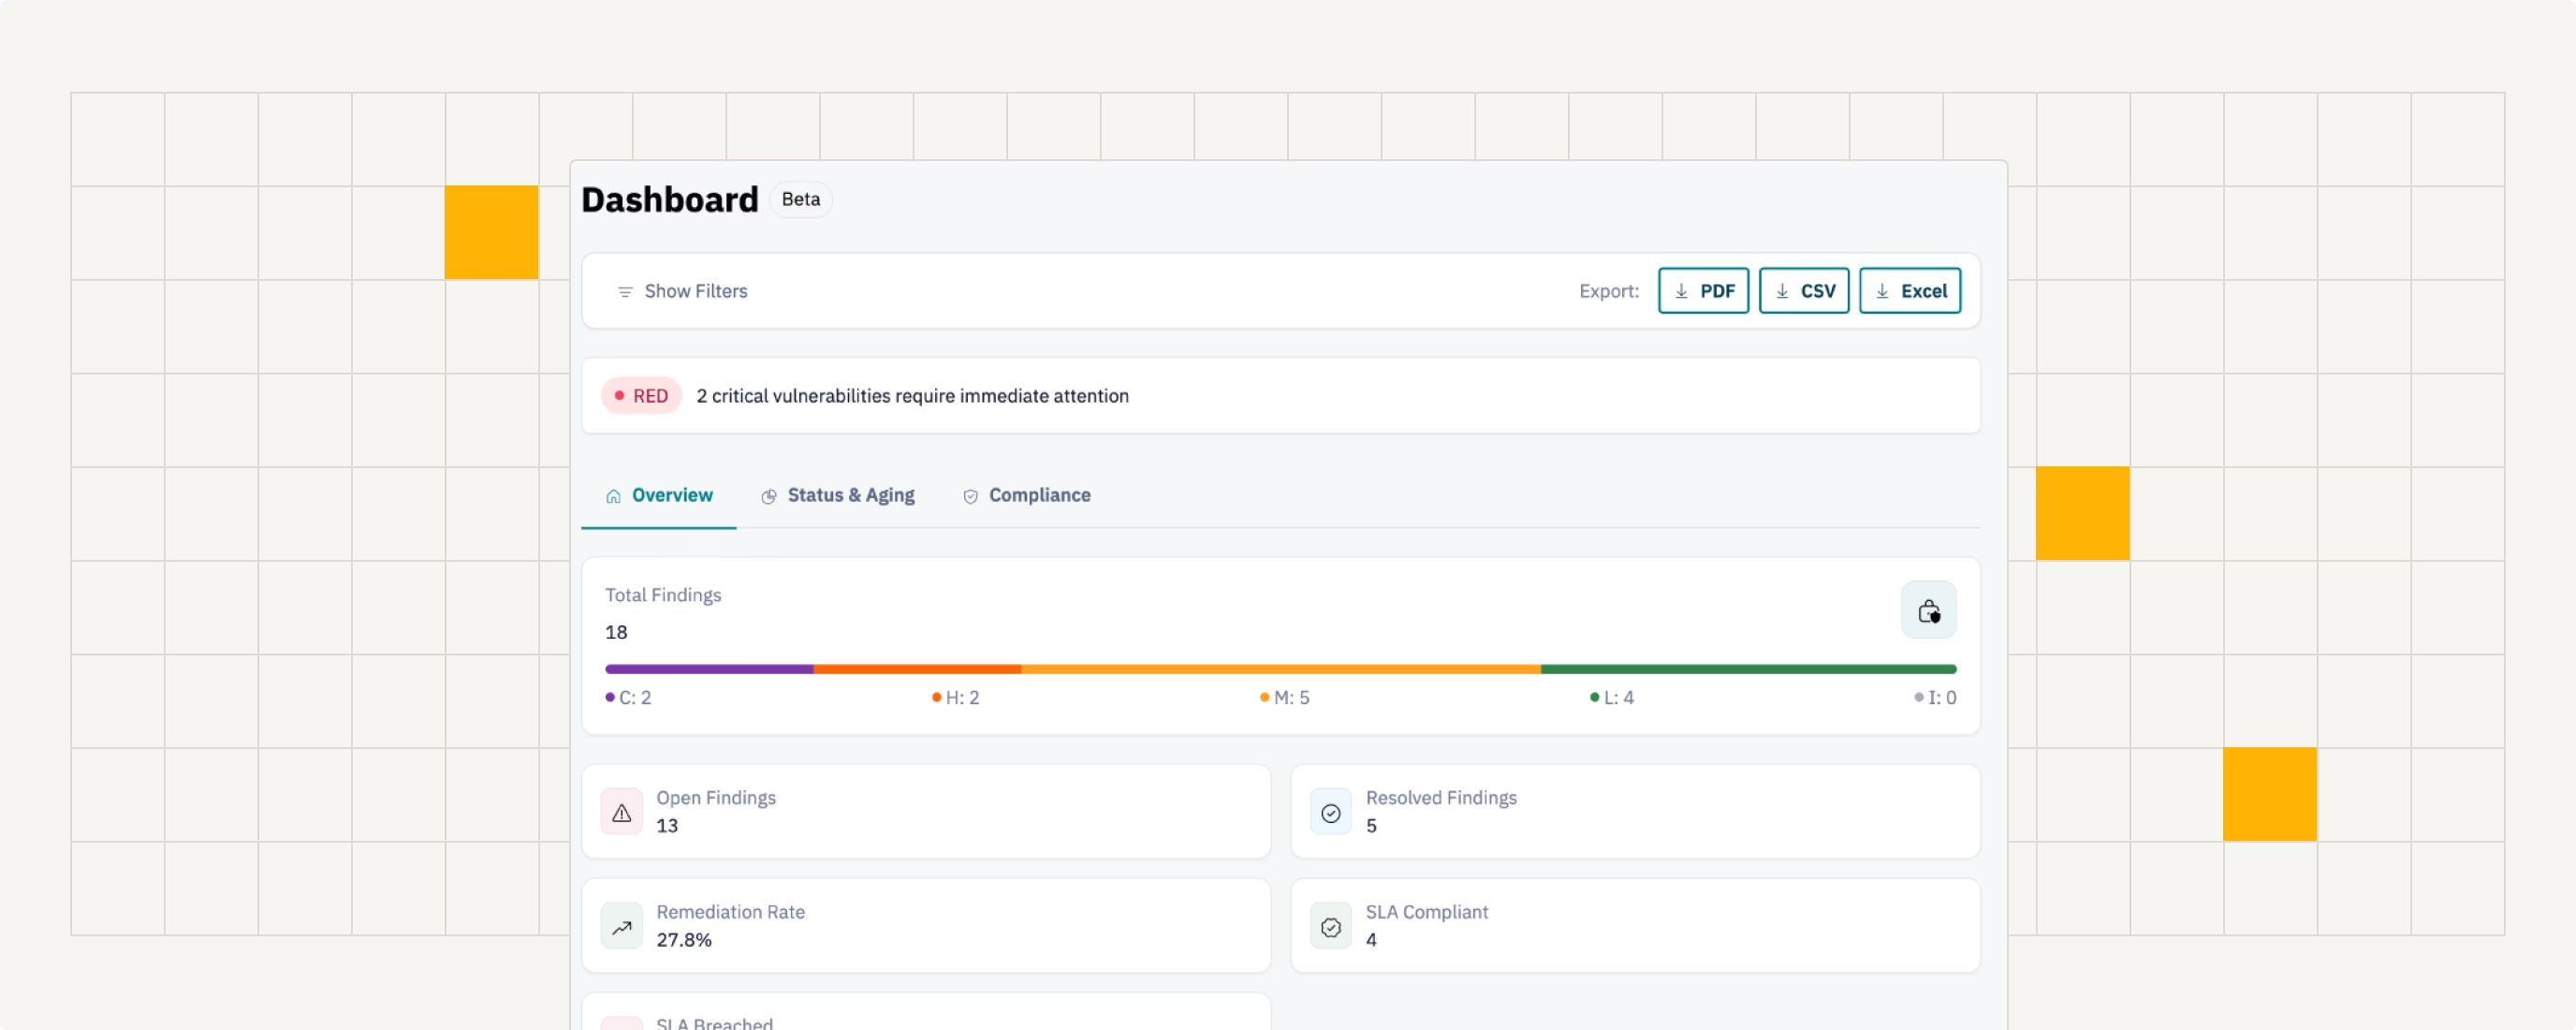
Senior security ownership
Prioritized roadmap
Business, risk, and compliance
Executive clarity
CISO-level ownership—without the full-time executive hire
Trusted by 400+ organizations worldwide.
Your Blaze Fractional CISO owns questionnaires, policies, compliance readiness, risk decisions, and executive reporting—backed by offensive-security specialists whenever technical validation is needed.








When a Fractional CISO makes sense
A Fractional CISO—also called a virtual CISO or vCISO—gives growing companies senior security leadership without a full-time hire. Blaze can own the program, support your team, and bring in offensive-security specialists when technical validation is needed.

Enterprise sales pressure
Security questionnaires, trust evidence, and customer due diligence are slowing opportunities or creating more demand than your team can absorb.
- Security policies & procedures
- Risk assessment framework
- Vendor security program
- Incident response plan

Compliance without an owner
Compliance management for SOC 2, ISO 27001, and other requirements needs a clear owner.
- Questionnaire completion
- Trust center setup
- Evidence collection
- Response library building

Security priorities keep slipping
Cyber risks, governance, policies, and remediation compete with day-to-day delivery.
- Gap assessments
- Compliance roadmaps
- Auditor liaison
- Evidence preparation

Boards need clarity
Leaders and investors need concise reporting on exposure, progress, and decisions.
- Quarterly security reviews
- Risk dashboards
- Investor due diligence support
- Security metrics & KPIs
What your Fractional CISO can own
The service scope follows your priorities, internal team, and required level of ownership.

Security strategy and roadmap
Turn business goals, cyber threats, cyber risks, and customer commitments into a prioritized plan with owners.
Compliance program leadership
Coordinate control owners, evidence, auditors, implementing controls, and ongoing maintenance for the standards and regulations in scope.
Customer assurance
Handle questionnaires, organize reusable evidence, and support customer or investor security reviews.
Policies and governance
Develop practical policies, decision rights, and governance processes your employees and leadership team can follow.
Risk management and executive reporting
Translate risk assessments, material exposure, progress, and tradeoffs into decisions executives and boards can act on.
Technical security coordination
Use Blaze penetration testing and security specialists when architecture, controls, or technical risk need independent validation.
Fractional CISO engagement models
Choose the ownership and support level that fits your team. Scope can expand or contract as priorities, regulations, and internal capabilities change.
Advisor
Senior direction
- Strategy and roadmap reviews
- Executive risk guidance
- Compliance and customer assurance
- Defined working cadence
Managed
Program ownership
- Security program ownership
- Policies, risk, and governance
- Questionnaire and audit coordination
- Executive reporting
- Vendor guidance
Embedded
Embedded leadership
- Leadership team integration
- Multi-workstream management
- Board and auditor engagement
- Customer security support
- Technical specialist coordination
- Incident preparedness
Frequently asked questions

Ready for accountable security leadership?
Give your cybersecurity program a clear owner and operating cadence—without hiring a full-time CISO too early.
