Penetration testing services built around real attack paths
Organizations worldwide
Weeks to start, on average
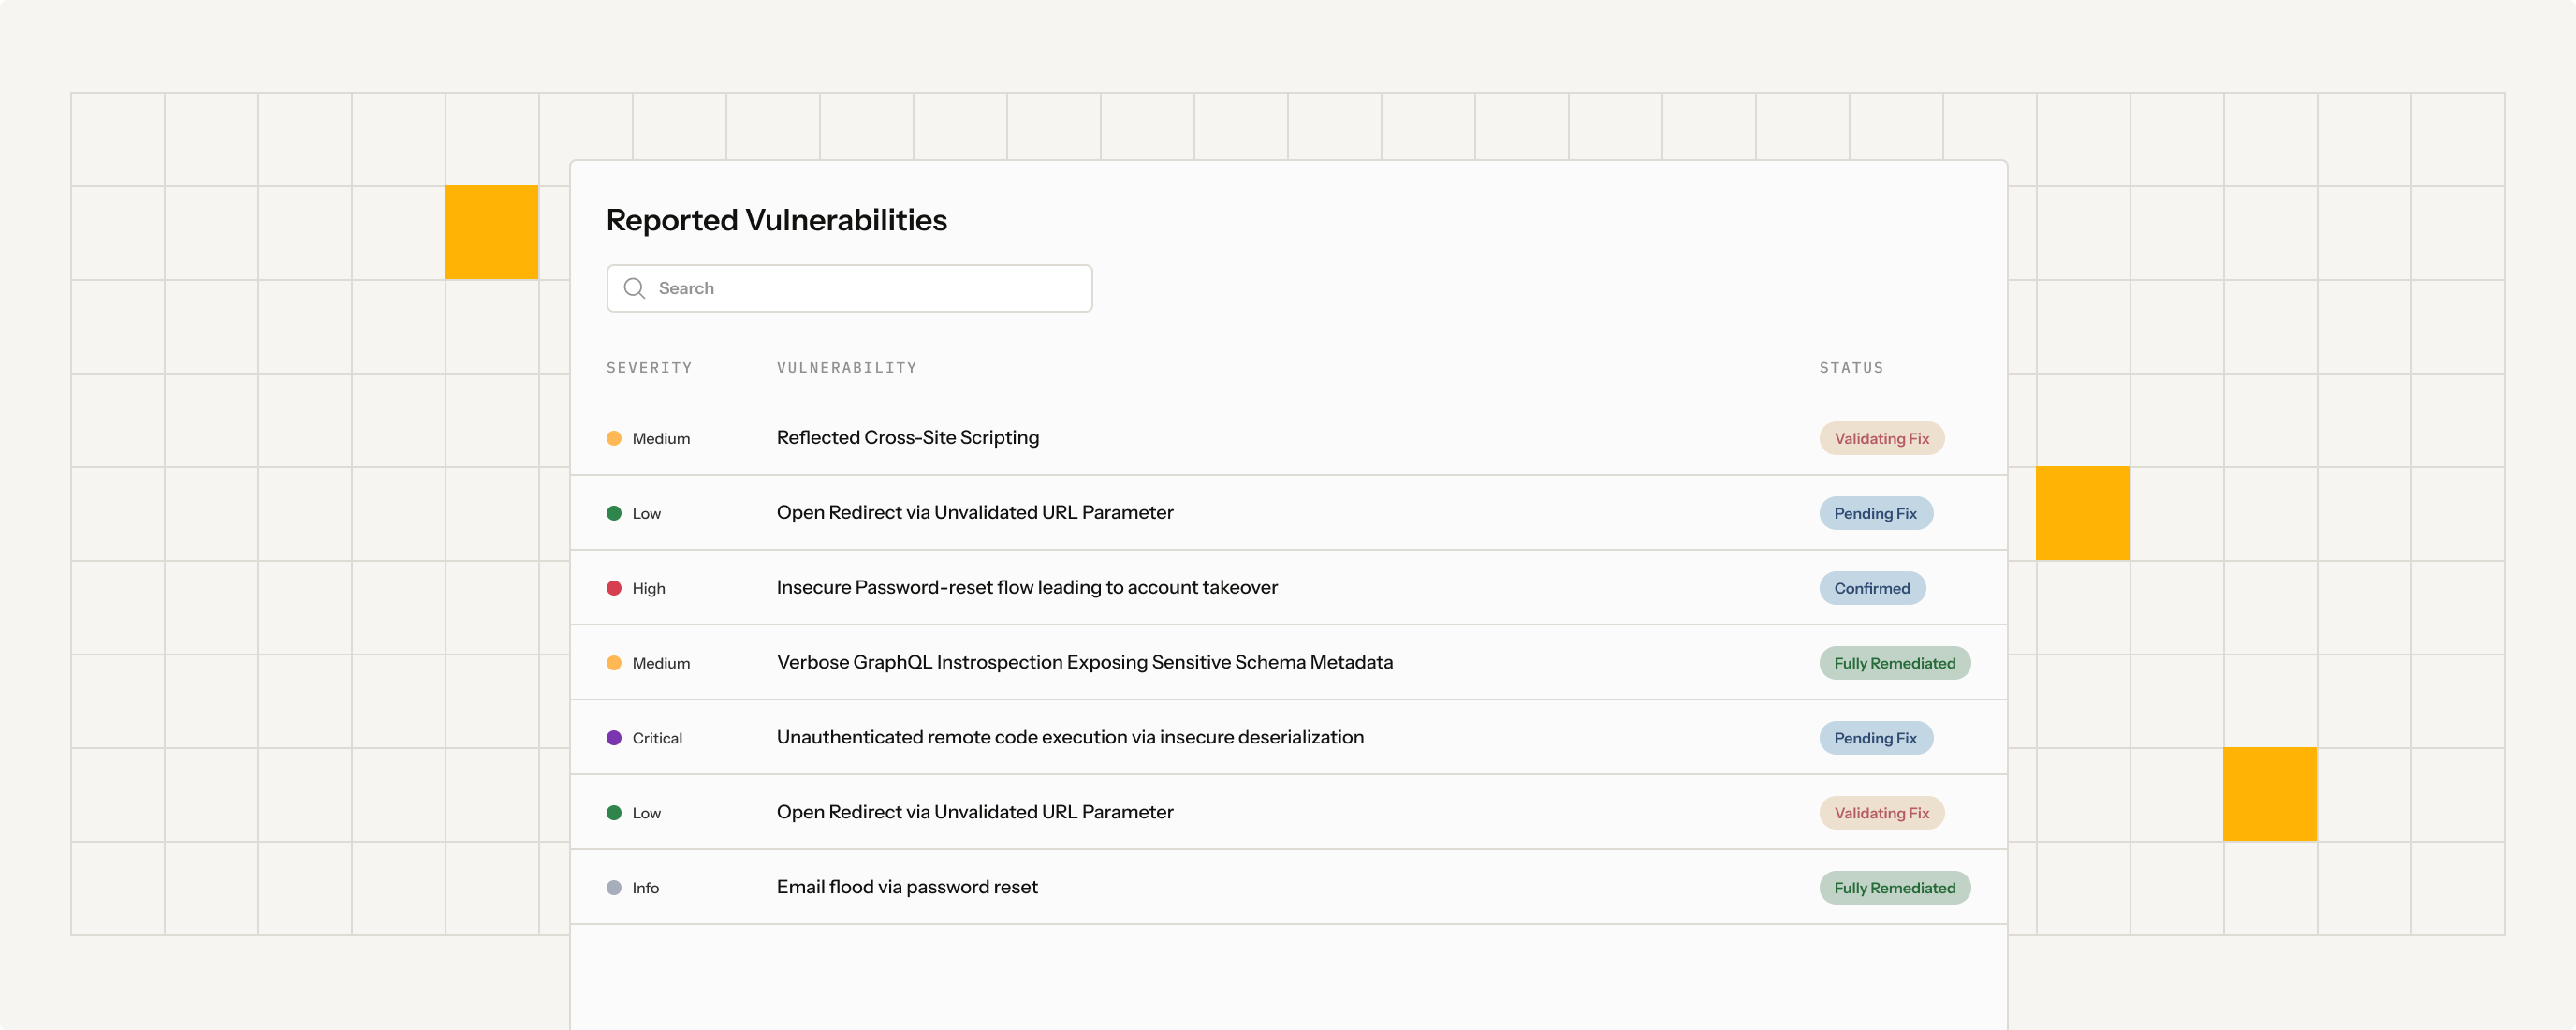
Findings manually validated
Findings in the Blaze Portal
Penetration testing services for web applications, APIs, mobile, cloud, and networks. We validate real attack paths and deliver findings your engineers can fix.
Trusted by 400+ organizations worldwide — from startups to global enterprises.
Penetration testing services across your attack surface
Our penetration testing services are shaped around your architecture, user roles, trust boundaries, and highest-risk attack paths.

Web application penetration testing
Test access controls, tenancy boundaries, sessions, business logic, injection paths, file handling, and application-specific abuse cases.

API penetration testing
Assess REST, GraphQL, gRPC, and WebSocket APIs for authorization failures, authentication weaknesses, data exposure, rate-limit abuse, and business-logic flaws.

Mobile application penetration testing
Test iOS and Android apps across platform controls, authentication, local storage, cryptography, reverse engineering, and backend APIs.

Cloud penetration testing
Assess AWS, Azure, and GCP identities, permissions, exposed services, configuration weaknesses, privilege escalation, and lateral movement.

Network penetration testing
Test external, internal, hybrid, and wireless networks for exposed services, credential paths, segmentation failures, privilege escalation, and lateral movement.

Manual pentest, with AI used where it helps
We use AI selectively to speed up repetitive analysis and expand coverage. Researchers control the assessment, validate every finding, and pursue the attack paths that require human judgment.
Beyond automated scanning
Researchers test roles, workflows, trust boundaries, business logic, and chained attack paths in the context of your system.
Independent security evidence
Document the scope, methodology, confirmed findings, and remediation status for customers, auditors, procurement teams, and internal stakeholders.
Specialist capacity when you need it
Add focused offensive-security expertise for a release, annual assessment, customer deadline, or broader testing program.
Testing matched to your release cycle
Choose a point-in-time assessment, release-based testing, or a recurring program as your attack surface changes.
Why security teams choose Blaze for penetration testing
Hands-on testing, direct researcher access, live findings, and reports your engineers can act on.
Hands-on pentesting
Researchers control testing, reproduce every issue, and confirm its real-world impact before reporting it.
Direct researcher access
Speak directly with the experts testing your systems, from kickoff through remediation.
Validated findings as testing progresses
Confirmed findings appear in the Blaze Portal, with critical issues escalated immediately.
Remediation built into delivery
Discuss fixes directly with researchers. When included, agreed remediations are retested and reflected in the report.
Reports for engineers and stakeholders
Receive a report with validated findings, reproduction steps, business impact, and remediation guidance—plus an executive summary for stakeholders.
Dates agreed before testing begins
Confirm the testing window and report date during scoping, based on scope, readiness, availability, and your deadline.
How our penetration testing process works
Methodical testing. Compliance-aware reporting.
We use standards relevant to your technology and threat model, then map confirmed findings where appropriate. A pentest provides evidence; it does not create compliance.
OWASP Top 10
Common web application security risk categories.
OWASP ASVS
Application security verification requirements.

Compliance support
Relevant findings can be mapped to SOC 2, ISO 27001, PCI DSS, HIPAA, and other applicable frameworks.
OWASP MASVS
Mobile application security requirements.
PTES
Penetration testing execution methodology.
NIST SP 800-115
Technical security testing and assessment guidance.
CWE Top 25
High-impact software weakness categories.
Pentest services shaped around your environment

SaaS and technology
Test multi-tenant applications, authorization boundaries, APIs, cloud environments, integrations, and fast-changing products.

Banking and fintech
Assess payment flows, transaction logic, identity systems, APIs, mobile applications, and cloud environments.

Healthcare
Test patient portals, APIs, mobile apps, identity boundaries, and exposure of sensitive health information.

Enterprise procurement
Produce independent security evidence for customer reviews, questionnaires, renewals, audits, and enterprise deals.
What clients say about working with Blaze
Blaze Infosec was very professional in handling our request and the changes that came along with it.
Penetration testing FAQs
Straight answers about scope, timing, retesting, and standards.
Testing and reporting timelines depend on the agreed scope, access, complexity, and environment readiness. We confirm the testing window and report delivery date during scoping, before the engagement begins.