A Microsoft 365 security assessment that finds what your Secure Score misses
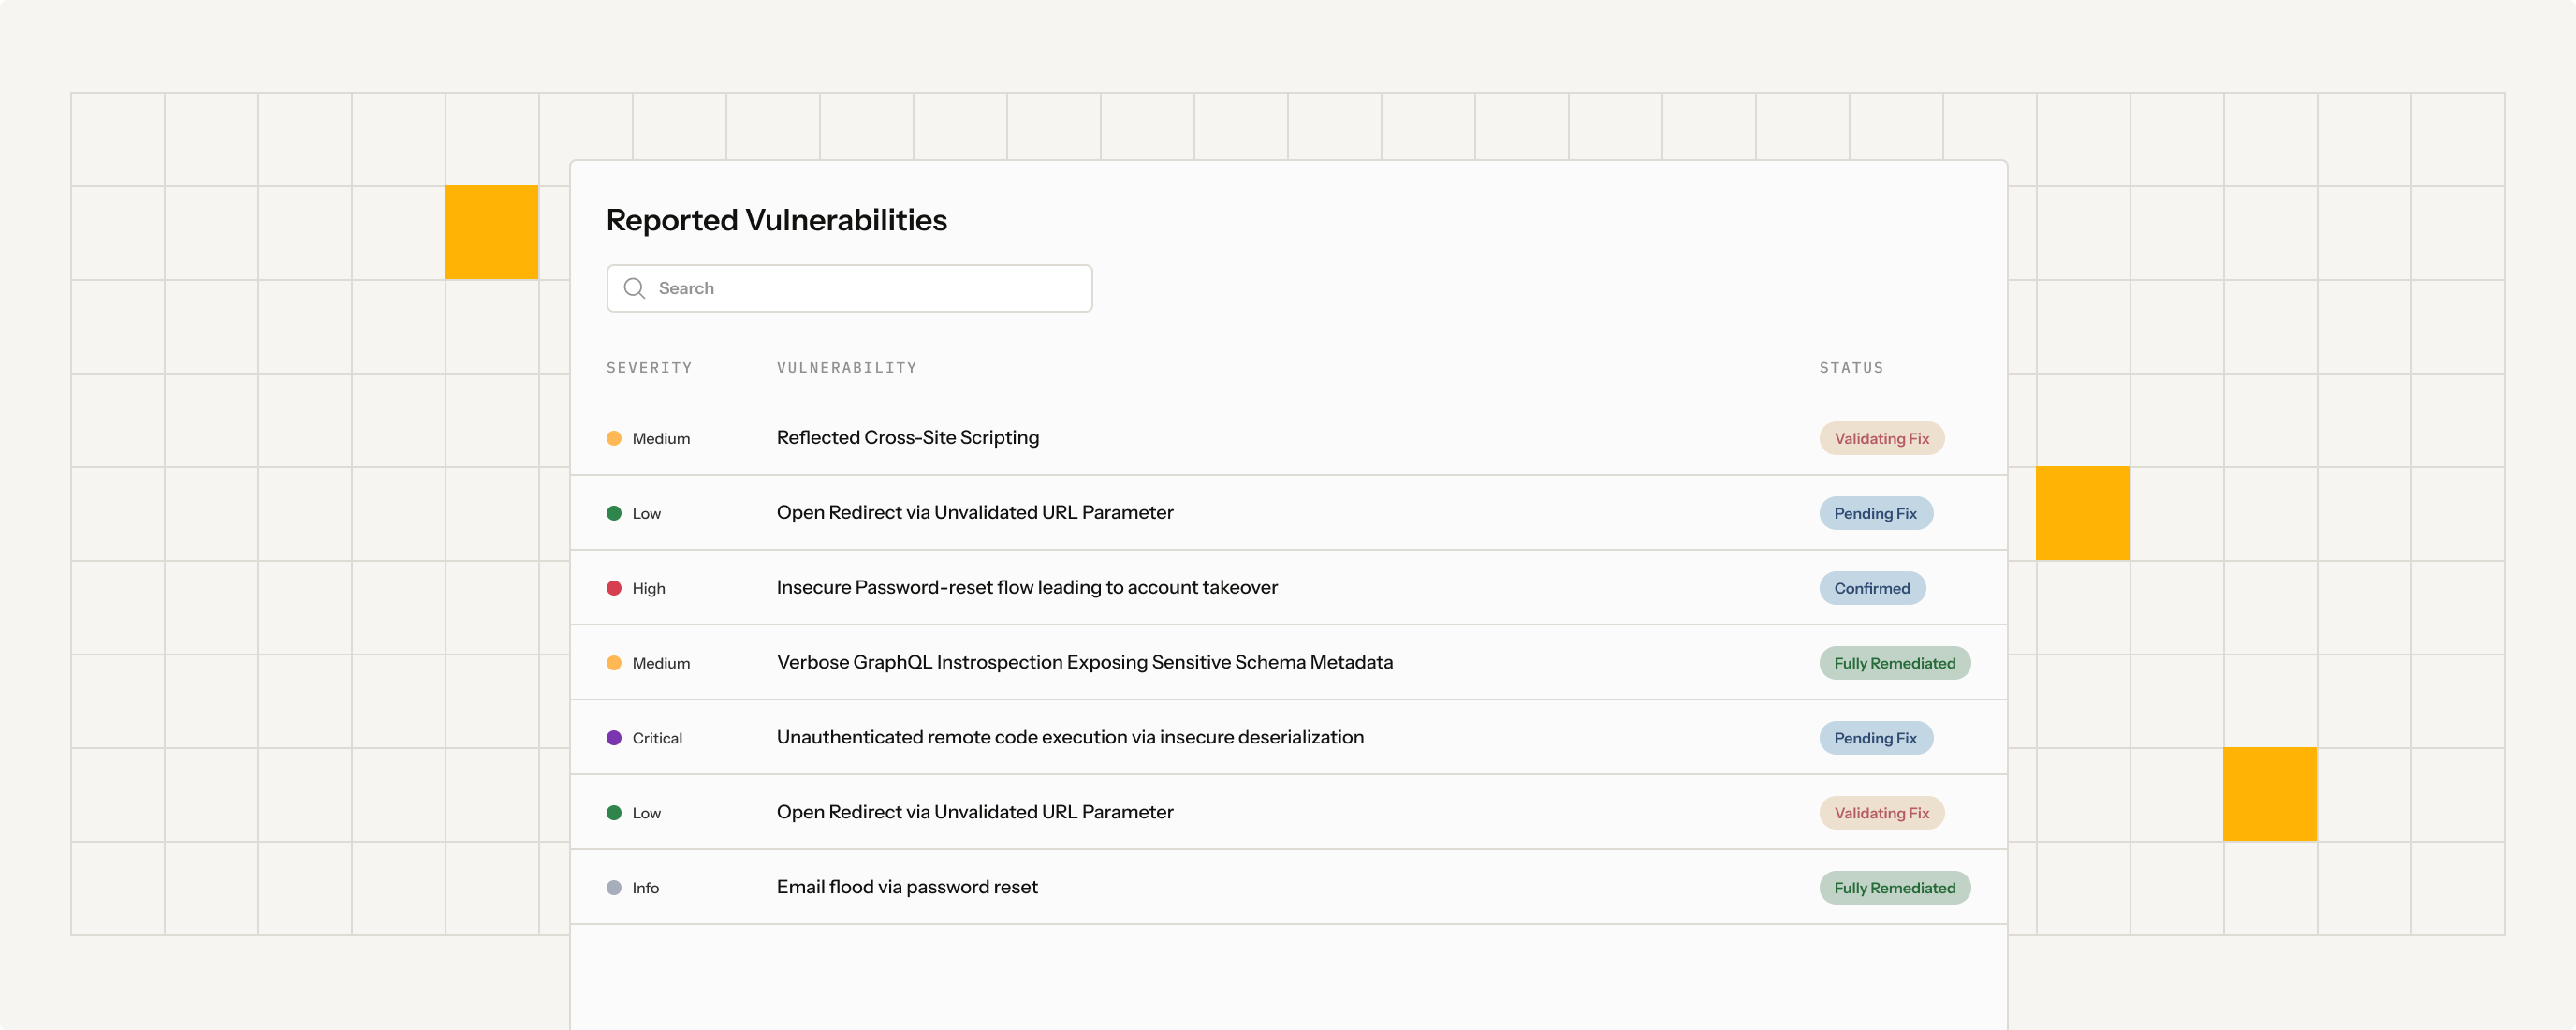
Blaze assesses your Microsoft 365 and Entra ID tenant from an attacker's perspective, finding the identity, email, OAuth, and configuration gaps that create real takeover paths.
Audits completed
Avg issues found
Days typical turnaround
Remediation guidance
Most M365 "audits" read your Secure Score back to you. Blaze runs an offensive Microsoft 365 security assessment of your Entra ID and tenant — finding the identity, email, and configuration gaps an attacker would actually use to take it over, and mapping the real path from initial access to full tenant compromise.
CREST-Certified | CIS Microsoft 365 Benchmark | Entra ID | Defender for Office 365








Secure Score shows settings. We show attack paths.
Automated checks show configuration gaps. Blaze tests how conditional access, app permissions, legacy authentication, and sharing controls combine into exploitable paths.
Microsoft 365 workloads
SharePoint & OneDrive
Microsoft Teams
Intune
Defender for Office 365
Entra ID & identity
MFA & authentication methods
Privileged roles
App registrations & service principals
Guest / B2B access
What our Microsoft 365 security assessment covers
Aligned to the CIS Microsoft 365 Foundations Benchmark and tested from an attacker's perspective.

Identity & Entra ID
Conditional access, MFA coverage, legacy authentication, privileged roles, and guest access.
App registrations & OAuth
Over-permissioned apps, consent grants, and service-principal abuse paths.
Email & Defender for Office 365
Phishing resilience, transport rules, forwarding abuse, and anti-spoofing (SPF/DKIM/DMARC).
Data & sharing
SharePoint, OneDrive, and Teams external-sharing exposure and DLP gaps.
Device & conditional access
Compliance policies and access controls that actually gate risky sign-ins.
Logging & monitoring
Review audit logging, alerting, and Secure Score context to determine whether attacks would be detected.
What you get
Benchmark-mapped report
A prioritized findings report mapped to the CIS Microsoft 365 Benchmark.
Real attack paths
Demonstrated takeover paths with clear evidence.
Actionable remediation
Clear, step-by-step fixes your IT team can action without breaking users.
Fix validation
Re-verify agreed fixes and document the hardened state when validation is included.
Your identity backbone is your biggest attack surface
Microsoft 365 often controls identity, email, files, and access to other systems. An offensive assessment tests whether those controls hold and provides useful audit evidence.
How attackers chain Microsoft 365 weaknesses
1. Get in
Phishing, password spray, or legacy auth bypasses weak or missing MFA.
2. Escalate
Abuse an over-permissioned app or a misconfigured privileged role.

Compliance Support
Our pentests satisfy the technical requirements for major compliance frameworks:
3. Persist
Add consent grants, forwarding rules, or rogue app registrations.
4. Reach the data
Access mailboxes, SharePoint, Teams, and connected applications before anyone notices.
NIST Cybersecurity Framework
Identify, Protect, Detect, Respond, Recover methodology applied to cloud configurations
ISO 27001 Controls
Relevant Annex A controls mapped to Microsoft 365 and Entra ID findings for audit and remediation evidence.
Frequently asked questions

Ready to find the attack paths in your Microsoft 365 tenant?
Get an assessment scoped to your Microsoft 365 and Entra ID environment, with prioritized findings and a practical hardening plan.
