Penetration testing as a service for continuous delivery
Launch penetration tests around releases and security milestones. See validated findings as testing happens, route remediation into your workflow, and use annual credits across applications, APIs, cloud, and infrastructure.
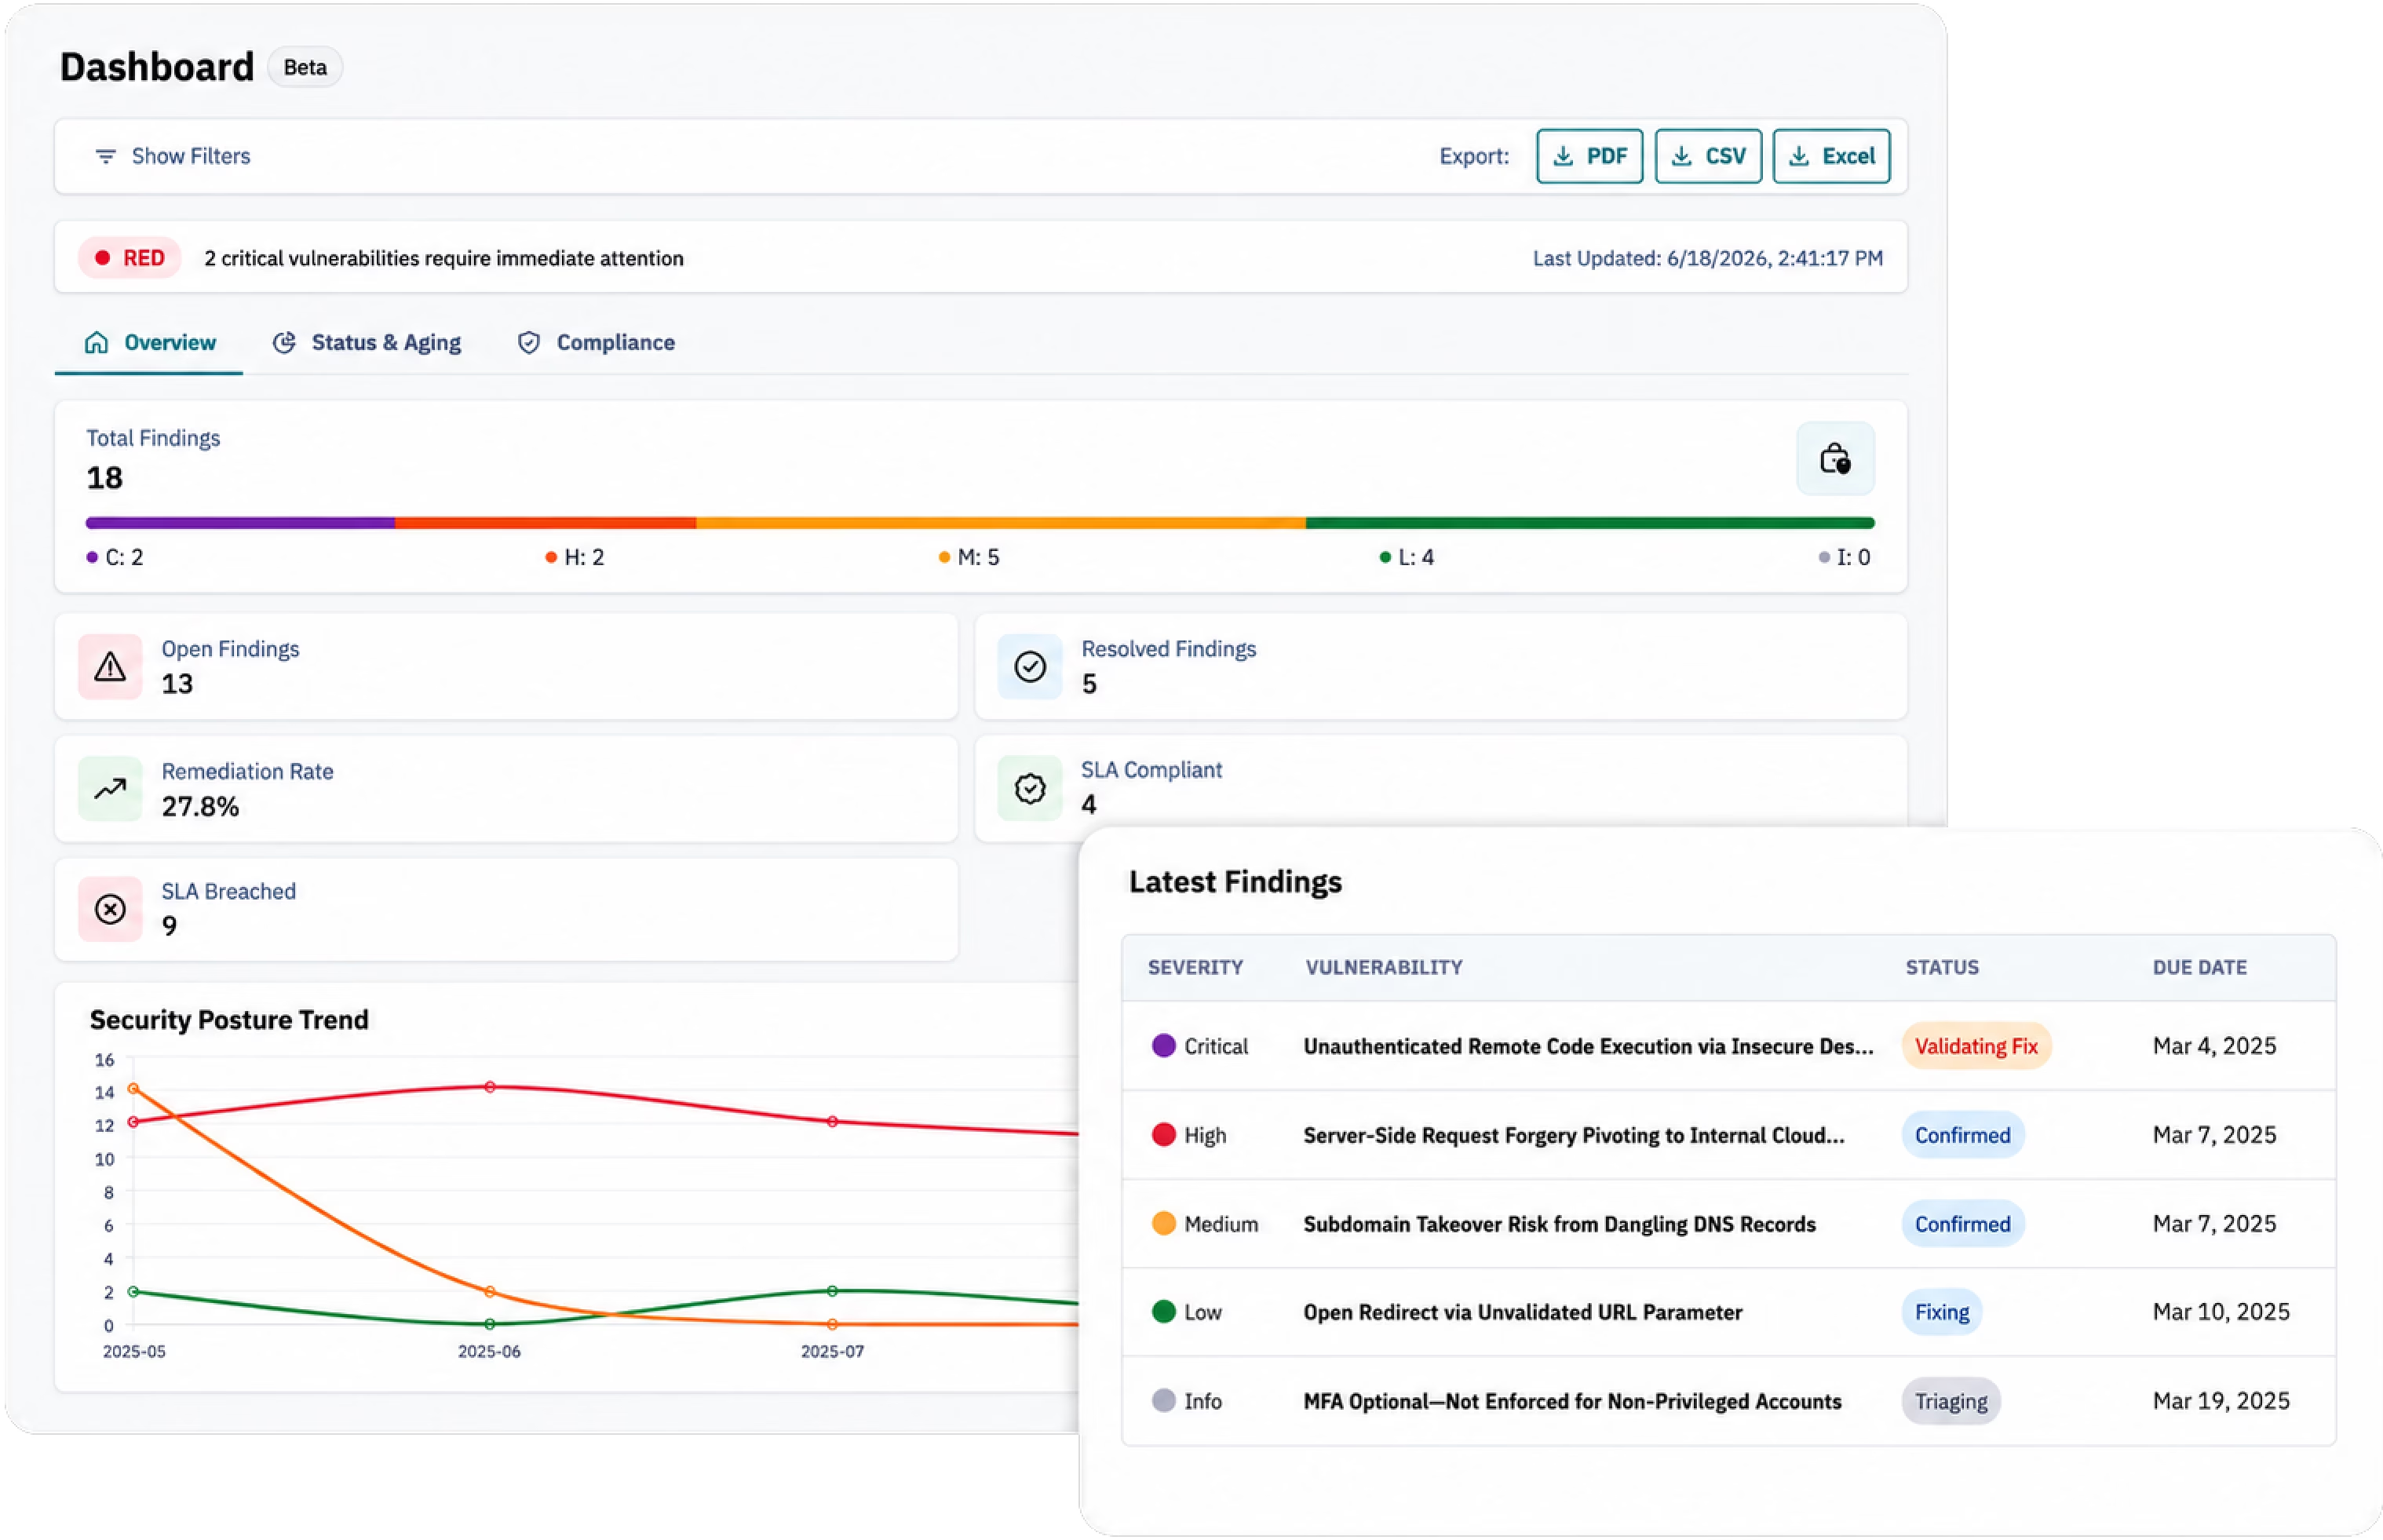
Penetration testing
Validated findings
Fix validation
Annual credits
What is penetration testing as a service (PTaaS)?
Penetration testing as a service (PTaaS) combines manual security testing with AI and a platform for scoping assessments, viewing validated findings, collaborating on remediation, and managing evidence across multiple engagements. Blaze uses annual credits to plan continuous penetration testing around releases, new assets, and assurance deadlines.
 Manual testing for apps, APIs, cloud, and infrastructure
- Findings delivered as researchers validate them
- Remediation tracked in your existing workflows
- Consistent delivery and reporting across engagements
Why one-off pentests fall behind product change
Point-in-time tests still matter. The problem is rebuilding scope, scheduling, delivery, and remediation every time the product or assurance calendar moves.

Testing lag
Release schedules move faster than one-off testing cycles, leaving new changes outside the last assessment.

Procurement drag
Repeated scopes, approvals, and vendor handoffs slow testing before it begins.

Lost context
Switching teams between engagements means architecture and risk priorities must be rebuilt.

Remediation friction
Static reports separate findings from the engineering work needed to close them.
Why teams choose Blaze PTaaS

Expert researchers, direct access
Work with named testers who understand the scope and can discuss findings with your team.
Testing when priorities change
Use annual capacity across agreed scopes as products, releases, and assurance needs evolve.
Validated findings, delivered live
See findings in the Blaze Portal as researchers confirm exploitability and impact.
Fix validation included
Submit agreed remediations for validation without starting a separate engagement.
Evidence across engagements
Keep reports, findings, and remediation status together for audit and customer assurance.
Workflow-ready delivery
Route confirmed findings into supported engineering, collaboration, and compliance tools.
AI expands coverage. Experts prove the risk.
AI assists selected discovery and analysis so researchers can spend more time on complex attack paths. Expert testers control the methodology, validate every delivered finding, and assess the business logic and exploitation that automation cannot judge reliably.
How Blaze PTaaS works
Plan capacity once, then launch scoped tests as priorities change.
PTaaS vs project-based penetration testing
Both use expert testing. PTaaS adds an operating layer for repeatable delivery, live findings, and program management.
PTaaS: planned around releases
Project-based: scoped per engagement
Time to start
Capacity and scheduling planned in advance
Scheduling arranged per project
Findings
Shared as researchers validate them
Commonly delivered at close
Fix validation
Included for agreed findings
Defined per engagement
Integrations
Supported engineering and GRC workflows
Depends on provider
Who tests you
Named expert researchers
Depends on delivery model
Program evidence
History across engagements
Engagement by engagement
Connect PTaaS to your remediation workflow
Move validated findings into supported engineering, collaboration, and compliance tools without rebuilding them from a PDF.

Jira / Linear
Create tickets with severity, evidence, reproduction steps, and fix guidance.

Slack
Share critical finding alerts and coordinate with your Blaze team.

GitHub / GitLab
Track remediation alongside the code and issues your engineers already manage.

Webhooks
Connect supported events and findings to internal workflows.

SSO / SAML
Use enterprise authentication for controlled portal access.

API access
Use findings data in supported internal dashboards and workflows.
Annual PTaaS plans
Choose 15, 30, or 50 annual credits. Additional credits are $1,099 each in packs of five.
Starter
$19,999
15 credits
- 15 credits, valid for 12 months
- Expert-led pentest assessments
- Audit-ready report and attestation
- Email support and findings clarifications
- Debriefing call
- Usage tracking and project summary
- 90-day fix validation
Growth
$35,999
30 credits
- 30 credits, valid for 12 months
- Everything in Starter
- Named project manager
- Quarterly recap
- Slack channel
- 20% credit rollover
- 90-day fix validation
Scale
$53,999
50 credits
- 50 credits, valid for 12 months
- Everything in Growth
- Fast-track start
- Named project manager
- Slack channel
- Annual strategic pentest roadmap
- 30% credit rollover
Need more than 50 credits or a tailored testing cadence?
Talk to sales about a custom PTaaS plan.
Frequently asked questions
Clear answers on scope, delivery, evidence, and how Blaze PTaaS fits an ongoing testing program.

Build a penetration testing program that keeps moving
Plan annual capacity around your products, releases, and assurance needs—then launch each scoped test when the business is ready.
