Web application penetration testing is an authorized security assessment that simulates real attacks against a web application to find exploitable vulnerabilities before attackers do. A strong web app pentest goes beyond automated scanning by testing authentication, authorization, business logic, session handling, input validation, APIs, and the OWASP Top 10 using a structured methodology such as the OWASP Web Security Testing Guide.
For SaaS, B2B and B2C internet-facing platforms, a web application pentest can support compliance evidence, customer security reviews, vendor assessments, and enterprise sales. Requirements depend on the applicable framework, scope, contracts, and risk assessment; SOC 2 and ISO 27001 do not impose a universal pentest mandate. It gives security and engineering teams evidence of what is exploitable, how severe each issue is, and what needs to be fixed first.
At Blaze Information Security, we conduct hundreds of SaaS and web application penetration testing assessments every year. Our 2025 Annual Penetration Testing Review analyzed 660 penetration tests across 145 organizations, identifying 3,294 confirmed vulnerabilities across those engagements. That experience shows a clear pattern: modern web application risk is usually concentrated around identity, authorization, APIs, sensitive data exposure, and business logic.
This guide is for security managers, engineering leads, and teams commissioning an assessment. It explains what web application penetration testing is, what it includes, how it differs from vulnerability scanning, how to prepare, which methodologies matter in 2026, what tools are commonly used, how long a test takes, and what to expect from a high-quality report.
What is web application penetration testing?
Web application penetration testing is a controlled security assessment designed to evaluate a web application's resistance to real-world attacks. During a web app pentest, security engineers examine the application for vulnerabilities that could allow unauthorized access, data exposure, account takeover, privilege escalation, payment abuse, business logic abuse, or compromise of connected systems.
Unlike a basic vulnerability scan, a penetration test does not stop at listing possible issues. A pentester verifies findings, attempts safe exploitation, evaluates impact, chains weaknesses where relevant, and documents practical remediation steps for engineering teams.
A web application penetration test typically examines five core areas:
Identity and access control: Authentication, authorization, session management, SSO, SAML, OAuth, OpenID Connect, SCIM, invitation flows, and role-based access control.
Application and API behavior: REST, GraphQL, WebSocket, backend API endpoints, user input handling, server-side validation, and business logic abuse cases.
Sensitive workflows: Payments, checkout flows, subscriptions, admin actions, file uploads, file downloads, exports, previews, and privileged operations.
Data protection and browser-side controls: Sensitive data exposure, encryption use, security headers, client-side controls, and browser-side protections.
Operational security: Third-party integrations, logging, monitoring, error handling, and alerting for suspicious or unauthorized activity.
The primary goals and tangible benefits of web application penetration testing include:
Identifying exploitable security weaknesses: A web app pentest uncovers vulnerabilities in design, implementation, configuration, access control, and business logic.
Evaluating security controls: Testing shows whether controls such as authentication, authorization, encryption, rate limiting, input validation, and session management work under attack conditions.
Supporting compliance evidence: Web penetration testing can contribute scoped technical evidence for frameworks and regulations such as GDPR, HIPAA, SOC 2, ISO 27001, and PCI DSS, alongside the organization’s wider controls and audit obligations. A pentest alone does not establish compliance.
Providing actionable recommendations: A good report includes severity, business impact, affected endpoints, reproduction steps, proof-of-concept evidence, and specific remediation advice.
Integrating security into the software development life cycle (SDLC): Findings from a web app pentest help engineering teams fix current issues and improve secure coding, code review, threat modeling, and release processes.
Maintaining customer trust and brand integrity: Regular penetration testing demonstrates that your organization takes application security seriously, especially when selling to enterprise customers or handling regulated data.
Cost-effective and proactive risk management: Addressing vulnerabilities post-attack can be costly. Penetration testing proactively identifies and resolves security weaknesses, making it a cost-effective strategy for risk management.
Prioritizing security investment: Penetration testing helps teams focus on real, exploitable risks rather than long lists of theoretical scanner alerts.
Web application penetration testing vs. web application vulnerability scanning
A vulnerability scan is not the same as a web application penetration test. Both are useful, but they answer different questions. A vulnerability scanner asks, "What known issues might exist?", whereas a web application penetration test asks, "What can an attacker actually do?"
Automated scanners are useful for identifying common misconfigurations, missing headers, outdated components, exposed files, known CVEs, and some injection patterns. They are fast, repeatable, and helpful for continuous monitoring. Vulnerability scanning is also useful for compliance programs, including SOC 2 security monitoring and remediation workflows.
A human-led web application penetration test goes deeper. It evaluates how the application behaves in context. For example, a scanner may miss that a standard user can modify another customer's invoice by changing an ID in an API request. It may also miss logic flaws such as bypassing a checkout flow, abusing a password reset process, escalating privileges across tenant boundaries, or chaining a low-severity XSS with weak session controls.
For mature security programs, the strongest approach is not "scanner or pentest." It is both. Use continuous vulnerability scanning, then run web app pentests before major releases, after significant architectural changes, during compliance cycles, and when onboarding major enterprise customers.
Static application security testing (SAST) analyzes source code without executing the application, while dynamic application security testing (DAST) probes a running application. Both can support the software development life cycle, but neither replaces a scoped pentest of authenticated roles, workflows, and business logic. Agree whether source code review or automated scanning is included in the proposed engagement.
Preparing for a web application penetration test
Give the penetration testing team enough access and context to assess the agreed application scope. Missing accounts, incomplete API documentation, or an unstable environment can reduce coverage and delay delivery.
Before the pentest begins, agree confidentiality terms and written authorization, then prepare:
Targets and boundaries: Application URLs, API endpoints, environments, third-party dependencies, exclusions, and sensitive or destructive actions that need separate approval.
Accounts and roles: Working accounts for each relevant role, including administrators where authorized. For a multi-tenant application, provide separate test tenants so the team can assess cross-customer access.
Documentation and workflows: Architecture context, API schemas or collections, sample requests, authentication details, and important journeys such as invitations, exports, billing, and account recovery.
Environment readiness: Representative test data, working integrations or agreed substitutes, stable builds, and any relevant VPN, allowlisting, WAF, or rate-limit arrangements. Record differences from production.
Operational coordination: Technology-specific information, known limitations, sensitive areas, an emergency contact, communication channels, and the report deadline.
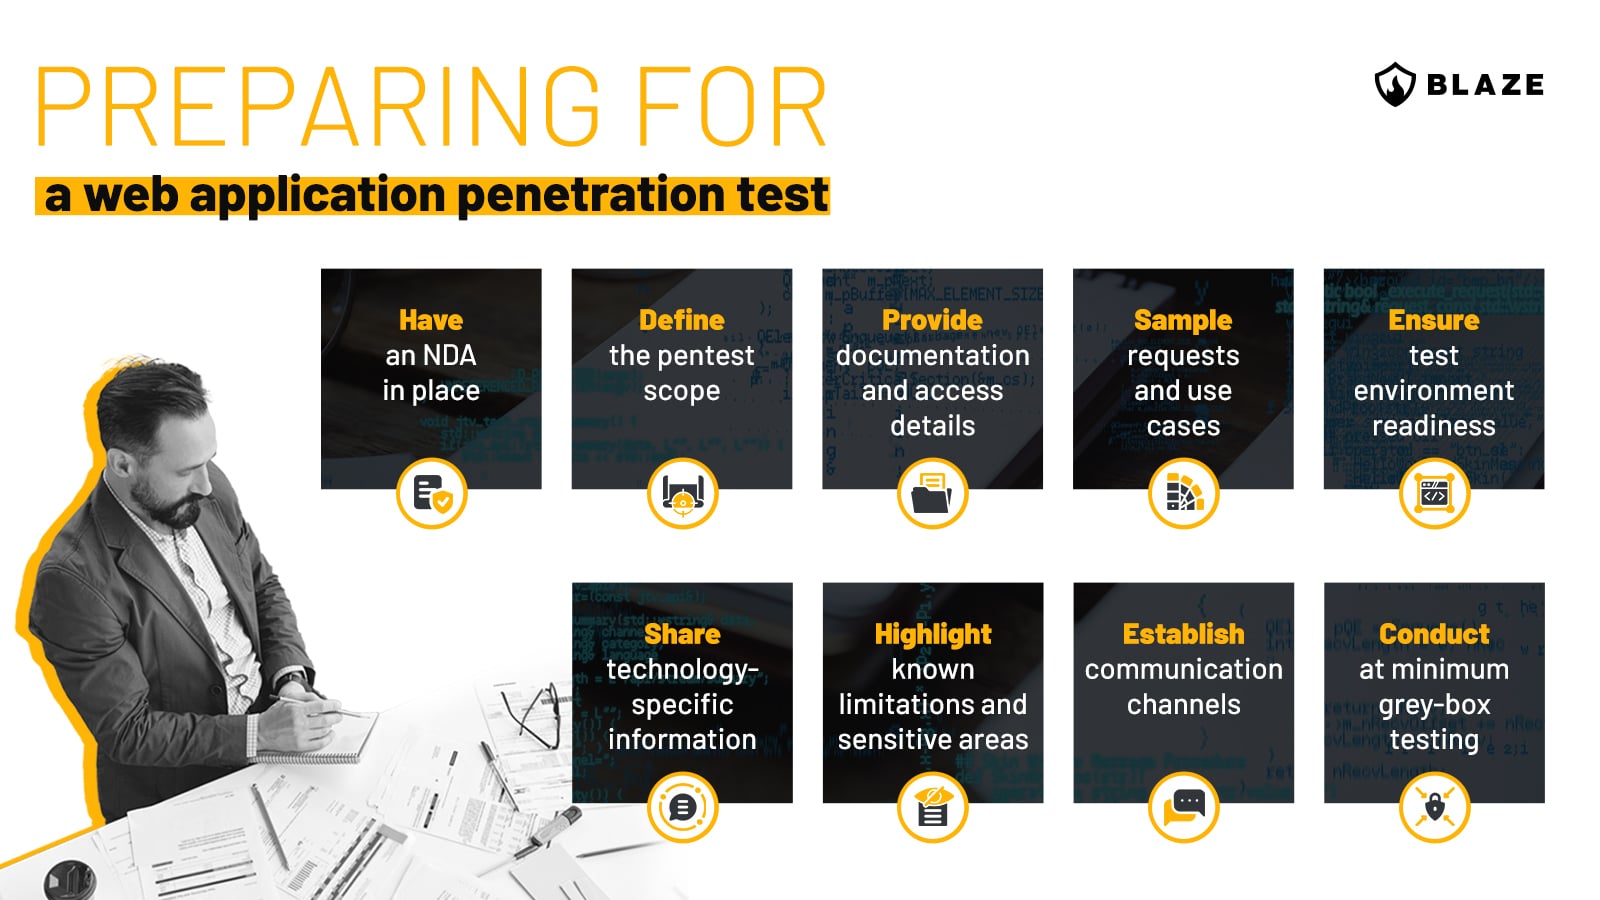
Organizations might opt for a full white-box test for a more in-depth assessment. In this scenario, the penetration testing team is given access to the web application's source code. Source access can help security engineers trace data flows and investigate code paths that are difficult to reach through gray-box or black-box penetration testing. Agree whether source review is included; credentials and documentation are still useful when source access is unavailable.
Which OWASP resources guide web application penetration testing?
The Open Worldwide Application Security Project publishes complementary resources for web application security. A useful proposal explains which resources inform the engagement and how they apply to the application’s roles, architecture, and risk.
Resource | Purpose | How it supports a web app pentest |
|---|---|---|
Awareness of critical web application risk categories | Helps prioritize risks. It is not a complete penetration testing methodology or proof of exhaustive coverage. | |
Methods and scenarios for evaluating web applications and services | Provides structured checks for information gathering, configuration, identity, authentication, authorization, sessions, input validation, cryptography, business logic, and client-side behavior. Version 4.2 is the released guide; version 5.0 is under development. | |
OWASP Application Security Verification Standard (ASVS) 5.0.0 | Verifiable application security requirements | Helps define agreed coverage and evidence. State the applicable version, verification level, and any exclusions rather than implying that every requirement was assessed. |
Practical implementation and remediation guidance | Supports recommendations on controls such as authentication, authorization, session management, and input handling. |
A methodology should also account for application-specific abuse cases. For example, a payment workflow may require checks for repeated discounts or bypassed approval steps, while a multi-tenant SaaS platform needs role and tenant-isolation checks beyond a generic checklist.
Common vulnerabilities in web applications
Web application vulnerabilities can come from insecure design, implementation flaws, misconfigurations, weak access controls, unsafe dependencies, missing validation, and poor assumptions about how users will interact with the system. Blaze's analysis of common penetration testing findings shows that recurring issues often involve identity and authorization issues, sensitive data exposure, insecure configurations, and application-specific logic flaws.
OWASP Top 10 2025 risks in web applications
The OWASP Top 10:2025 provides a useful starting point for understanding the most critical risks associated with modern web applications. For web application penetration testing, it helps security teams and developers prioritize the issues most likely to expose sensitive data, enable account takeover, break tenant isolation, compromise supply chains, or allow attackers to abuse application logic.
A01:2025 — Broken Access Control: Access control failures remain the top web application security risk. These flaws allow users to act outside their intended permissions, such as viewing another customer's data, modifying another user's records, accessing admin functions, bypassing tenant boundaries, or abusing server-side request forgery paths, now consolidated under this category.
A02:2025 — Security Misconfiguration: Security misconfiguration moved up in the 2025 list because modern applications rely heavily on configuration across cloud services, containers, APIs, identity providers, frameworks, and deployment pipelines. Common examples include exposed admin panels, verbose error messages, insecure CORS policies, default settings, missing security headers, overly permissive storage, and unnecessary services.
A03:2025 — Software Supply Chain Failures: This category expands the older "Vulnerable and Outdated Components" risk into a broader supply chain concern. It covers weaknesses in third-party dependencies, open-source packages, build systems, CI/CD workflows, software distribution, package integrity, and dependency trust. In a web app pentest, this means reviewing not only known vulnerable libraries, but also how software artifacts are built, updated, verified, and deployed.
A04:2025 — Cryptographic Failures: Cryptographic failures occur when sensitive data is not properly protected in transit, at rest, or during processing. Examples include weak encryption, missing TLS protections, insecure key management, predictable tokens, poor password storage, exposed secrets, and sensitive data leakage. These flaws can expose personal information, financial data, credentials, healthcare records, or confidential business information.
A05:2025 — Injection: Injection vulnerabilities happen when untrusted input is interpreted as a command, query, expression, or executable instruction. This includes SQL injection, NoSQL injection, command injection, LDAP injection, template injection, and cross-site scripting. Attackers can exploit injection flaws to read or modify data, bypass controls, execute commands, or compromise users.
A06:2025 — Insecure Design: Insecure design refers to weaknesses caused by flawed architecture, missing threat modeling, unsafe assumptions, or business workflows that fail under attack conditions. Examples include bypassable approval flows, weak abuse controls, unsafe trust boundaries, insecure multi-tenant design, and payment or subscription logic that can be manipulated.
A07:2025 — Authentication Failures: Authentication failures occur when login, session, identity, or account recovery controls are implemented incorrectly. Common examples include weak password reset flows, insecure MFA enforcement, predictable tokens, session fixation, excessive session lifetime, insecure cookies, account enumeration, and authentication bypass in APIs or SSO integrations.
A08:2025 — Software or Data Integrity Failures: These failures occur when an application does not properly verify the integrity of software, code, updates, data, or trusted workflows. This can affect CI/CD pipelines, signed updates, plugin systems, serialized objects, deployment artifacts, and data imported from external systems. The result can be unauthorized code execution, tampered data, or compromised application behavior.
A09:2025 — Security Logging and Alerting Failures: Logging without effective alerting is not enough. This category covers missing, incomplete, or ineffective logging and alerting for security-relevant events such as login abuse, privilege changes, suspicious API activity, failed access control checks, data exports, account takeover attempts, and administrative actions. Without proper alerting, attackers can operate longer before detection.
A10:2025 — Mishandling of Exceptional Conditions: This new category focuses on what happens when applications encounter abnormal states, errors, edge cases, failed dependencies, race conditions, unexpected input, or partial system failures. Poor exception handling can cause applications to fail open, expose sensitive information, skip security checks, enter unsafe states, or behave unpredictably under attack conditions.
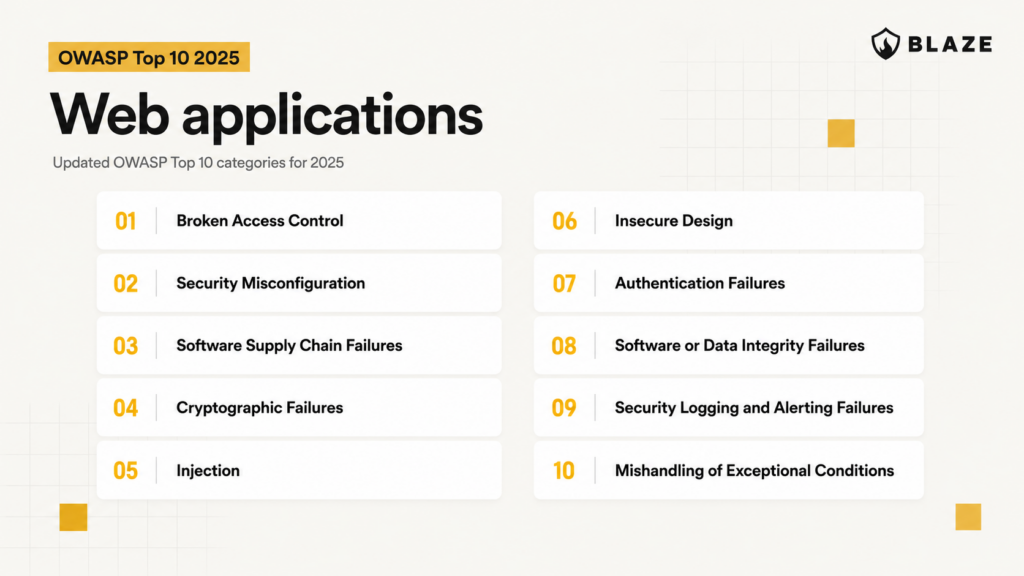
Depending on the application context, OWASP Top 10 2025 risks can lead to data breaches, account takeover, privilege escalation, tenant isolation failure, payment abuse, service disruption, supply chain compromise, regulatory exposure, and reputational damage. Understanding these categories is a useful first step, but a real web application penetration test should go further by identifying more intricate vulnerabilities, verifying their exploitability, assessing business impact, and mapping application-specific attack paths.
Commonly used web application penetration testing tools
Penetration testing tools play an important role in web application security assessments, but tools do not replace human analysis. They help penetration testers intercept requests, map functionality, discover hidden endpoints, fuzz parameters, verify vulnerabilities, and document findings. Some popular tools include:
Burp Suite Professional: A comprehensive web application security testing tool offering automated and manual testing capabilities. It includes features like proxying requests, analyzing traffic, and exploiting vulnerabilities. Alternatives include the open-source ZAP and Caido, which offers free and paid plans and is not currently open source.
ffuf (Fuzz Faster U Fool): ffuf is a highly efficient web fuzzer written in Go. It's used for discovering elements and directories on a web server and is particularly effective for brute-forcing directories and filenames in web applications.
Amass: An advanced tool for subdomain enumeration, useful for discovering external assets associated with a target web application.
Postman: Commonly used for API development, Postman is also valuable for exploring and testing APIs in web applications, helping identify API-related vulnerabilities.
Aquatone: A domain flyover tool that collects screenshots of web-based assets. The original Aquatone repository was archived in January 2023, so it should be treated as a legacy option when selecting an assessment toolchain.
XSStrike: A specialized tool for detecting and exploiting Cross-Site Scripting (XSS) vulnerabilities in web applications. It uses fuzzing and advanced analysis techniques.
SQLMap: An open-source penetration testing tool for automating, detecting, and exploiting SQL injection vulnerabilities in web applications.
Param Miner: A tool for discovering hidden, unlinked parameters in web applications, which can reveal security issues often overlooked. Arjun is also an alternative to Param Miner with similar capabilities.
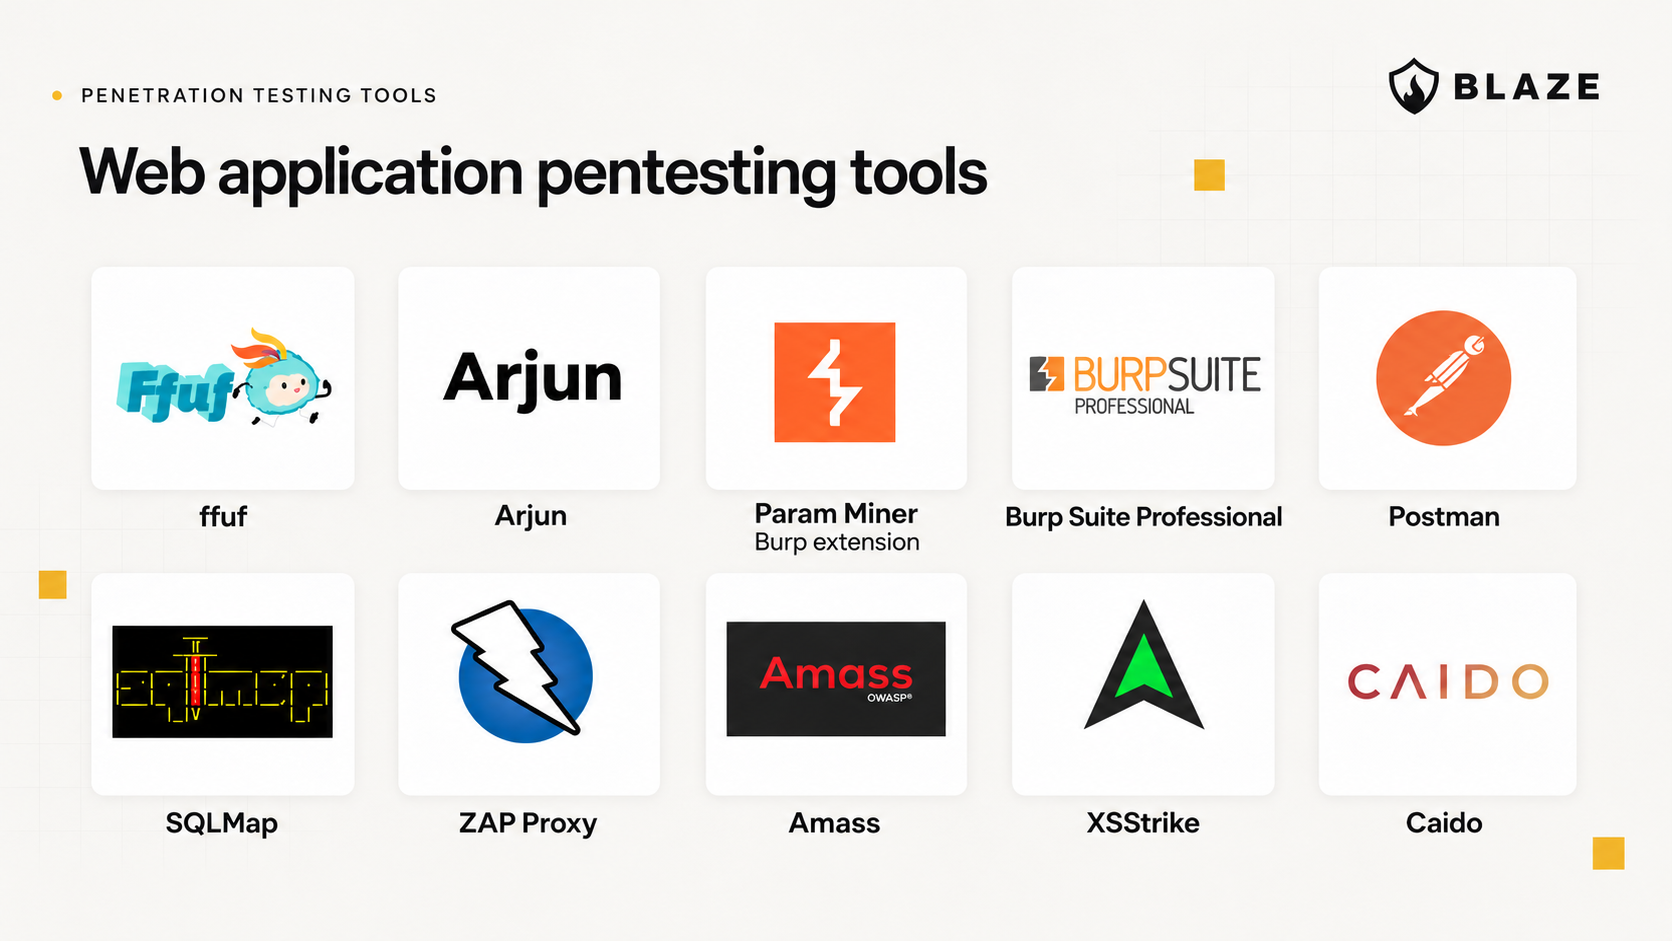
Automated tools help identify potential weaknesses, but security engineers must investigate context, validate exploitability, and assess business impact. AI-assisted analysis can support code investigation and reduce repetitive work, with security engineers checking its output against the code and observed behavior. This does not replace the separate assessment of AI features described below.
Certifications and practical experience for web application pentesting
There's no shortage of penetration testing certifications on the market. For web application work, buyers should consider credentials that demonstrate relevant application security skills, including:
OffSec Web Expert (OSWE – WEB-300)
GIAC Web Application Penetration Tester (GWAPT)
Burp Suite Certified Practitioner (BSCP)
eLearnSecurity Web Application Penetration Tester Extreme (eWPTX)
OffSec Web Assessor (OSWA – WEB-200)
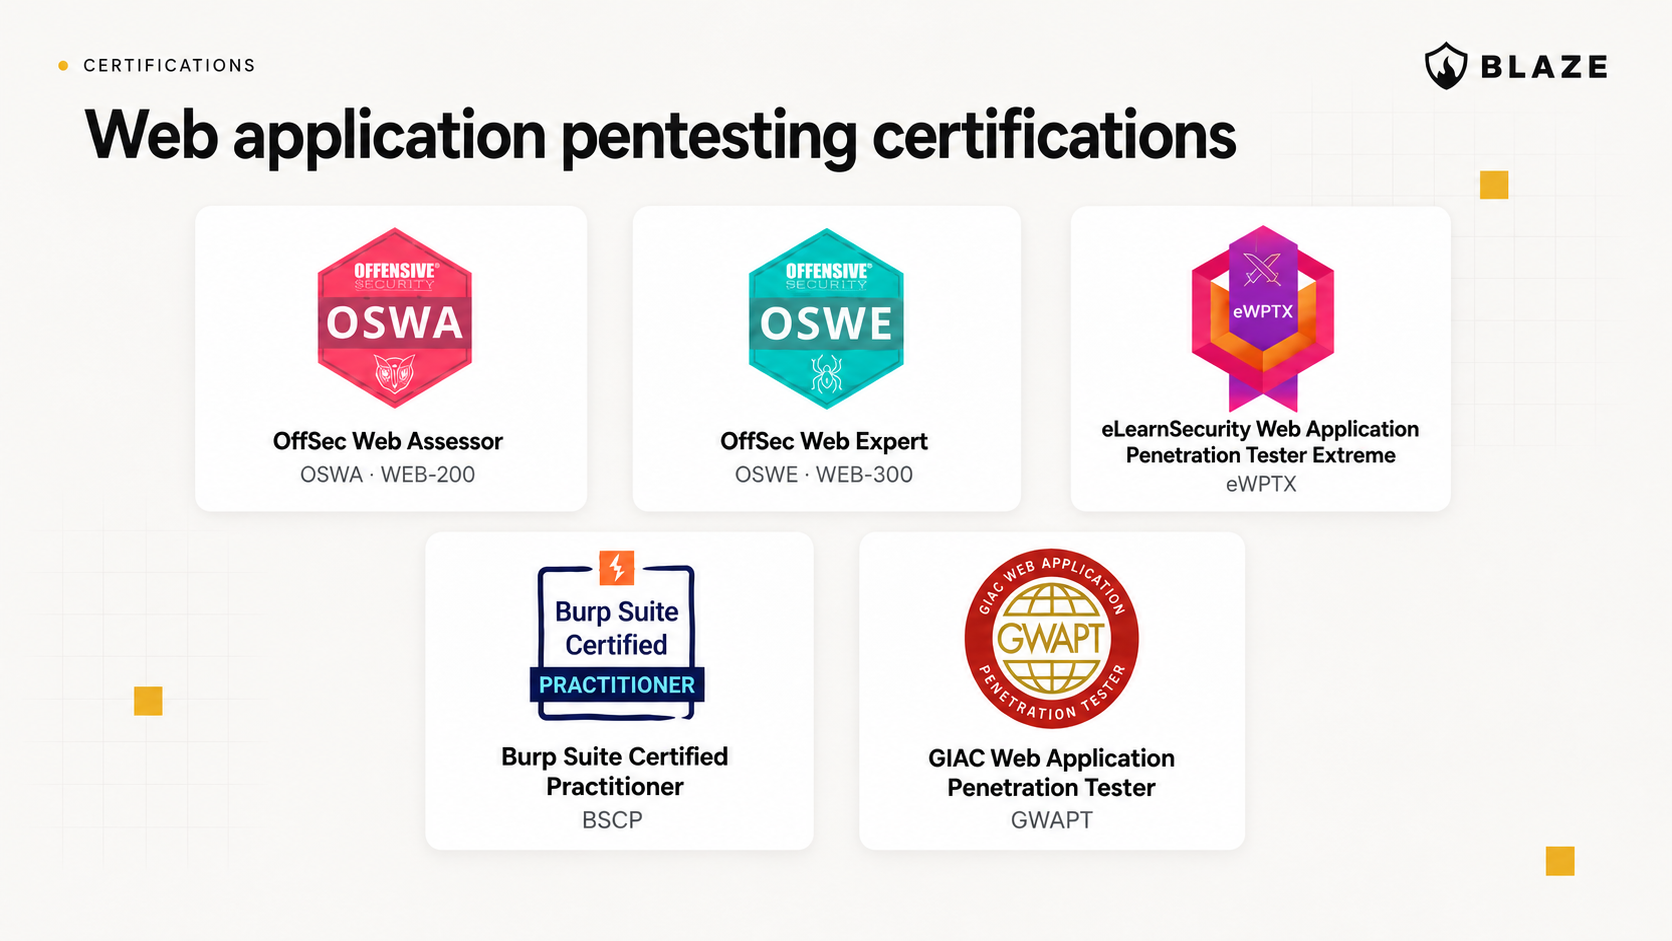
PentesterLab Pro provides practical training labs rather than an equivalent professional certification. Credentials and training are useful signals, but buyers should also evaluate relevant application experience, methodology, sample reporting, and communication.
How long does a web application penetration test take?
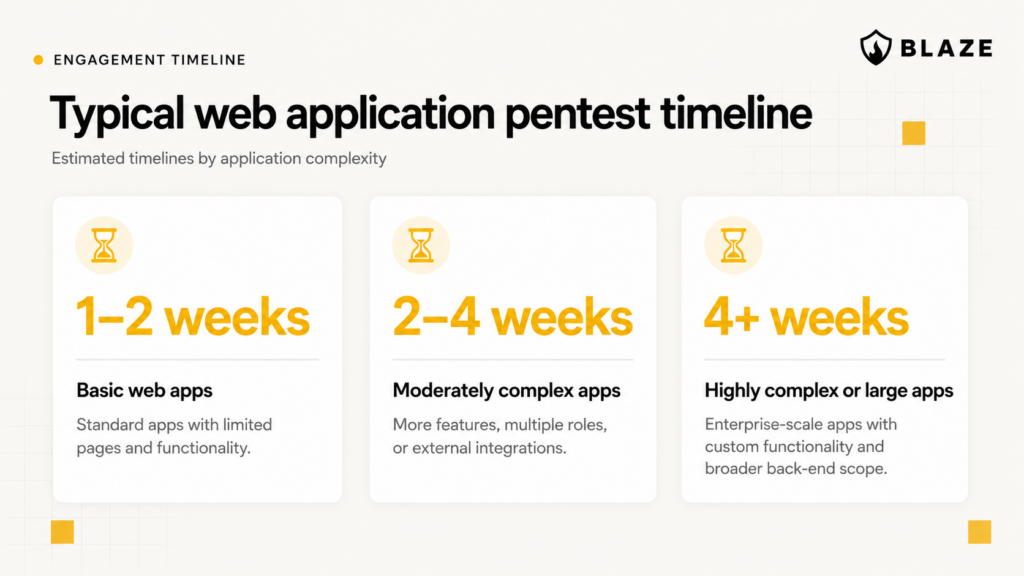
A focused web application pentest may take about one to two weeks; moderately complex applications may need two to four weeks, and large or highly complex platforms can take longer. These are planning estimates, not fixed delivery promises. Confirm the assessment effort, calendar schedule, and report date separately; access setup, remediation, and fix validation can add time.
Factors influencing the duration of a web app pentest assessment:
Application size: The number of pages, features, API endpoints and user roles directly impacts the time required. More elements mean more ground to cover during the pentest.
Authentication model: SSO, SAML, OAuth, MFA, SCIM, invitation flows, and account recovery increase scope and require careful checks of those identity flows.
API coverage: REST, GraphQL, WebSocket, and mobile-backed APIs add additional assessment paths.
Complexity: Custom functionalities, sophisticated user interfaces, and complex back-end logic increase pentesting effort.
Security maturity: Mature applications may require more advanced security testing to uncover subtle logic flaws and chained attack paths.
Integration with third-party services: Numerous integrations (like payment gateways and external APIs) require additional time to assess the security of these interactions.
Regulatory requirements: If the application must adhere to specific security standards and frameworks, such as PCI DSS, SOC 2, ISO 27001, HIPAA, GDPR, etc., additional time may be required to thoroughly assess it in line with these standards.
Client collaboration: The speed of client responses to queries and the provision of necessary information can also affect the timeline.
Scoping note for AI and LLM-powered web applications
If your web application includes AI agents, LLM-powered workflows, autonomous actions, retrieval-augmented generation, prompt-driven business logic, or integrations that allow a model to call tools or APIs, scope those features explicitly.
A standard web application pentest should still test authentication, authorization, APIs, data exposure, business logic, and OWASP Top 10 risks. However, LLM-specific risks such as prompt injection, indirect prompt injection, data leakage, excessive agency, insecure tool use, and model-driven workflow abuse may require a dedicated AI or LLM pentest.
For 2026, this distinction matters. Many applications are adding AI features faster than security teams can model the new trust boundaries. If an AI workflow can read sensitive data, trigger actions, query internal systems, send requests, summarize customer records, or call external tools, it should be included in the security testing scope.
Pricing and budgeting for a web app pentest
Blaze’s published web application and API pentest packages start at $4,999 USD for Lite, with Essentials at $7,499 and Assurance at $8,999, before applicable taxes. Each covers one bounded web application or API group with stated role limits; larger or more complex environments may need a tailored engagement. See the current package scope and pricing before purchasing. Blaze's penetration testing cost guide explains the main pricing factors teams should consider when budgeting for a web app pentest.
For a small web application, pricing is usually lower because the scope is limited. For a complex SaaS platform with multiple roles, tenant isolation, SSO, APIs, file handling, billing, and administrative functionality, the effort is significantly higher.
When comparing quotes, do not evaluate price alone. Check whether a low-cost proposal includes an actual penetration test or only automated scanning and a generic report. A high-quality assessment should include manual investigation, business logic review, role-based access control testing, API coverage, clear proof of exploitability, practical remediation guidance, and fix validation options.
A better way to evaluate cost is to ask:
How many pentesting person-days are included?
Will the test cover authenticated and unauthenticated functionality? How many user roles are included? Are APIs included?
Will the team test business logic and access control manually?
Is fix validation included, and what are its time window and scope?
Will findings be delivered in a format developers can use?
Will the report support SOC 2, ISO 27001, PCI DSS, HIPAA, or customer security reviews?
Will there be a debrief call with technical stakeholders?
Lite offers fix validation as an add-on. Essentials and Assurance include one round within 90 days. Confirm whether the debrief, additional rounds, or new functionality are included in your engagement.
What to expect from a web application pentest assessment
A web application penetration testing engagement should have clear scope, regular communication, reproducible findings, and an agreed reporting and follow-up process:
Initial consultation and scope definition: Before the pentest begins, expect a brief discussion to define the test scope. This will set the expectations and determine the best approach for the application security evaluation.
Reconnaissance phase: The security engineers will gather information about your application, such as its technology and structure, to help them plan their pentesting strategy.
Automated vulnerability scanning: The team will use specialized tools to scan your web application for known vulnerabilities. This step helps identify potential weak points.
Manual investigation and exploitation: Beyond automated tools, expect manual investigation where experts attempt to exploit identified vulnerabilities. This demonstrates how an attacker might breach your application.
Regular updates and communication: Throughout the process, the penetration testing team will keep you informed, providing updates and explaining their findings clearly.
Comprehensive report: After the test, you will receive a detailed report. The penetration testing report should document scope, methodology, accounts and roles assessed, limitations, affected endpoints, severity, business impact, reproducible steps, and supporting evidence, alongside remediation guidance.
Remediation guidance: The report will also include recommendations for fixing the vulnerabilities. These suggestions will be practical and prioritized based on risk.
Post-pentest debriefing: Often, the penetration testing team will offer a debriefing session to review the findings, answer your questions, and discuss next steps to secure your application.
Fix validation: After you fix the vulnerabilities, you may have the option to retest to ensure the remedial actions were effective.
See Blaze’s sample web application penetration testing report for an example of the structure, findings, evidence, and remediation guidance. This illustrative sample is dated 2022; ask for a current redacted report when evaluating a provider. Findings and remediation status can be managed through Blaze’s PTaaS offering; agree the reporting format and fix-validation arrangements before the engagement.
For online stores and retail platforms, the scope should also reflect the purchase journey. Our e-commerce penetration testing page covers testing considerations for checkout, payments, customer accounts, and connected APIs.
Final remarks
Web application penetration testing is one of the most practical ways to assess your application's resilience to real-world attacks. It helps identify vulnerabilities that scanners miss, validates whether security controls work as intended, and gives engineering teams clear remediation priorities.
For SaaS companies and organizations that rely on web applications, a high-quality web app pentest can support compliance, enterprise sales, customer trust, and risk reduction. The best results come from a structured methodology, realistic test accounts, a clear scope, strong communication, and manual investigation focused on the application's actual business logic.