Mobile application penetration testing helps organizations understand how an attacker could exploit their Android or iOS app, expose sensitive data, or abuse the services behind it.
At Blaze Information Security, we conduct mobile application penetration tests every year. Many of our first-time clients ask about the process – including how to prepare, what information the penetration testers need for an effective test, the tools used, pentesting strategies, typical security issues identified in mobile apps, expected durations, and more.
In response to these common queries, we have created an informative guide designed to help organizations more effectively engage in and prepare for a mobile application penetration testing process.
What is mobile application penetration testing?
Mobile application pentesting assesses a mobile app's security through controlled, simulated attacks. It identifies exploitable weaknesses and gives your team evidence and recommendations to reduce the risk.
This type of cybersecurity assessment examines various components, such as security flaws in the mobile app's backend APIs, authentication and authorization mechanisms, permissions on the filesystem, interprocess communication, and insecure data storage on the cloud and device. Both Android and iOS builds need platform-specific assessment, even when they share a backend. The agreed scope should identify which builds and backend APIs are included.
Android coverage includes manifest permissions, exported activities, content providers, intents, deep links, WebViews, and Android Keystore use. Pentesters examine whether another app can invoke sensitive components or retrieve data without the required permissions.
iOS coverage includes entitlements, Keychain access controls, data protection, URL schemes, universal links, extensions, and runtime behavior. Pentesters check how these controls protect credentials and sensitive operations; the app's sandbox does not establish that its backend authorization is correct.
The primary goals and benefits of mobile app penetration testing include:
Identifying security weaknesses: Discovering vulnerabilities in the mobile application's design and implementation, from simple misconfigurations to complex logical flaws.
Evaluating security controls: Assessing the effectiveness of cybersecurity measures implemented within the mobile app, including its resistance to attacks and protection of sensitive data.
Providing recommendations for improvements: Offering detailed findings and actionable recommendations, enabling organizations to prioritize and address identified vulnerabilities.
Integrating security into the development lifecycle: Playing a vital role in incorporating security practices into the software development lifecycle of mobile applications.
Maintaining customer trust and brand integrity: Demonstrating a commitment to security helps maintain customer trust and protect the brand's reputation.
Supporting compliance and assurance: Provide evidence for reviews against applicable frameworks and regulations, such as GDPR, HIPAA, SOC 2, and ISO 27001, while recognizing that a pentest alone does not establish compliance or certification.
Proactive risk management: Proactively identifying and resolving security weaknesses makes it a cost-effective risk management strategy in mobile app security.
Enhancing security posture: Strengthening the overall security posture through regular pentesting and continual improvements, making mobile apps resilient against cyber threats.
Preparing for a mobile application penetration test
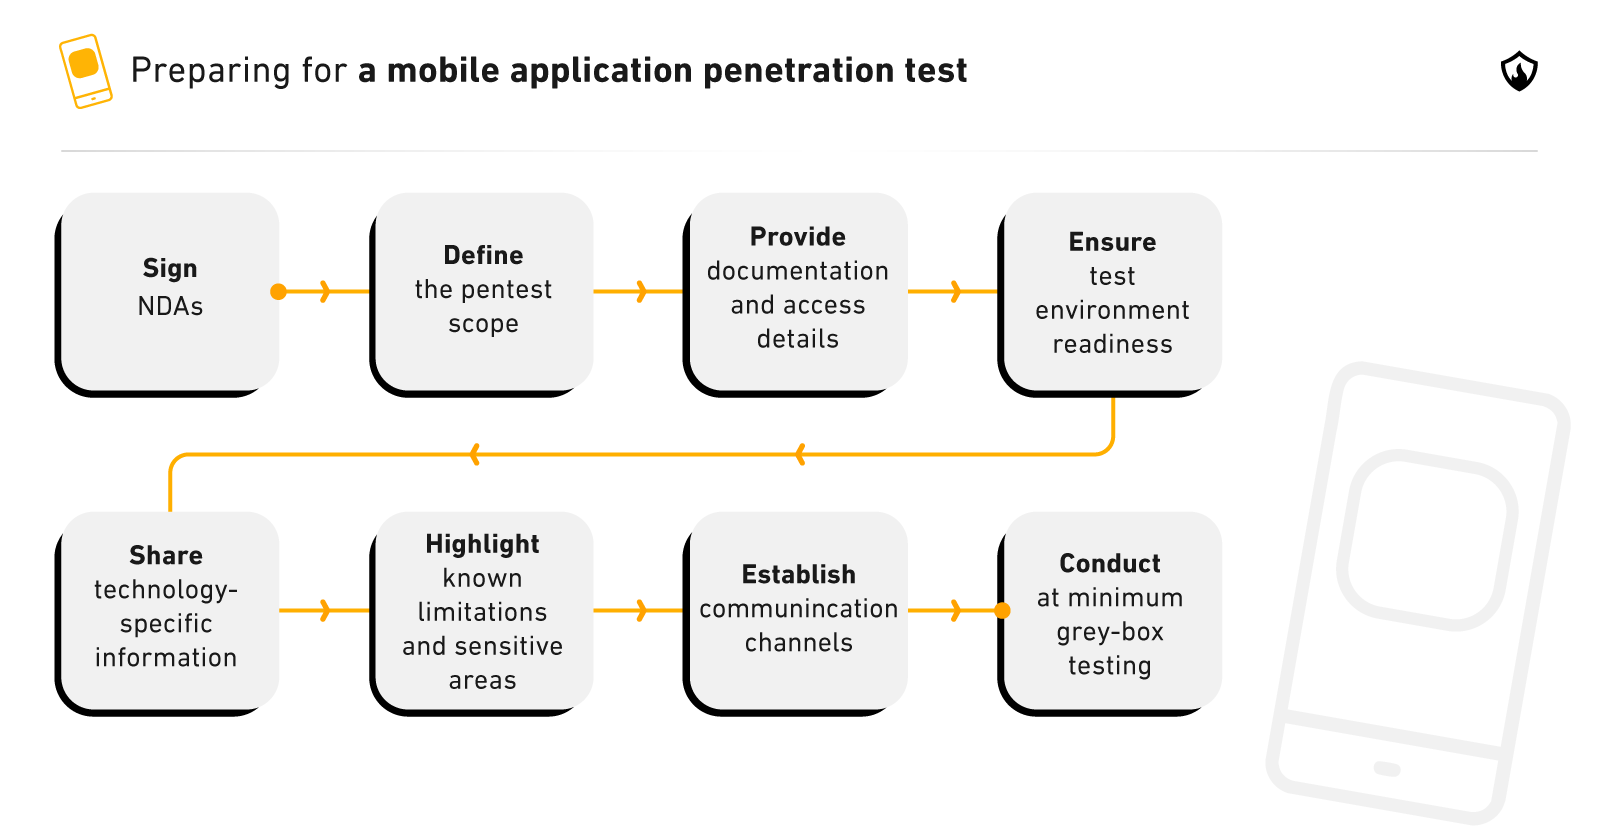
Preparation for mobile app penetration testing is vital to ensure the assessment is thorough, aligned with the application's threat model profile and comprehensively addresses the mobile application's attack surface. Here are essential steps to be ready for the evaluation:
Sign NDAs: Establish a Non-Disclosure Agreement to protect sensitive information shared during the pentest, including details about the mobile app's security mechanisms and internal workings.
Define the pentest scope: Specify which components of the mobile application will be tested, including their functionalities, data flows, and the test's goals and objectives. Clearly state what is not included in the scope, such as specific areas or functionalities.
Provide documentation and access details: If available, give pentesters detailed documentation and access credentials for Android and iOS versions. This includes information on user interfaces, server-side functions, authentication mechanisms, and any specific technologies or unique interaction patterns used in mobile apps. Share at least two accounts per role and, where relevant, accounts in separate tenants. Arrange working MFA or SSO access, test inboxes or phone numbers, and any required device enrollment or allowlisting. Also, sometimes apps aren't yet available as app store apps, so sharing the IPA or APK files or sending them to the pentester via platforms such as TestFlight might be necessary.
Ensure test environment readiness: If the pentest uses a non-production environment, confirm that its data structures, authentication, and functionality resemble production. Populate it with non-sensitive records and realistic account states so pentesters can exercise purchases, subscriptions, and other important workflows.
Share technology-specific information: Provide any special guidance or tools necessary for technologies or frameworks unique to the mobile application.
Highlight known limitations and sensitive areas: Inform pentesters about any sensitive parts of the application or known limitations that require special attention, such as areas handling sensitive data or insecure data storage.
Establish communication channels: Set up clear communication pathways during the pentest. At Blaze, we always set up a Slack channel with the customer throughout the assessment for faster communication and closer collaboration.
Arrange at least gray-box pentesting: In gray-box pentesting, give pentesters partial system knowledge, such as user accounts and admin panels, to enable more realistic attack simulations and uncover vulnerabilities that black-box pentesting might miss in mobile apps. If possible, go white-box with a source-code-assisted pentest.
For a more in-depth assessment, organizations might opt for a full white-box pentest for their mobile apps. In this scenario, the penetration testing team is given access to the mobile application's source code (not simply a decompiled version).
This is particularly effective for mobile app security testing, as it provides insights into Android and iOS apps' unique vulnerabilities and security mechanisms.
Agree on installable builds and supported devices before the engagement. Where appropriate, a release build lets pentesters assess production protections, while a debug variant with selected controls disabled supports deeper instrumentation. Your team should document the differences so behavior observed in the debug variant is not presented as production behavior. OWASP's mobile assessment guidance explains this approach.
Leveraging OWASP methodologies in mobile app penetration testing
The Open Worldwide Application Security Project (OWASP) provides complementary resources for planning and evaluating a mobile security assessment:
The OWASP Mobile Top 10 summarizes common mobile application risks. It is an awareness resource, rather than a complete pentest checklist.
The Mobile Application Security Verification Standard (MASVS) defines mobile application security controls.
The Mobile Application Security Testing Guide (MASTG) provides techniques and checks for evaluating those controls on Android and iOS. Incorporating MAST (mobile application security testing) into the development pipeline allows organizations to improve security posture and reduce costs.
Pentesters use the app's threat model to select relevant controls and OWASP MAS profiles. For example, protecting data from another app on the device involves different attacker assumptions from protecting it against a user who controls the device. The pentesting report should make the assessed builds, device states, resources, versions, coverage, and exclusions clear.
Backend authorization needs its own assessment: device-side checks do not establish whether the server separates users, roles, and tenants. For development teams implementing fixes, OWASP's Mobile Application Security Cheat Sheet is a useful companion reference.
Other frameworks that involve mobile app penetration testing
Some procurement or certification requirements involve additional frameworks, such as NIAP, ioXt Alliance, and App Defense Alliance's MASA. If one applies to your app, agree on the required profile and evaluation route during scoping; an ordinary mobile pentest does not automatically confer certification.
NIAP
NIAP details functional and security assurance requirements for vetting mobile applications, categorizing requirements into Security Functional Requirements, Selection-based Security Functional Requirements, Objective Security Functional Requirements, Optional Security Functional Requirements, and Security Assurance Requirements. It aims to guide the vetting of mobile apps in government and industry, addressing concerns like random bit generation, cryptographic key generation, storage of credentials, access to platform resources, encryption of sensitive application data and more.
ioXt alliance
The ioXt Alliance was created as an industry-wide alliance to set baseline requirements for product security for IoT, and in 2020 and 2021 it expanded its certification program to include mobile apps and VPNs, with a mobile profile for Android security criteria.
MASA
The Mobile Application Security Assessment (MASA) provides an independent assessment route for mobile apps. Its documentation now directs certification applicants to the App Defense Alliance's Mobile App Profile specification. Organizations seeking this validation should confirm the applicable requirements and authorized assessment route, rather than assuming that a general MASVS-based pentest qualifies.
Common vulnerabilities in mobile applications
Like web applications, mobile apps have unique potential vulnerabilities that attackers can exploit. The OWASP Mobile Top 10 2024 provides an essential resource for understanding these threats. The OWASP Top 10 Mobile Risks for 2024, as per the final release, includes the following key areas:
M1: Improper Credential Usage – Mismanagement or misuse of credentials leading to unauthorized access.
M2: Inadequate Supply Chain Security – Security weaknesses in the supply chain that could impact the mobile app.
M3: Insecure Authentication/Authorization – Flaws in authentication or authorization mechanisms that could allow attackers to bypass security measures.
M4: Insufficient Input/Output Validation – Failure to properly validate input and output leads to various attacks, such as injection or data leaks.
M5: Insecure Communication – Lack of secure communication channels, leading to potential interception or alteration of data in transit.
M6: Inadequate Privacy Controls – Insufficient measures to protect user privacy, leading to potential exposure of personal information.
M7: Insufficient Binary Protections – Insufficient resistance to reverse engineering or tampering where those protections are required by the app's threat model.
M8: Security Misconfiguration – Insecure default configurations or misconfigurations that expose the mobile app to attacks.
M9: Insecure Data Storage – Inappropriate storage of sensitive data within the mobile app, leading to potential data breaches.
M10: Insufficient Cryptography – Weak cryptographic practices that fail to secure data effectively.
A slightly more detailed look at common vulnerabilities in mobile apps
Exploring key security vulnerabilities in mobile applications, focusing on the critical areas of data storage, platform usage, APIs, deep links, content providers, and intents:
Insecure Data Storage: Sensitive information may persist in files, logs, caches, or backups. For example, an app may write a session token into a log accessible under the assessed device conditions. Pentesters establish how it can be retrieved, whether it remains usable, and what access it grants. The report distinguishes access by another app from access requiring a rooted or jailbroken device. Fixes can include removing sensitive logging, protecting storage, and correcting token lifetime or revocation.
Insecure Platform Usage: Risks arise from not following best practices for platform features or security measures, possibly compromising user data or app integrity.
Insecure APIs: A signed-in user may change an object identifier in an API request and retrieve another customer's record because the server does not enforce authorization. Pentesters compare requests across users, roles, and tenants to establish the boundary crossed and the data or actions exposed. The fix belongs in server-side authorization; hiding a record or action in the mobile interface does not protect it. Authentication and transport protection also need assessment.
Deep link vulnerabilities: A deep link may pass untrusted input to a sensitive workflow without checking the user's session or authorization. Pentesters establish whether opening the link enables an unauthorized action or exposes data; reaching a screen alone is not enough. Remediation may require validating inputs and destinations, restricting component access, and enforcing authorization when the action executes.
Issues with Content Providers: Insecurely implemented content providers may expose sensitive data to other apps on the device, risking data leakage.
Insecure Intents: Poorly managed intents can lead to information leakage or unauthorized app behavior manipulation, emphasizing the need for proper permission checks and validation.
Comprehensive security testing, static and dynamic analysis, and thorough code review are crucial in identifying and mitigating these risks in Android and iOS mobile apps. On iOS, this includes Keychain access controls and the way biometric checks protect sensitive operations; on Android, exported components, intents, and content providers require platform-specific checks.
What Blaze found in mobile assessments in 2025
The mobile results in Blaze's 2025 Annual Penetration Testing Review show sensitive information exposure as the most frequent finding category. The five leading categories below illustrate what can go wrong in an app:

Sensitive information exposure (CWE-200): Session tokens or personal records become visible to an unintended recipient.
Missing encryption (CWE-311): Sensitive files remain readable if an attacker obtains access to their storage.
Cleartext transmission (CWE-319): An attacker with access to relevant network traffic can read sensitive information sent without encryption.
Insecure storage (CWE-922): Private data persists in locations accessible through another app, backups, or a compromised device, depending on platform controls.
Sensitive information in browser caches (CWE-525): Cached pages or responses retain private information beyond its intended use.
For patterns across other assessment types, see our common penetration testing findings analysis.
Commonly used mobile application penetration testing tools
In mobile application security testing, various specialized tools are employed to ensure a thorough assessment. Here's an updated overview of essential tools in this space:
Emulators and virtual devices
Android Studio's Emulator and Genymotion: These emulators are vital for replicating Android mobile app environments for testing purposes. They allow pentesters to simulate different Android devices and versions.
Corellium: This tool offers a virtualized environment for iOS, providing a platform for testing iOS apps on various Apple devices and OS versions.
Dynamic and static analysis tools
Burp Suite Professional: A cornerstone in application testing for analyzing network traffic, automating attacks, and more. It's commonly used in conjunction with mobile application traffic for in-depth analysis.
Postman and Swagger UI: These remain critical for sending requests to mobile app endpoints, aiding in testing various functionalities within Android and iOS apps.
MobSF (Mobile Security Framework): Useful for performing both static and dynamic analysis on mobile apps, identifying security low-hanging fruit vulnerabilities and insecure data storage practices.
Oversecured: A commercial static analysis tool for identifying potential mobile application vulnerabilities; findings still require investigation and validation.
Reverse engineering, decompilers and binary instrumentation tools
Hopper and Ghidra: Tools for examining compiled mobile apps and libraries to understand their structure and investigate vulnerabilities. Ghidra is open source; Hopper is commercial.
Frida and Objection: Frida is a dynamic instrumentation toolkit for modifying real-time app behavior. Objection, which runs on top of Frida, provides a runtime mobile exploration toolkit that simplifies the use of Frida.
jadx: An open-source decompiler that translates Android applications back to Java code, simplifying reverse engineering for security analysis. The tool effectively processes Android dex files contained within APK files, making it invaluable for analyzing the structure and logic of binary Android apps, and it is also widely used in malware analysis to detect and understand malicious behaviors hidden in mobile applications.
JD-GUI: A standalone graphical utility (GUI tool) that displays Java source codes of ".class" files, enabling easy decompilation and analysis of Java applications.
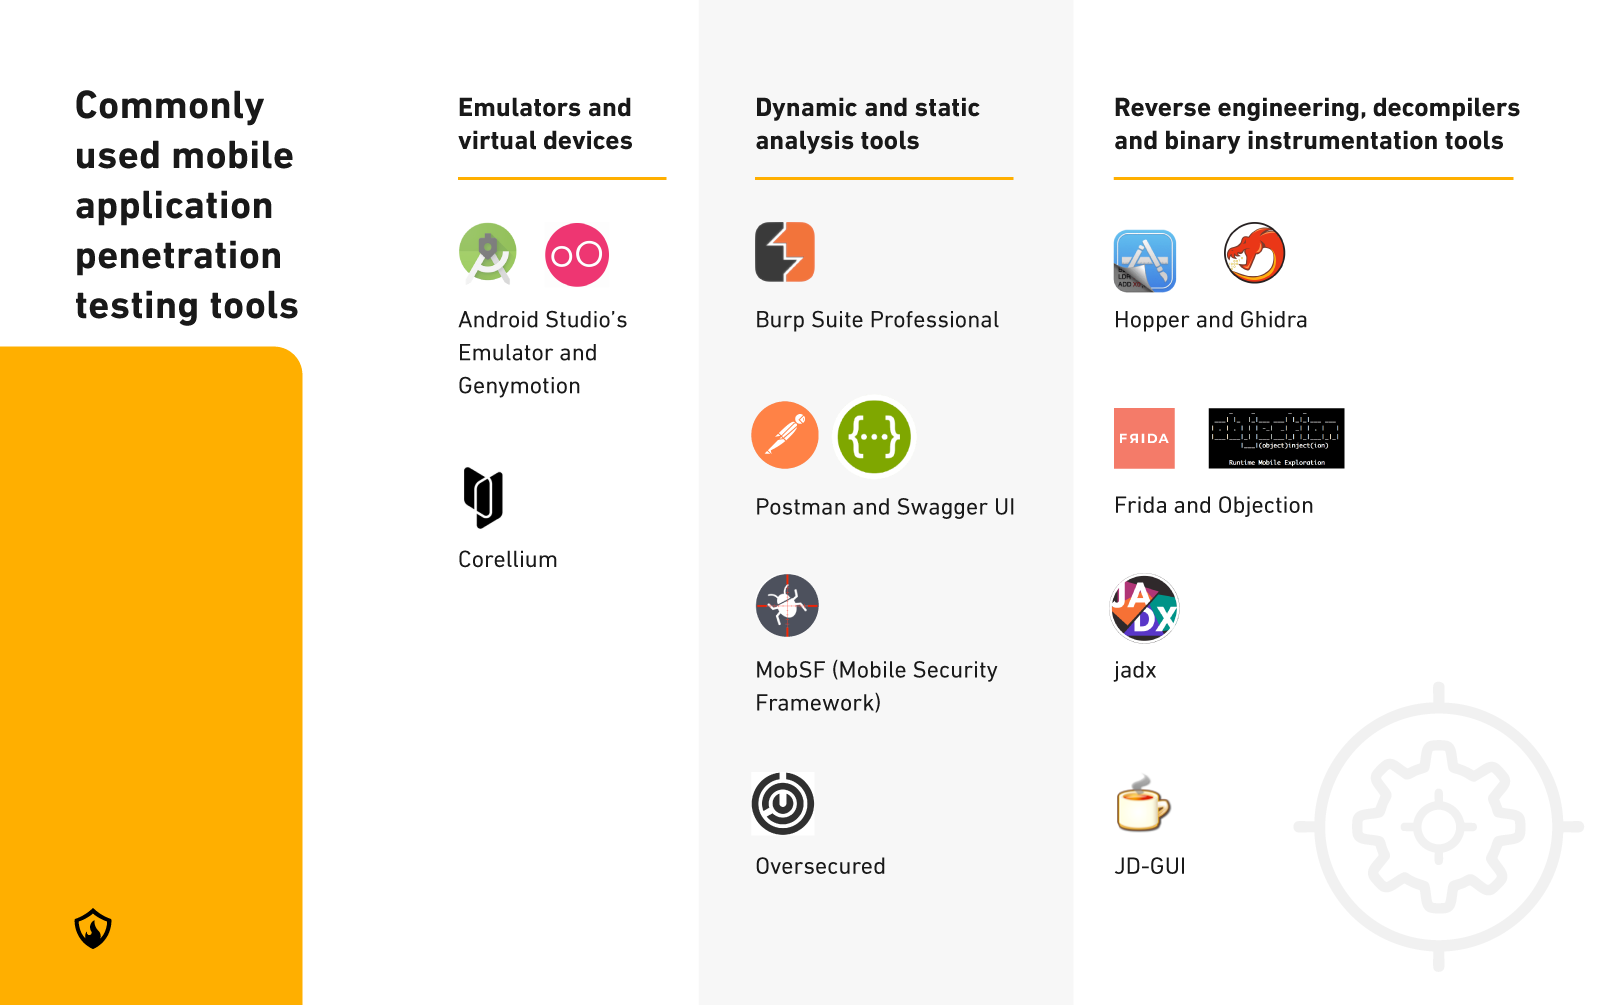
The combination of these tools provides a comprehensive toolkit for mobile security testing. They enable pentesters to perform various tasks, from emulating different environments, attempting controlled bypasses of root/jailbreak detection and TLS certificate pinning, and analyzing network traffic to conducting in-depth static and dynamic analysis and reverse engineering.
The right certifications for mobile app security testing
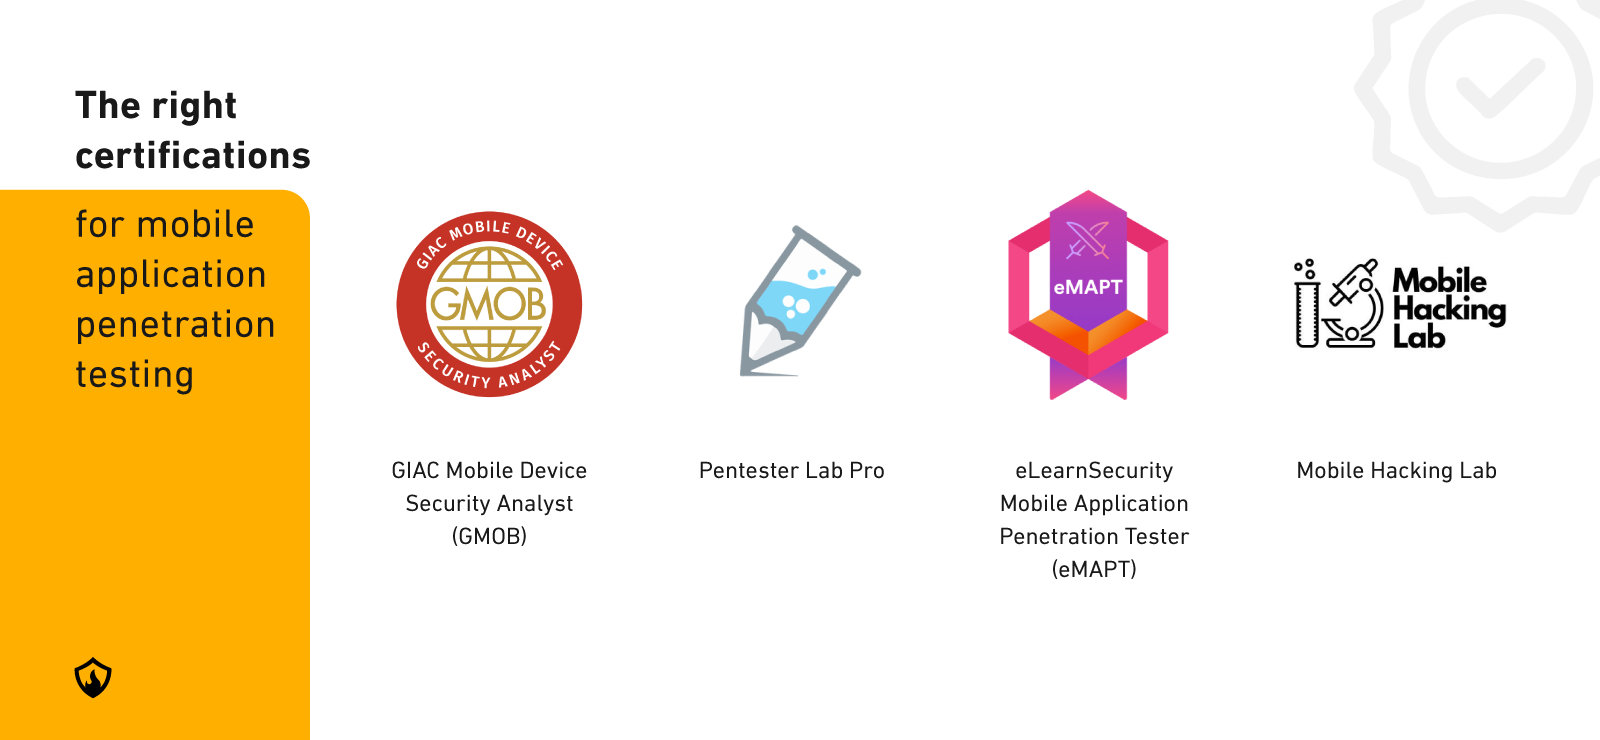
When choosing a provider, ask about the proposed security engineers' Android and iOS experience, relevant training, and ability to explain findings. Certifications can support that assessment, but they do not replace demonstrated mobile expertise. Examples include:
GIAC Mobile Device Security Analyst (GMOB): Similar to the GWAPT for web apps, the GMOB certification focuses on security and penetration testing for mobile devices, including Android and iOS apps. SANS also has a related training known as SEC575 for Android and iOS application security.
eLearnSecurity Mobile Application Penetration Tester (eMAPT): A hands-on certification focused on assessing Android and iOS mobile applications.
Pentester Lab Pro: While not a certification per se, Pentester Lab Pro offers a handful of specialized labs for mobile application pentesting, providing practical experience in a wide range of mobile security scenarios.
NowSecure Academy: NowSecure, a well-known vendor in the mobile application security space, offers free mobile app security courses through its Academy Learning Hub, covering secure development and techniques for pentesting iOS and Android apps.
Mobile Hacking Lab: This training platform focuses mainly on low-level mobile OS hacking (fuzzing of userland apps) but has lessons that can be directly applied to mobile application pen testing.
What's the average duration of a mobile penetration test engagement?
Allow roughly one to two weeks of active pentesting for a focused scope, two to three weeks for a broader app, and longer for specialist work. These are planning ranges; the proposal should specify both platform and backend coverage.
Basic mobile applications (1-2 weeks)
A bounded app with few roles and straightforward workflows may fit this range, with its Android, iOS, and API scope explicitly agreed.
Moderately complex mobile applications (2-3 weeks)
Multiple roles, payment flows, sensitive data, and backend integrations require more time to investigate authorization and business logic.
Complex or large mobile applications (3+ weeks)
Extensive APIs, native-code analysis, biometric controls, NFC payments, or difficult instrumentation can extend the engagement beyond four weeks. MDM restrictions and root or jailbreak protections may add setup effort.
Factors influencing the duration of mobile app pentest
Scope, accessible workflows, API coverage, and source-review depth drive effort. Previous assessments may inform deeper investigation or fix validation; they do not determine duration alone. PCI DSS, HIPAA, or DiGA requirements can add coverage or evidence needs. Allow separately for scheduling, report delivery, remediation, and retesting. Ready accounts, representative data, and prompt technical responses help avoid delays.
How much does mobile app penetration testing cost?
Blaze’s mobile penetration testing packages have the following starting prices, in USD:
Package | Mobile pentest starting price |
|---|---|
Lite | $5,499 |
Essentials | $7,999 |
Assurance | $9,499 |
The final quote reflects the Android and iOS builds, user roles, backend APIs, business workflows, and assessment depth included. Both platforms or a large shared backend may require a broader scope than a starting package. Source-code review, specialist analysis, and follow-up support should be identified in the proposal.
See Blaze’s penetration testing pricing for current package details. The duration ranges above are planning guidance; they do not specify the number of pentester-days included in a package.
What can I expect from a mobile penetration test assessment?
You should expect a defined scope, direct communication with the pentesters, and findings that your developers can reproduce and act on. The engagement has three practical parts:
During the assessment
The process starts with scope and access confirmation, followed by investigation of the app's binary, runtime behavior, storage, network traffic, authentication, business logic, and agreed backend APIs. Blaze's mobile application penetration testing service combines these checks with platform-specific analysis for Android and iOS.
Backend coverage should distinguish the endpoints used by the app from a broader shared API estate, which may require a dedicated API penetration test.
Automated scanning, code inspection, reverse engineering, and runtime instrumentation help penetration testers identify potential weaknesses. AI-assisted analysis can support code investigation and reduce repetitive work, with security engineers checking its output against the code and observed behavior. Pentesters investigate and validate findings through controlled exploitation, and communicate access blockers, coverage limitations, and urgent issues during the engagement.
If your app includes an AI assistant, AI search, or an agent connected to tools, agree whether the scope also includes prompt injection, sensitive-data exposure, and unauthorized tool actions. Blaze's AI and LLM penetration testing covers these additional risks.
At delivery
The report should identify the assessed builds, platforms, accounts, APIs, exclusions, and coverage limitations. Each finding should explain the affected component, attacker prerequisites, reproduction steps, evidence, severity, demonstrated impact, and practical remediation guidance. An executive summary helps your team prioritize the business risks. See what to expect from a penetration testing report for more detail.
Expect a debrief with the pentesters to discuss findings and developer questions. Blaze's PTaaS platform provides access to findings and reports through VulnKeep.
After delivery
Your team uses the recommendations to plan fixes. Where fix validation is included, pentesters replay the agreed findings against an updated build and document the results. Confirm whether fix validation and an attestation letter are included in the agreed package.

Final remarks
Mobile application pentesting gives your team evidence about exploitable weaknesses in a defined scope and practical recommendations to address them. A useful assessment combines platform-specific investigation with the backend and business logic behind the app.
When choosing a penetration testing company, look for relevant mobile expertise, clear coverage, and findings your developers can use.