SOC 2 does not explicitly require penetration testing or prescribe a universal testing frequency. Penetration testing is one way to evaluate security controls under AICPA's Trust Services Criteria. Your own control descriptions, security policies, customer contracts, and risk assessment can make testing necessary for your organization.
For SaaS founders, security teams, and compliance leaders preparing for an audit, the practical questions are what to test, when to test it, and what evidence to retain. A SOC 2 pentest should examine the systems that store, process, or protect customer data within your audit boundary.
This guide covers current requirements, the proposed 2027 criteria, Type I and Type II timing, testing scope, audit evidence, and pricing.
SOC 2 pentest requirements: quick answers
- Is a penetration test mandatory? No universal AICPA mandate applies. Check the testing commitments in your controls, policies, and customer contracts.
- Which criteria does it support? CC4.1 covers control evaluations. Depending on scope, findings can also support CC6.1, CC6.6, CC6.7, CC7.1, and CC7.2.
- How often should you test? Annual testing is a common starting point, with additional testing after material changes. Set the cadence from your risks and commitments.
- When should you test for Type II? Agree the evidence dates with your auditor and leave time within the observation period for testing, remediation, and fix validation.
- What evidence should you retain? Scope, methodology, testing dates, the final report, remediation tickets, retest results, and any documented risk decisions.
- Do the proposed 2027 criteria apply now? No. An exposure draft is a proposal, not an effective requirement.
What is SOC 2 compliance?
SOC 2 is an examination in which an independent CPA firm reports on a service organization's controls against the AICPA Trust Services Criteria. Management must implement controls aligned with its risks, service commitments, and security objectives. A Type II examination also evaluates their operating effectiveness over the review period. It produces an attestation report, rather than a security certification or a guarantee that systems have no vulnerabilities.
For SaaS companies, customers and procurement teams often use the SOC 2 report when evaluating a vendor. The report and a recent penetration test answer different questions: the examination evaluates the described controls, while the pentest investigates whether selected technical weaknesses can be exploited.
Key differences between SOC 2 Type I and Type II
There are two types of AICPA SOC 2 attestation reports: Type I and Type II. The difference between them is the following:
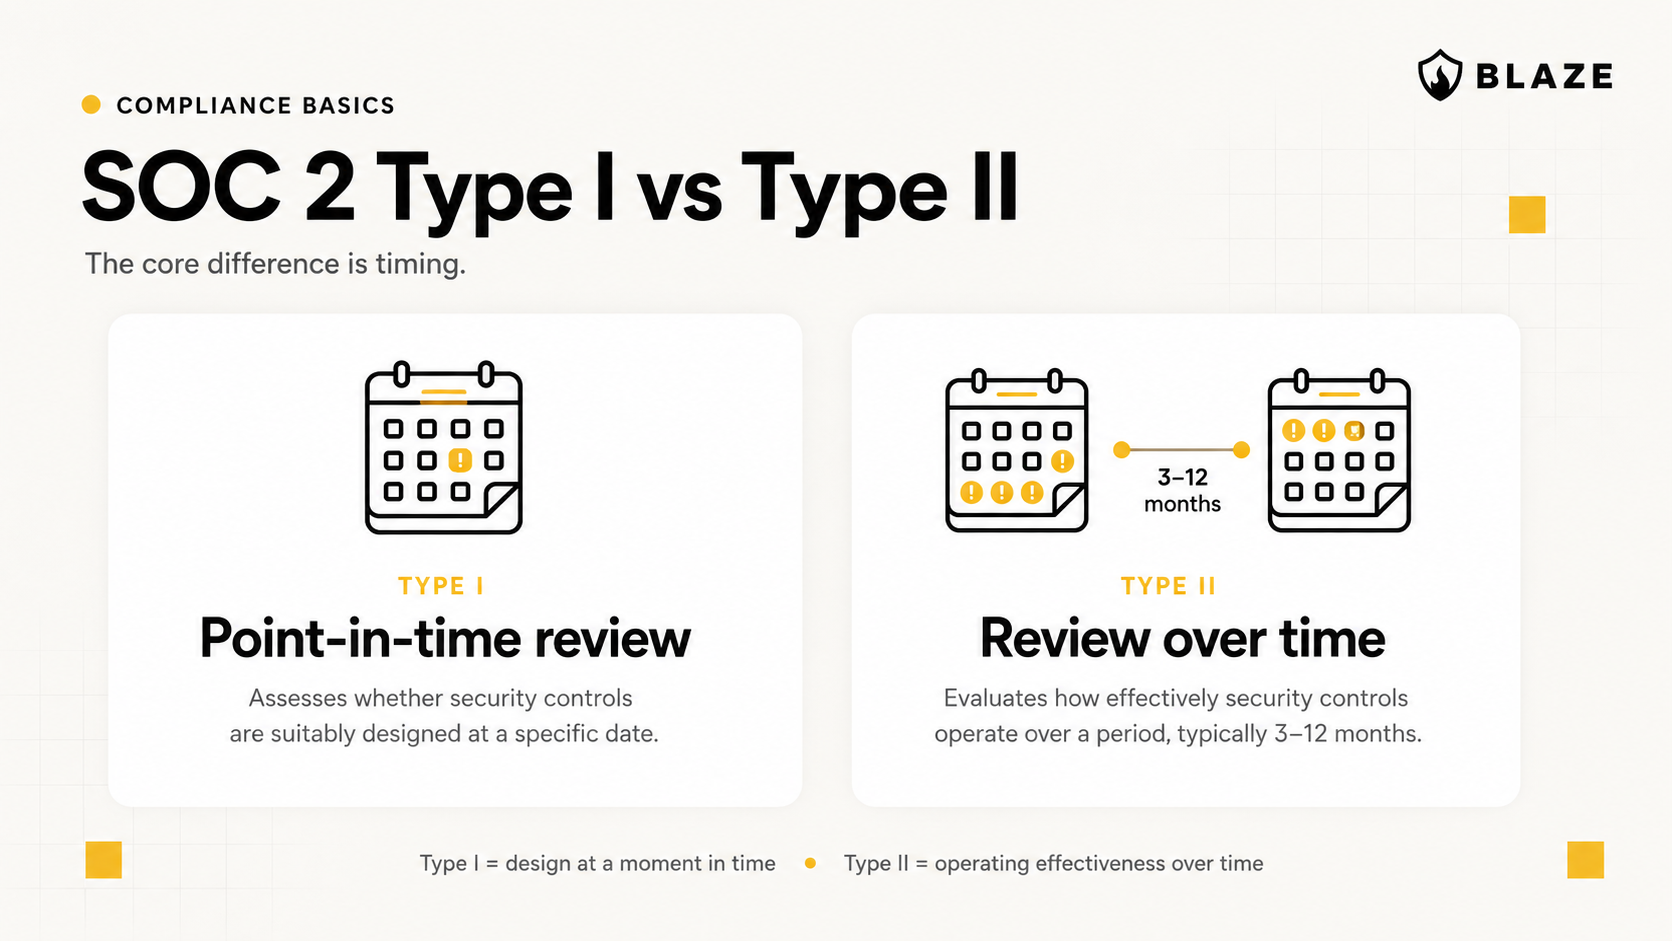
- SOC 2 Type I: reports on an organization's information security controls at a specific time. The idea is to identify the controls and whether they are fit for purpose and in place.
- SOC 2 Type II: reports on an organization's security controls over a period of time (3–12 months). The main goal is to determine whether the controls work as intended and fulfill the requirements of the AICPA's Trust Services Criteria. They are more comprehensive and valuable for customers assessing an organization's long-term commitment and strategy regarding cybersecurity.
For a Type I audit, a pentest may help demonstrate that your company has evaluated its systems in a timely manner. For a Type II audit, timing matters more because the auditor is looking at how controls operated during the audit period.
A practical approach is to perform the penetration test early enough to fix important findings before evidence collection becomes stressful. If the assessment finds a serious authorization flaw, exposed cloud secret, or vulnerable API, you want time to remediate it and validate the fix.
What are the AICPA's SOC 2 Trust Services Criteria?
The AICPA Trust Services Criteria cover five categories. The common criteria apply across those categories; additional criteria apply to availability, processing integrity, confidentiality, and privacy:
- Security
- Availability
- Processing integrity
- Confidentiality
- Privacy
Security ensures protection against unauthorized access and threats. Key measures include access controls, encryption, network security, vulnerability management, and incident response plans.
Availability addresses whether systems and services are operational and accessible to meet the organization's commitments. This involves redundancy, disaster recovery planning, capacity management, and meeting service level agreements (SLAs).
Processing Integrity ensures data is processed accurately, completely, and on time. This includes data validation, error handling, system monitoring, and controlled process changes.
Confidentiality protects sensitive information from unauthorized access. Key practices involve data classification, encryption, strict access controls, and secure data retention and disposal.
Privacy governs the responsible handling of personal information and aligns with applicable laws and privacy notices. It covers notice and consent, data minimization, respecting individual rights, third-party disclosures, and privacy impact assessments.
Penetration testing usually supports the Security category most directly, but a well-scoped SOC 2 pentest can also provide useful evidence for confidentiality, availability, and privacy-related controls depending on the systems tested.
SOC 2 penetration testing and vulnerability scanning: what are they?
Penetration testing and vulnerability scanning are two critical elements used to assess the security of a computer system, verify an organization's overall security posture, and test the controls designed to protect against cyberattacks.
Also known by the short form "pentest", penetration testing involves a simulated attack using the same tools, tactics, techniques, and procedures as an adversary for purposes of ethical security testing. The intention is to identify vulnerabilities and exploit weaknesses to compromise and demonstrate impact on a particular system, a network, or an entire organization.
Impact demonstration can take different forms, such as gaining access to confidential assets, such as customer data or strategic, board-level sensitive information.
Conversely, vulnerability scanning is an automated process that attempts to identify known vulnerabilities and can indicate a company's security posture.
Penetration testing and vulnerability scanning can help identify security risks, but they have different strengths and weaknesses. A penetration test is more likely to find unknown vulnerabilities, but it is more time-consuming and expensive. Vulnerability scanning is less likely to find vulnerabilities that do not follow known patterns, but it is much quicker and cheaper.
Does SOC 2 explicitly require penetration testing?
No. The current Trust Services Criteria do not prescribe a penetration test as a mandatory control. CC4.1 addresses ongoing and separate evaluations of internal control. An organization selects ongoing evaluations, separate evaluations, or both, as appropriate. Control testing, internal audit assessments, compliance assessments, vulnerability scans, and penetration testing can contribute to those evaluations. Its points of focus describe possible evaluation methods, including penetration testing. A point of focus illustrates how to address a criterion; it is not a universal checklist of required activities.
The relevant reference is the 2017 Trust Services Criteria with revised points of focus from 2022. Penetration testing can provide useful evidence, but a report alone does not demonstrate that every applicable criterion has been met.
When can a SOC 2 pentest become a requirement for your company?
- Your controls or policies commit to it: If your described control calls for an annual independent penetration test, the auditor will evaluate whether that control operated as described.
- A customer contract requires it: A contractual testing obligation applies even though SOC 2 does not universally mandate the activity.
- Your risk assessment calls for it: Internet-facing applications, sensitive customer data, and complex access controls may warrant testing as part of your response to identified risks.
Discuss the planned scope, frequency, and evidence with your CPA firm before booking. The auditor determines whether the evidence is sufficient for the examination.
Will AICPA's proposed 2027 SOC 2 criteria change penetration testing?
The proposed 2027 criteria are not current requirements. AICPA announced the exposure draft on October 28, 2026, with comments due January 15, 2027. If approved as proposed, it would take effect for engagements beginning on or after December 31, 2027, with early adoption permitted.
The proposal restructures parts of the criteria and expands points of focus concerning AI governance, model monitoring, prompt manipulation, data poisoning, and automated decisions. AICPA's announcement does not establish a new universal penetration-testing mandate.
Plan current audit evidence against the applicable existing criteria. If your service uses AI, discuss the relevant risks and testing scope with your auditor; do not treat a proposed future change as an obligation already in force.
Does SOC 2 require vulnerability scanning?
SOC 2 does not universally prescribe vulnerability scanning, but CC7.1 requires detection and monitoring procedures for newly discovered vulnerabilities and changes to system configurations. Its points of focus identify periodic vulnerability scans and scans after significant changes as a way to support that objective. Your own vulnerability management controls may specify scanning and remediation deadlines.
Recurring scans help identify potential vulnerabilities, including known software flaws, exposed services, and misconfigurations in network infrastructure. Manual penetration testing investigates exploitability, access controls, business logic flaws, and attack paths that automated scanning may miss. Use the two activities together where your risks warrant them; a scan does not replace a penetration test that your policies or contracts promise. Our guide to SOC 2 vulnerability scanning explains the distinction.
How pentests support SOC 2 audit evidence
A SOC 2 pentest does not replace policies, risk assessments, access reviews, monitoring, incident response, or vulnerability management. It supports them by showing that selected controls were tested in practice.
This is where the audit conversation becomes more concrete. Instead of only saying, "we have access controls," a pentest can show whether those access controls prevent a normal user from reaching another customer's data. Instead of only saying, "we monitor for threats," a pentest can help validate whether suspicious activity is logged, alerted on, and investigated.
| SOC 2 criterion | What it evaluates | How a pentest helps | Evidence to keep |
|---|---|---|---|
| CC4.1 | Monitoring activities and separate evaluations | Shows that the organization performs independent security evaluations | Pentest report, scope, methodology, testing dates |
| CC6.1 | Logical access controls | Tests whether authentication and authorization controls prevent unauthorized access | Access control findings, proof-of-concept evidence, and remediation tickets |
| CC6.6 | Protection against unauthorized access | Tests whether systems can be exploited through realistic attack paths | Exploitation evidence, affected assets, severity ratings |
| CC6.7 | Data transmission and protection controls | Tests whether sensitive data can be exposed, intercepted, or accessed insecurely | API findings, TLS findings, encryption-related evidence |
| CC7.1 | Vulnerability identification and monitoring | Identifies vulnerabilities, misconfigurations, and exploitable weaknesses | Findings, affected assets, risk ratings and remediation evidence |
| CC7.2 | Monitoring system components | Can validate whether suspicious testing activity is logged or detected | Logs, alerts, detection tickets and incident response evidence |
This mapping matters because auditors rarely care about a pentest as a standalone document. They care whether the test supports the controls in scope, whether the tested systems match the SOC 2 system boundary, and whether your company acted on the results.
When should you schedule a SOC 2 Type II pentest?
Agree testing dates around the control's required frequency and your Type II observation period. Schedule early enough to investigate findings, implement fixes, and validate remediation before the evidence deadline. A test completed before the period may provide context, but does not by itself establish that a periodic testing control operated during the period being examined.
For example, if your observation period ends in December, booking testing in the final week leaves little room for engineering fixes and retesting. Confirm the testing, report, remediation, and validation milestones with your team and auditor. Annual testing is a common baseline; significant application, API, cloud, authentication, or authorization changes may justify an additional assessment.
Can you complete a SOC 2 audit with open pentest findings?
A vulnerability does not automatically determine the audit opinion. The auditor considers the nature of the issue, the affected controls, and whether those controls operated as described. Maintain a finding owner, severity, remediation deadline, mitigation evidence, and retest status. Document any risk acceptance with its rationale and approval; it does not automatically resolve a missed control commitment or contractual deadline.
What should a SOC 2 penetration test cover?
The most important thing is scope. Your pentest should align with the systems included in your SOC 2 report.
If the SOC 2 system description covers your main SaaS product, APIs, administrative panels, cloud infrastructure, identity provider, Kubernetes clusters, mobile applications, or internal systems that support customer data, those assets should be considered when defining the penetration test scope.
This does not always mean testing everything at once. It does mean you should avoid testing a low-risk public website while leaving the systems that store, process, or protect customer data untouched.
It is also worth speaking with your auditor before finalizing the scope. The auditor should not design the pentest, but they can confirm whether the planned scope is likely to support the audit evidence they expect.
Defining the scope of the SOC 2 pentest
Defining the scope of a SOC 2 penetration test involves establishing the boundaries of what will be tested during the engagement. Typically, this includes a list of assets that the penetration testing team is authorized to evaluate and excludes those that are off-limits.
From our experience, organizations working toward SOC 2 compliance usually consider the following elements when determining the scope of their penetration test assessments:
- the company's main product, particularly any user-facing SaaS or web platforms;
- administrative panels or internal tools that support the user-facing SaaS;
- APIs, such as REST, GraphQL, and microservices;
- public-facing server infrastructure, typically hosted in the cloud;
- security assessments of mobile applications, if applicable; and
- the company's internal network, critical servers and infrastructure, which may include Active Directory, Kubernetes clusters, and similar systems.
Penetration tests are often conducted in a staging environment to prevent potential disruptions in production. As long as the staging environment closely mirrors the production setup, this approach is generally acceptable and widely used. However, consulting with your SOC 2 auditor beforehand is advisable to ensure that the scope meets their expectations.
A common mistake is scoping the pentest too narrowly. If your SOC 2 scope includes your SaaS platform, APIs, and cloud infrastructure, a pentest of only your marketing website will not provide the auditor with much useful evidence.
To evaluate data security, map how in-scope applications process customer data and which security measures protect each transition. Comprehensive penetration testing should trace an authorized workflow through the organization's systems, then test nearby misuse cases: a low-privilege account retrieving another customer's exports, a support role invoking administrator functions, or a service credential reading unrelated storage. These tests can reveal hidden vulnerabilities in cross-service permissions that a scanner's list of software flaws does not capture.
SOC 2 pen testing: access controls and testing approaches
SOC 2 does not prescribe a universal testing methodology or access model. Black-box testing simulates an external attack without prior system knowledge or credentials. Gray-box testing simulates an attack with partial system knowledge, such as selected documentation and user accounts. White-box testing gives testers full access to the agreed technical information, such as architecture, configuration, and source code.
For a SaaS application, authenticated testing with representative roles and at least two test tenants helps evaluate whether one customer can access another customer's data or an ordinary user can invoke administrator functions. Include API authorization, SSO, exports, and background jobs where relevant. A public perimeter test alone will not answer those questions. Regular penetration testing, also called pen testing, complements continuous monitoring by investigating whether security controls work against realistic misuse. For example, a data deletion workflow should enforce the same tenant and role restrictions as the corresponding read operation. Blaze researchers perform manual testing and validate findings, using AI assistance where it helps.
How long does a SOC 2 pentest take?
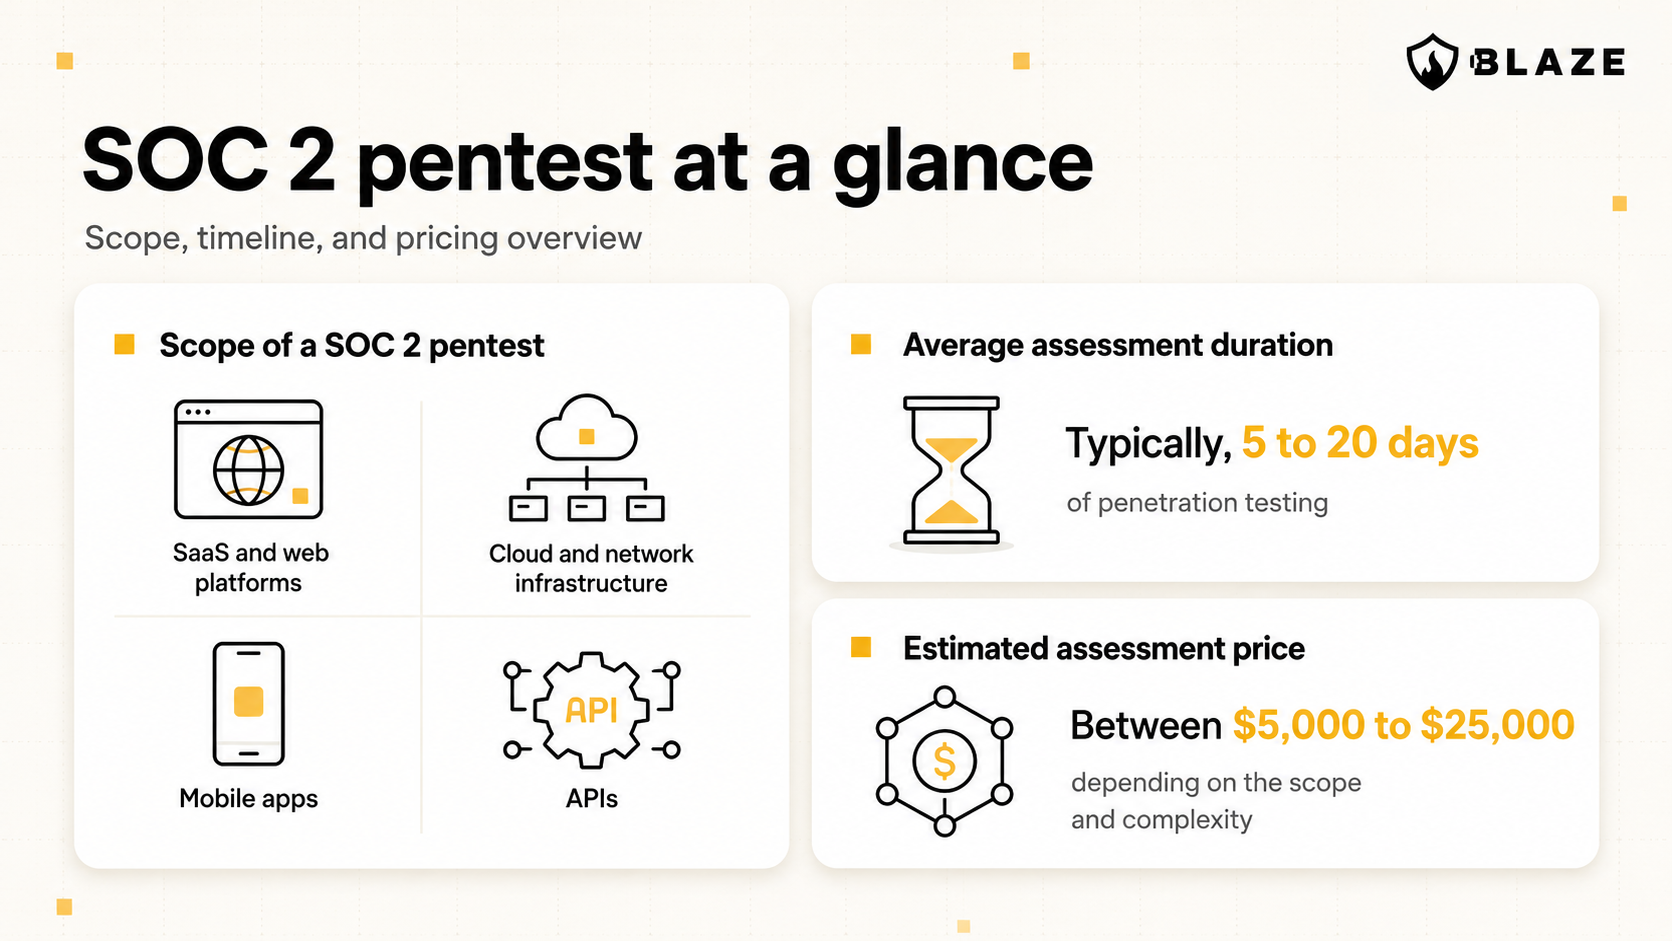
Blaze's planning range for a SOC 2 pentest is typically 5–25 person-days, depending on scope and complexity. A focused application may take about one to two weeks of testing, while multiple applications, cloud accounts, or internal networks can require more effort. Person-days measure work, not calendar lead time.
Agree scope, access readiness, testing duration, and report delivery before booking. Leave separate time for your engineers to remediate findings and for fix validation. Judge a proposal by its coverage and technical depth rather than duration alone.
How much does a SOC 2 penetration test cost?
Blaze's web application and API penetration testing packages start at $4,999 USD. Essentials costs $7,499 and Assurance costs $8,999. These are Blaze's published service prices for one bounded web application or API group, not the cost of the SOC 2 audit. Applicable taxes are additional.
| Package | Package price (USD) | Published scope and fix validation |
|---|---|---|
| Lite | $4,999 | One web application or API group with up to two roles. Fix validation is an add-on. |
| Essentials | $7,499 | One web application or API group with up to three roles, business logic testing, and one validation round within 90 days. |
| Assurance | $8,999 | One web application or API group with up to five roles, advanced and business logic testing, and one validation round within 90 days. |
Different scopes command different prices. A focused application or API group may fit a published package after scope confirmation. Multiple applications, separate administrative portals, additional API groups, cloud configuration reviews, internal networks, mobile applications, or a more complex role and tenant model may require a tailored engagement.
The broader $5,000–$25,000 planning range discussed in our pentest pricing guide is an estimate, not a fixed price or ceiling. Comprehensive environments can cost more. The SOC 2 label alone does not determine the effort: compare the assets, roles, workflows, testing depth, reporting, and fix validation included in each quote.
Lite offers fix validation as an add-on. Essentials and Assurance include one validation round within 90 days. That window does not extend your remediation policy, contractual deadlines, or audit period, and validation of a reported fix does not automatically cover newly added features.
What audit evidence do SOC 2 auditors expect?
Keep an evidence trail that connects testing to the controls and systems in scope:
- Scope and access: Asset inventory, environment, roles, methodology, test dates, exclusions, and limitations.
- Technical results: Final report with severity, business impact, reproducible findings, and remediation guidance.
- Follow-up: Remediation tickets, responsible owners, deadlines, change records, and retest results.
- Risk decisions: Approved exceptions or risk acceptance, with rationale, compensating measures, and review dates where applicable.
An attestation letter or executive summary can help with customer security reviews, but it does not replace detailed evidence when the auditor needs to inspect it. A clear executive summary explains the business impact and remaining security gaps; the technical report shows the evidence behind those conclusions. Track how your team will address vulnerabilities and remediate identified deficiencies under its agreed deadlines. The CPA firm remains responsible for the SOC 2 opinion.
If you want to learn more about the topic, see the complete buyer's guide to SOC 2 penetration testing. It contains everything you need to know about pentesting for SOC 2 compliance.
Need a quote for both a pentest and a SOC 2 audit?
Blaze partners with Render Compliance, a CPA firm, for SOC 2 audits. If you need both services, you can receive a single quote covering Blaze’s penetration test and Render Compliance’s independent SOC 2 audit. Talk to an expert about your testing scope and audit timeline.