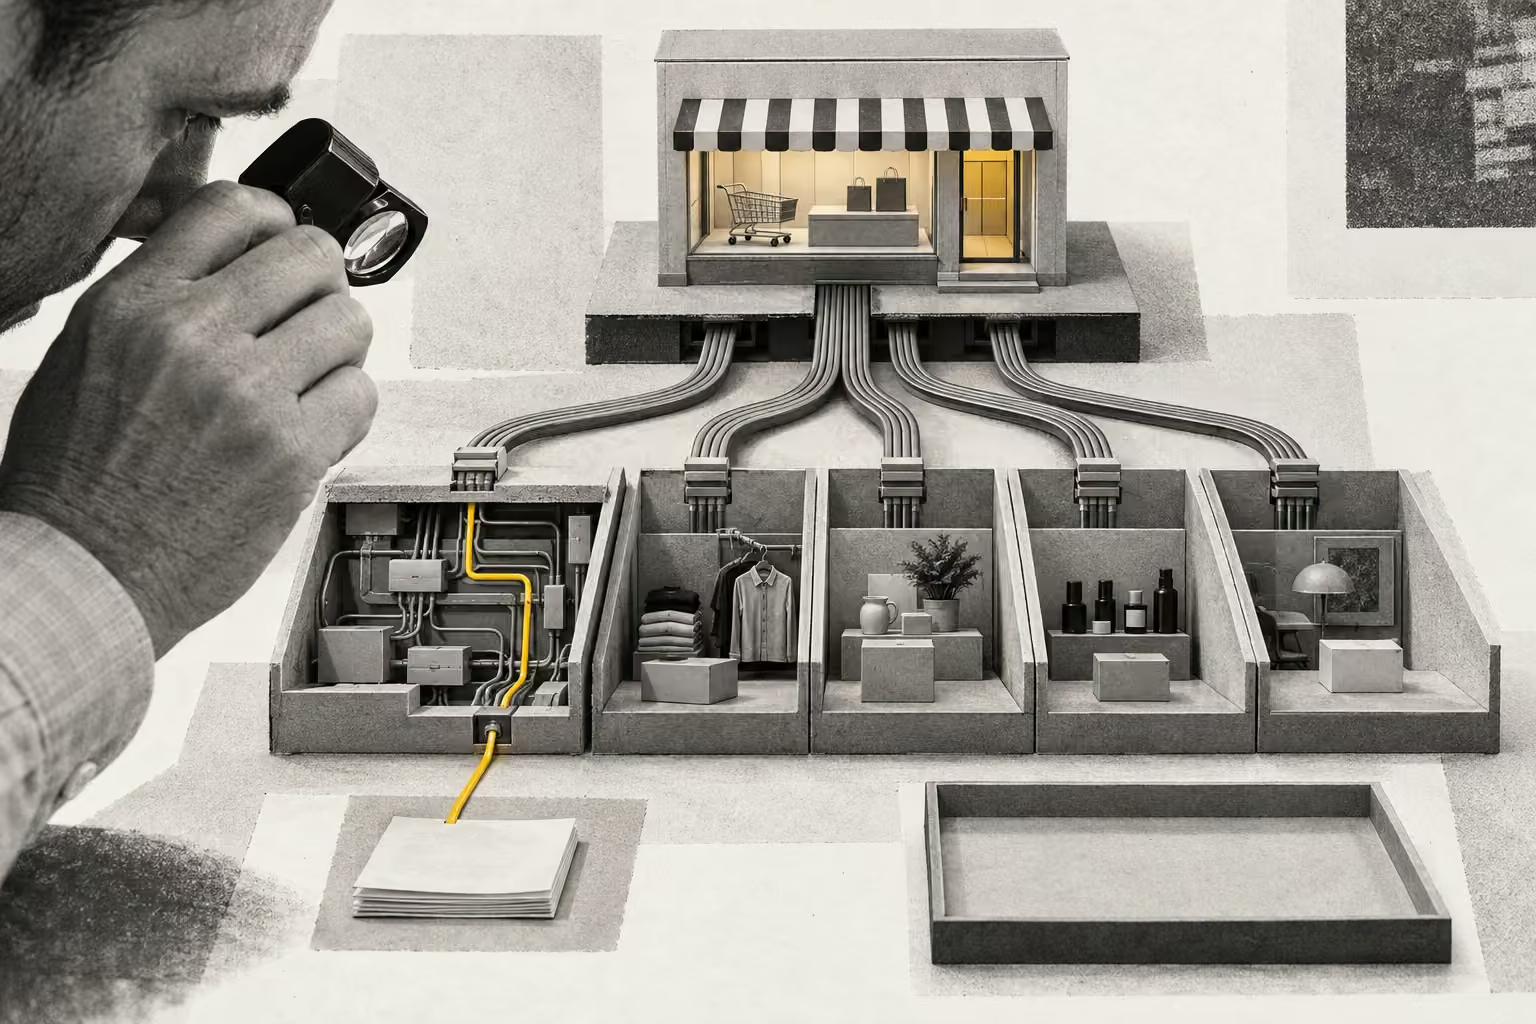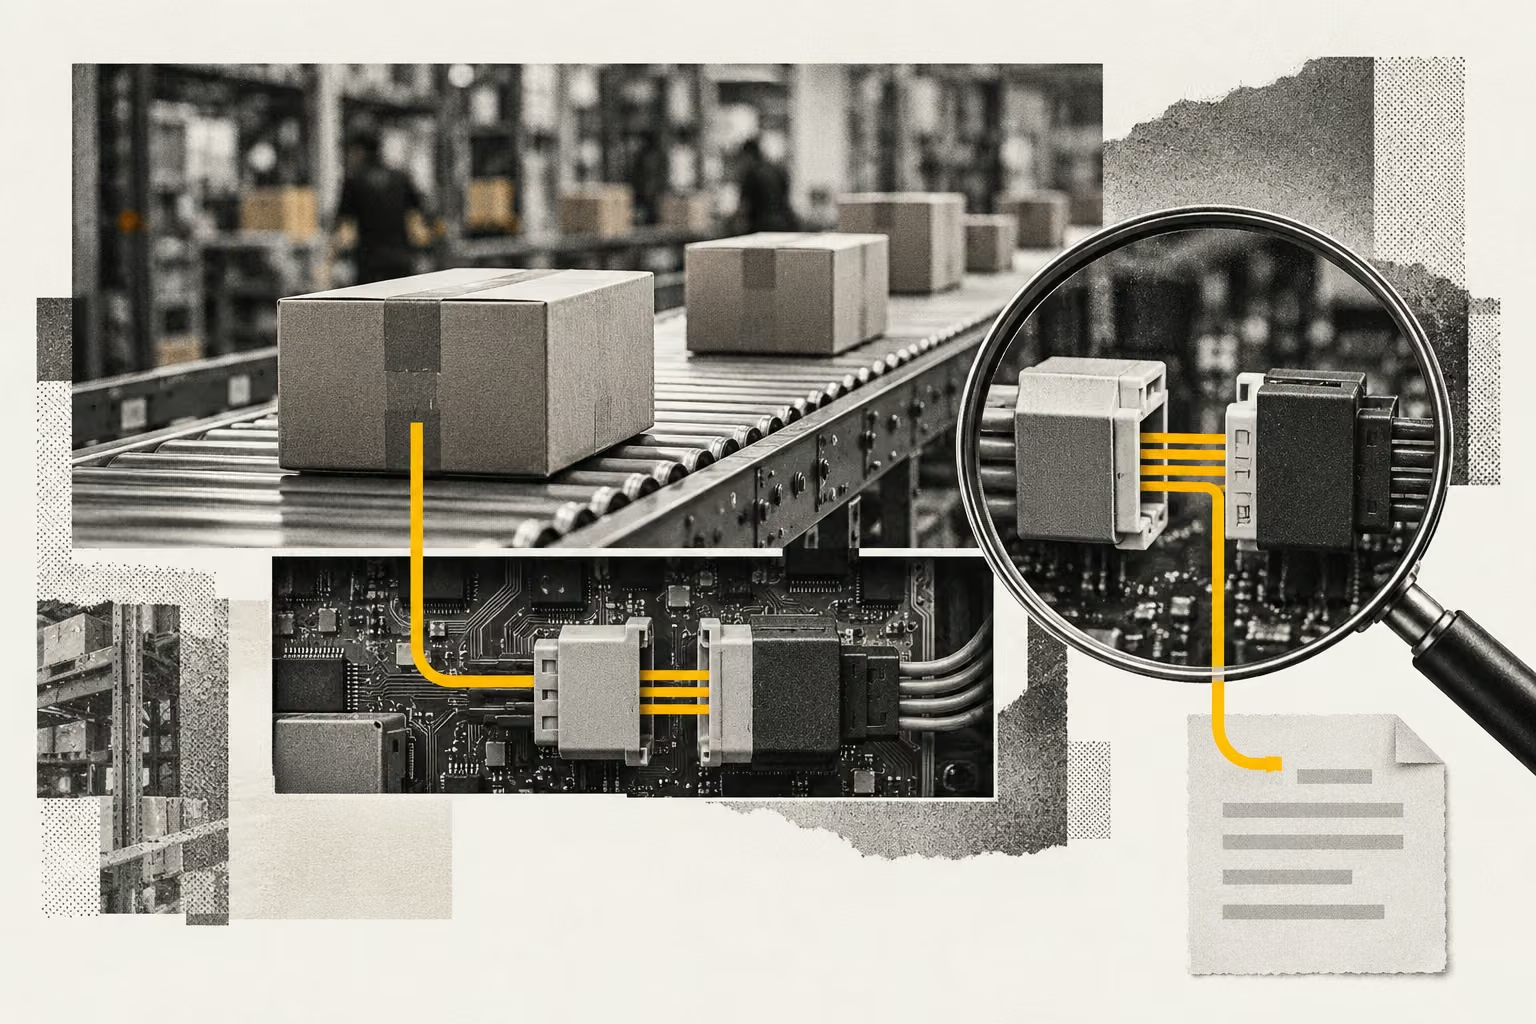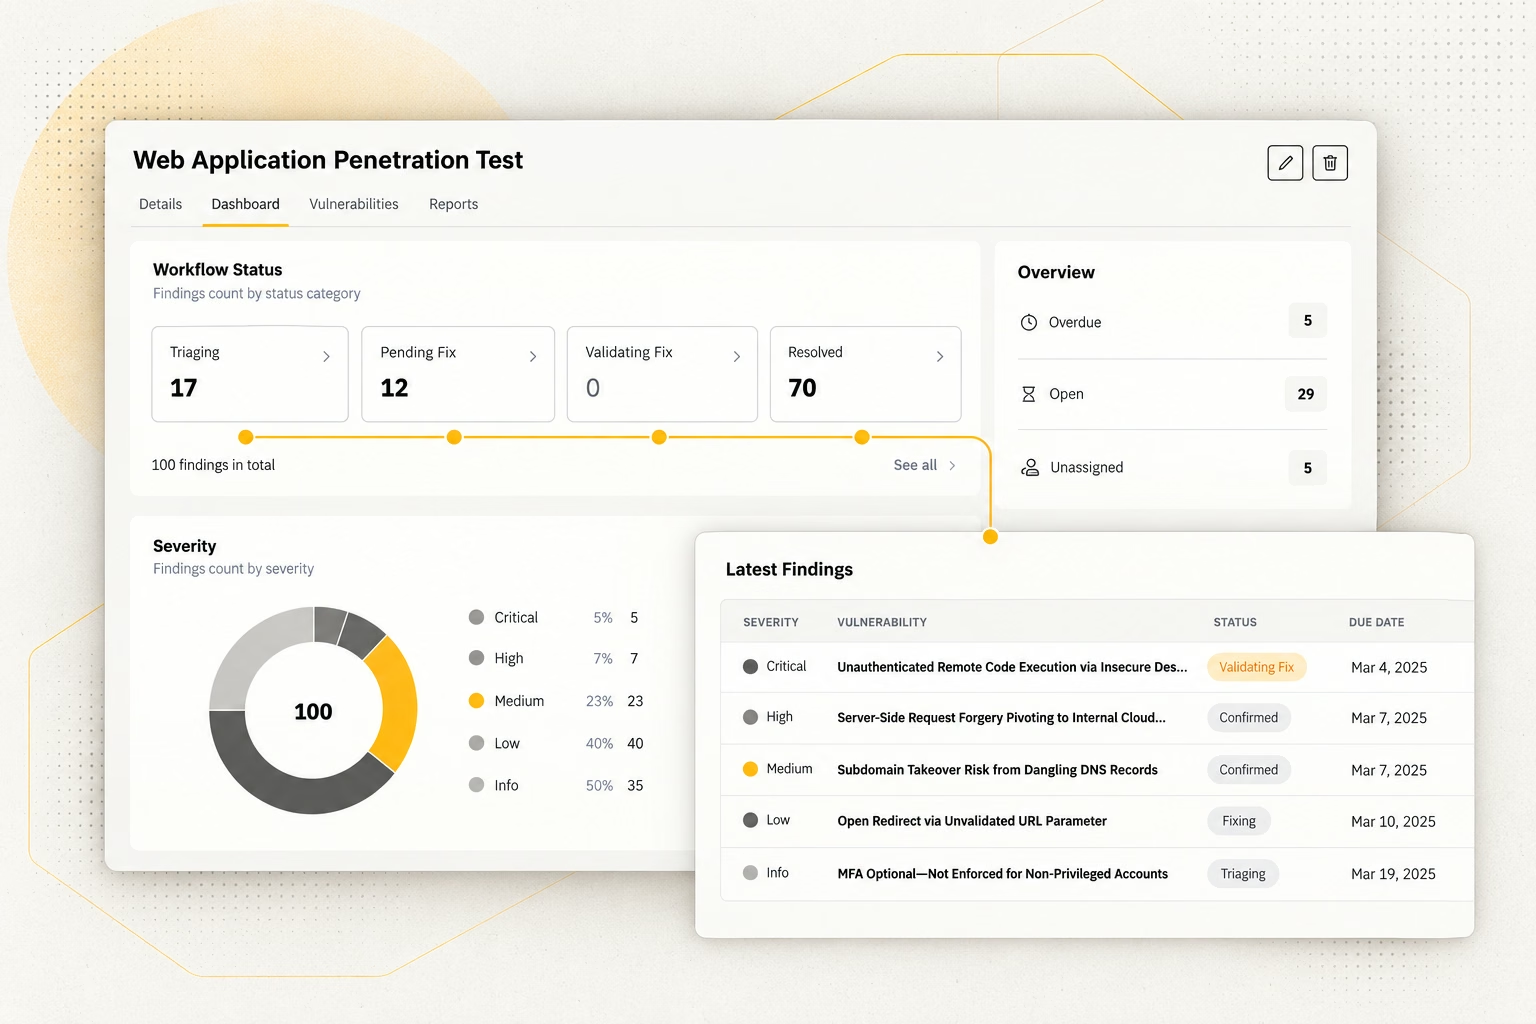
Penetration testing as a service (PTaaS) combines authorized security testing with a cloud-based platform for managing scope, findings, remediation and retesting. Security researchers simulate attacks to identify and validate vulnerabilities; the platform helps security and development teams coordinate that work across assessments. For a detailed example of assessment coverage, see our guide to web application pentest scope.
For CISOs, AppSec leads and engineering teams, its value is practical: findings can reach developers during testing, questions stay connected to the evidence, and repeated assessments share a consistent workflow. This guide explains how PTaaS works, its benefits, what it can test, and how to compare pricing, coverage and providers.
What is penetration testing as a service (PTaaS)?
PTaaS, also called pentest as a service, is a delivery model that connects penetration testers and their customers through a persistent platform. Teams use it to request assessments, review validated findings, collaborate on remediation and retain reports. Testing capacity may be purchased per assessment or through an annual allowance.
The platform supports the work; testing expertise determines how security flaws are investigated. A web application assessment might examine authentication, business logic and tenant isolation. Network testing might investigate exposed services and privilege escalation. Cloud-based delivery can support both.
How does PTaaS work?
A typical engagement follows five stages. Consider an illustrative SaaS release that introduces an administrator role and an invoice API. The same example shows how testing becomes an engineering task and a verified outcome.
- Scope the assessment. The team identifies the affected endpoints, two test tenants, representative user roles and sensitive workflows. The scope records environments, exclusions, permitted techniques and third-party authorization.
- Prepare access and schedule testing. Developers supply working accounts, API documentation and example requests. The provider confirms readiness, the testing window, safety limits and urgent-finding contacts.
- Investigate and validate vulnerabilities. Penetration testers examine access controls and attempt permitted attacks. In our example, a researcher demonstrates that a user from one tenant can retrieve another tenant's invoice. The finding records the prerequisites, requests, response evidence, affected endpoint and impact.
- Remediate with the evidence attached. An engineer owns the issue, asks questions in the finding record and implements a server-side authorization check. A linked engineering ticket can track the change where an appropriate integration is available.
- Retest the specified fix. The researcher repeats the original cross-tenant request and relevant checks within the retest scope, then records the build, date and result. The team uses remaining coverage gaps and upcoming changes to plan further testing.
This example uses fictional demonstration data, not client results or a recommended testing duration. Our penetration testing methodology guide explains the wider assessment lifecycle. NIST SP 800-115 and the OWASP Web Security Testing Guide provide established assessment guidance.
How the dashboard supports the workflow
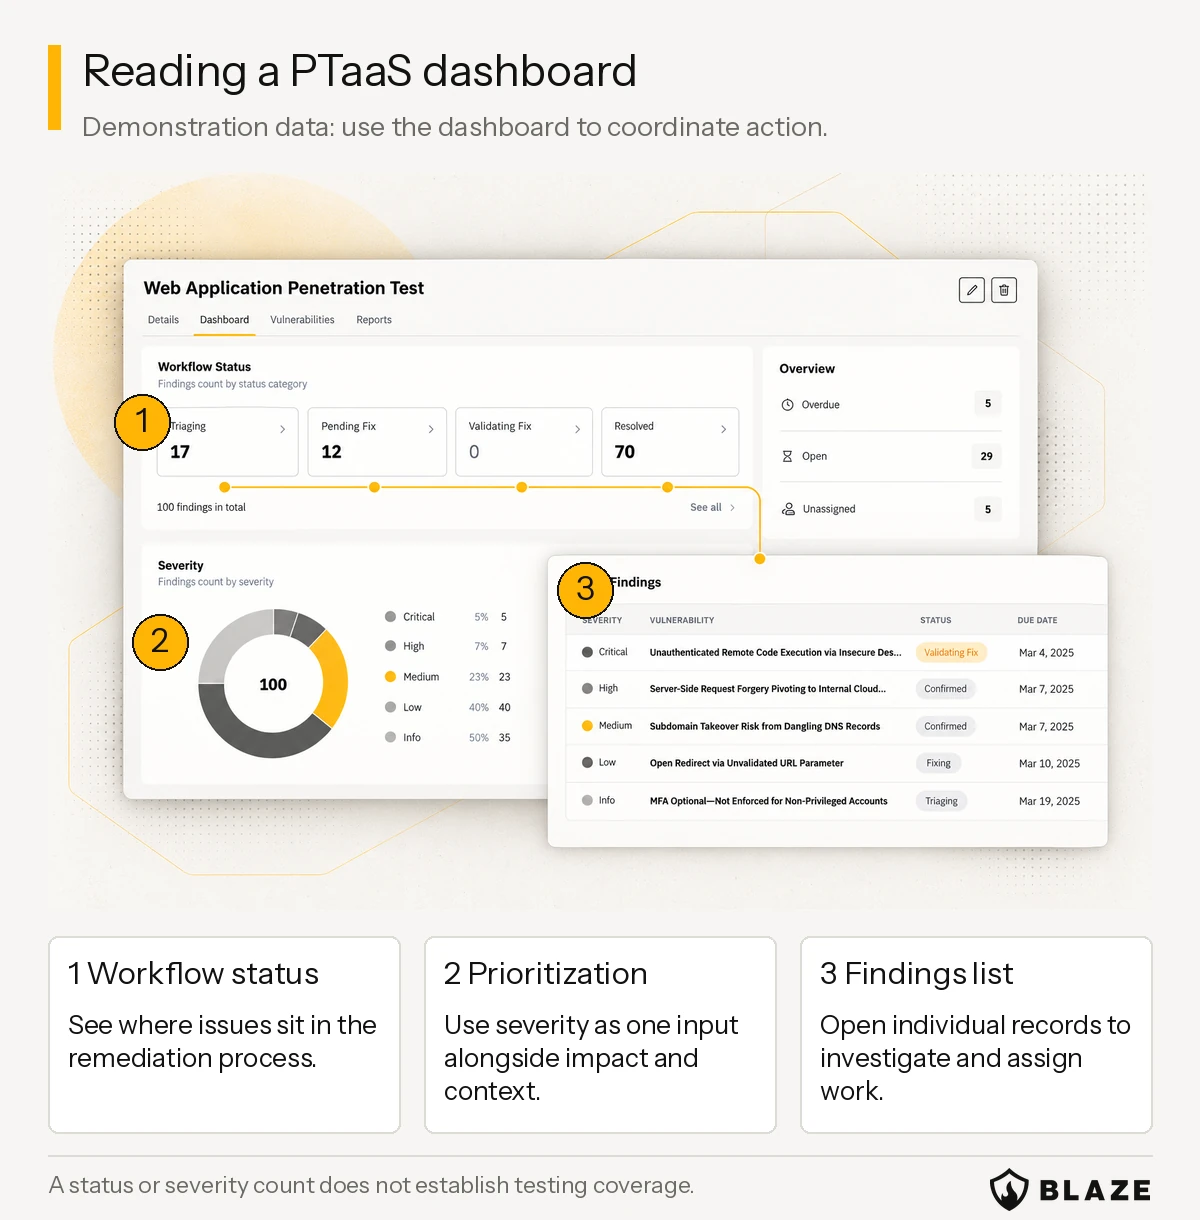
A PTaaS dashboard brings findings, severity and remediation status together. Open an individual record to understand the exploit evidence, assign an owner and discuss the fix. Severity helps prioritize investigation; business impact, exposure and affected assets provide the context for action.
Human expertise, automated tools and AI
PTaaS providers combine testing methods differently. Researchers use automated tools for repeatable discovery and checks, while human expertise supports business-logic testing, exploit chaining and interpretation of impact. AI-assisted analysis can support selected discovery and investigation tasks. Autonomous execution requires explicit permitted actions, stop conditions and oversight.
For the invoice example, discovering an endpoint is only the beginning: the assessment must establish which user should access which invoice and reproduce the unauthorized access. Our automated penetration testing and AI guide explains the distinction between generated attack narratives and reproduced vulnerabilities.
Does PTaaS mean continuous testing?
PTaaS describes delivery; continuous testing describes cadence. A portal may remain available between scheduled assessments. Other services add recurring automated checks or new assessments triggered by material changes. Ask which activities run between engagements and how additional work is scheduled and charged.
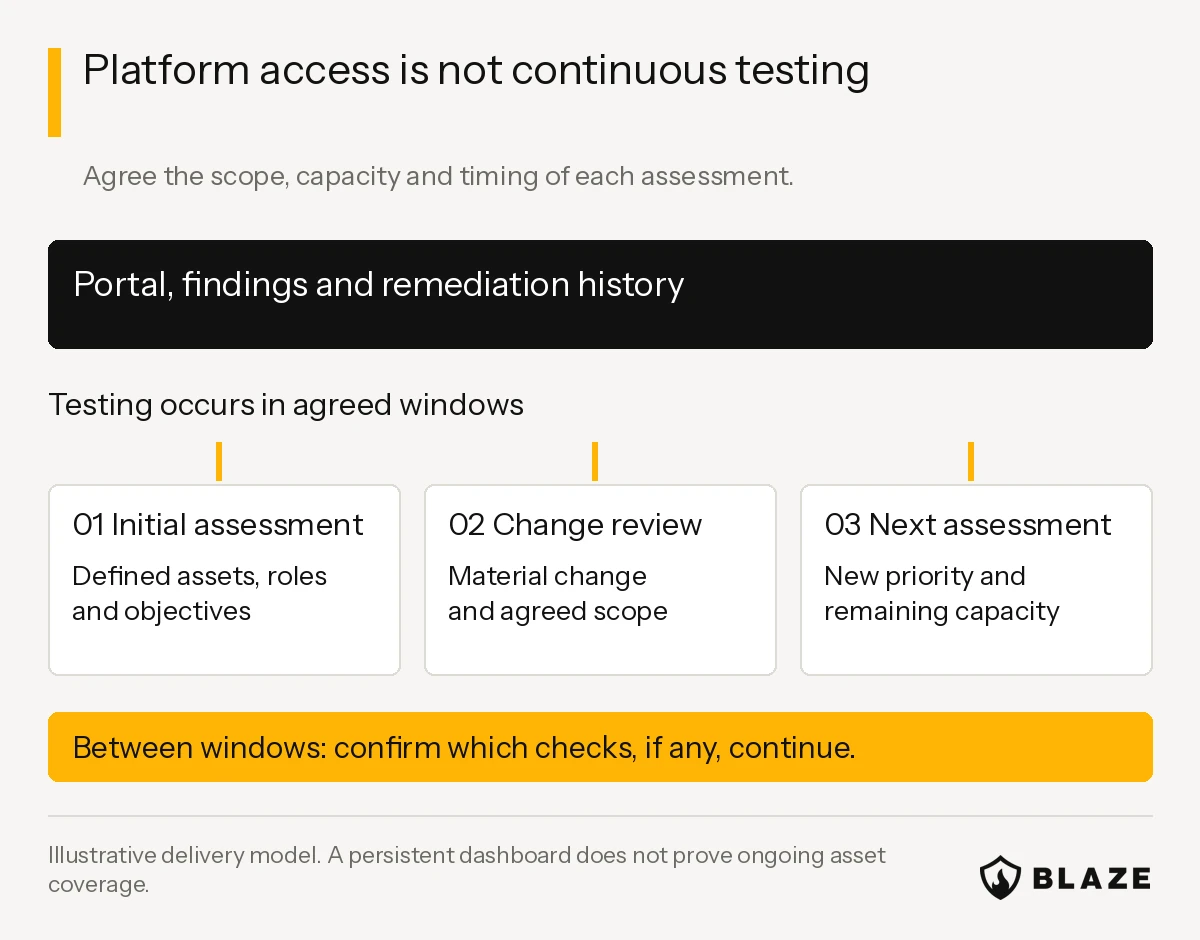
Choose assessment frequency around product risk and material changes. A new authorization model may justify targeted testing before a routine review. Our SaaS and fintech pentest frequency guide explains those decisions.
What are the benefits of PTaaS?
- Earlier visibility into validated findings. Findings shared during testing let developers investigate urgent issues before the final report. The testing team also needs a direct escalation channel for critical discoveries.
- Direct researcher collaboration. Evidence, technical questions and remediation guidance stay connected to the vulnerability. Engineers can clarify prerequisites and verify their understanding before implementing a fix.
- Easier coordination across assessments. Retained environment context, familiar workflows and reusable capacity simplify planning for teams managing several releases or products.
- A connected remediation history. Security teams can follow ownership, exceptions and fix-validation outcomes across engagements. That history supports customer assurance requests and audit preparation.
These benefits depend on the provider's delivery process and the team's ability to act. Compare how a service supports your engineering workflow and important attack surface, alongside its interface.
What can PTaaS test?
PTaaS can support penetration testing services for web applications, APIs, mobile apps, cloud environments, networks and AI-enabled products. The provider's expertise and the assessment scope determine the coverage and access required.
| Asset type | Example objectives | Preparation |
|---|---|---|
| Web applications | Authentication, authorization, business logic and tenant isolation | URLs, roles, test accounts and critical workflows |
| APIs | Object access, permissions, input handling and workflow abuse | API documentation, tokens, roles and example requests |
| Mobile applications | App-side controls and agreed backend interactions | iOS/Android builds, devices or setup, accounts and explicit API scope |
| Cloud environments | Identity permissions, configuration and permitted attack paths | Account/project boundaries, architecture and agreed access |
| Networks and infrastructure | Exposed services, privileges and segmentation | Internal/external ranges, starting position and testing windows |
| AI and LLM applications | Data exposure, prompt injection and tool permissions | Model/application context, connected tools and safety constraints |
For SaaS products, specify authenticated roles, tenant boundaries and sensitive workflows. Our SaaS penetration testing guide explains those boundaries. Include connected APIs and cloud resources explicitly when they are part of the assessment objectives.
PTaaS vs traditional pentesting, scanning and bug bounty
PTaaS and project-based penetration testing can both deliver deep manual assessments, early escalation, actionable remediation guidance and formal reports. The main difference is how work is purchased, coordinated and tracked over time.
| Decision | Project-based pentest | PTaaS program |
|---|---|---|
| Scope | Defined for the assessment | Defined for each assessment within the program |
| Purchase | Effort and deliverables quoted per project | Capacity, assessments or assets under agreed terms |
| Scheduling | Testing window confirmed per engagement | Requests and windows managed against available capacity |
| Findings | Early escalation can accompany a formal report | Live findings and history can accompany formal reports |
| Retesting | Included or separately scoped, as agreed | Managed under the program’s allowance and limits |
| Technical depth | Depends on expertise, scope, access and effort | Depends on expertise, scope, access and effort |
Vulnerability scanning is a testing technique for broad, repeatable discovery of potential weaknesses. A penetration test investigates exploitability and impact within an authorized scope. Scanning can form part of either delivery model.
Bug bounty programs commonly reward participating researchers for valid discoveries. Their incentive and participation model differs from a scoped assessment with defined objectives and a coverage record. Our PTaaS, pentest and bug bounty comparison explores when each approach is useful.
When PTaaS fits—and its limitations
PTaaS is a practical fit for teams shipping frequent material changes, managing several products or handling recurring assurance requests. A stable application with one customer deadline may be well served by a project-based pentest.
Capacity and scope remain finite, and engineering must own remediation. Confirm scheduling commitments and retest allowances before planning around them. PTaaS complements secure design, code review, continuous monitoring and incident response; these controls serve different purposes in a security program.
How much does PTaaS cost?
Blaze annual PTaaS plans start at $19,999 USD for 15 credits, valid for 12 months. One credit equals one day of penetration testing, and each assessment requires a minimum of three credits. See the current PTaaS plans and inclusions for details.
PTaaS pricing commonly uses testing days, credits, assessments, assets or subscription tiers. Compare the annual cost of equivalent scope and technical depth, including follow-up work. An asset count alone may conceal differences in roles, workflows and application complexity.
Establish what each unit buys, minimum assessment sizes, how scope changes consume capacity, and whether reporting and retesting are included. Check expiry, rollover, overage charges, cancellation terms and concurrent-assessment limits.
Illustrative annual-capacity example: a proposed plan contains 20 testing days. Suppose the plan allocates eight to an application/API assessment, six to a second product, four to targeted follow-up testing and two to fix validation. That allocates all 20 days. If setup or reporting also uses that allowance, the plan must reserve capacity for it or fund additional work. This is budgeting arithmetic, not a Blaze quote or a recommendation for assessment duration.
For current Blaze terms, see annual PTaaS plans and how credits work. Our penetration testing cost guide explains the factors behind assessment effort.
What should a PTaaS assessment deliver?
A useful assessment connects its objectives to testing coverage, validated vulnerabilities and follow-up outcomes. Detailed reports should make the work understandable to security leaders and actionable for developers.
- Assessment context: tested assets, environment or build, testing dates, roles and starting access.
- Coverage record: examined workflows and trust boundaries, exclusions, inaccessible areas and limitations.
- Actionable findings: affected assets, attack prerequisites, reproducible evidence, impact and remediation guidance.
- Fix-validation results: specified fixes, versions, retest dates, outcomes and residual issues.
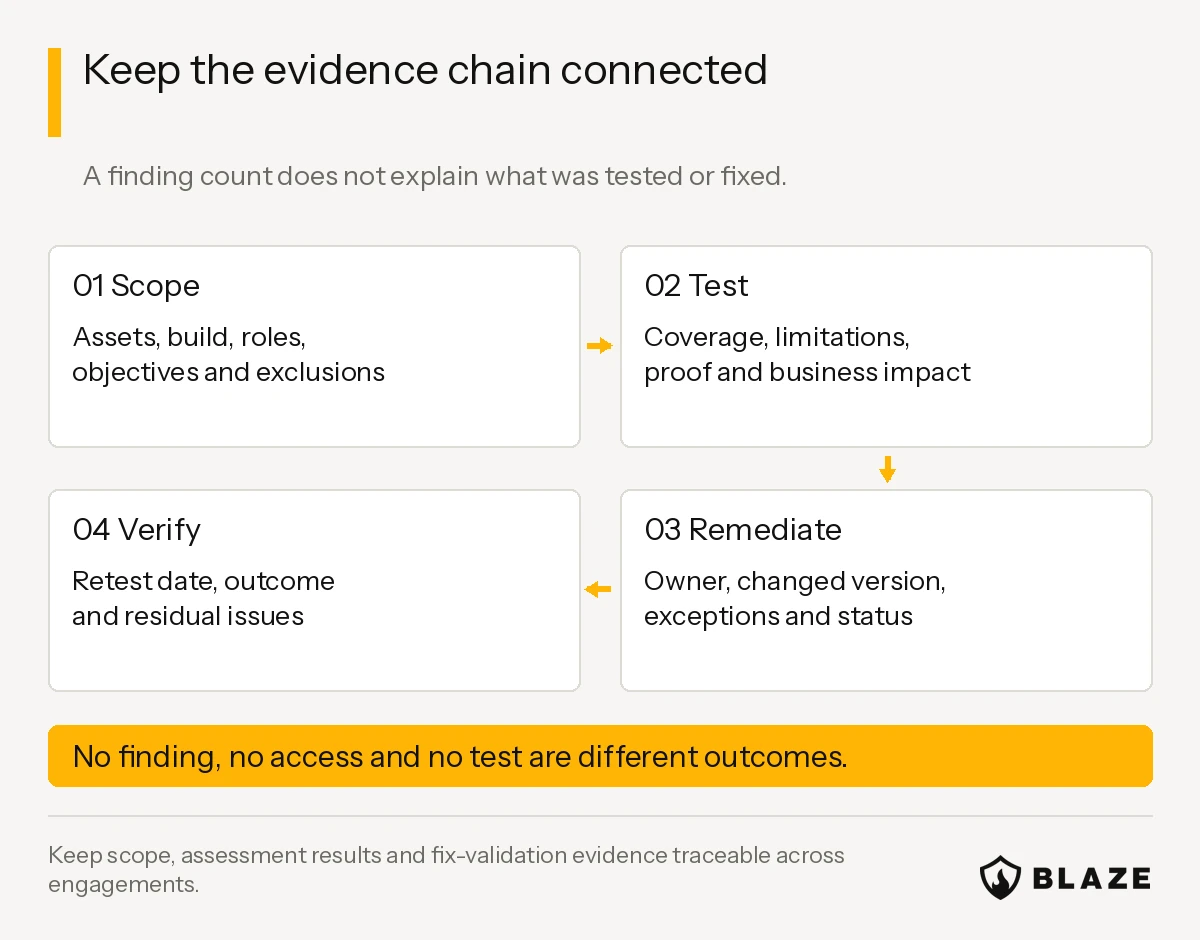
In the SaaS example, the record might show tenant isolation tested for invoice retrieval, an export workflow blocked by missing access, and payment processing excluded. Zero findings in those areas would represent different outcomes. A coverage record helps evaluate the assessment; a vulnerability count alone cannot establish thoroughness.
The technical pentest report explains findings and assessment context. A pentest attestation letter provides a less sensitive summary for authorized recipients. A retest statement records specified fix-validation results. Confirm the recipient's requirements for scope, timing, independence and evidence when arranging compliance support or a customer security review.
How do you evaluate a PTaaS provider?
Evaluate the security work and the collaboration process together. Use a focused checklist when reviewing proposals:
- Relevant expertise and quality assurance. Who performs and reviews the assessment? Look for experience with your technologies, architecture and attack paths, supported by an explanation of methodology and review.
- Delivery commitments. Separate request acknowledgment, assessment start, urgent escalation, reporting and retest turnaround. Establish what happens when access or readiness delays the work.
- Integrations and developer workflow. Distinguish exports from two-way synchronization. Confirm supported fields, attachments, permissions and error handling. A connected ticket does not mean a manual assessment runs on every deployment.
- Evidence protection and portability. Review portal access controls, researcher access, credential handling, retention and deletion. Confirm how reports, findings and attachments can be exported, including at contract end.
The Blaze integration catalog lists current connections and availability. Our penetration testing provider-selection guide expands on technical and organizational fit.
How Blaze delivers PTaaS
Blaze combines expert manual penetration testing, AI-assisted analysis and the Blaze Portal for validated findings, researcher collaboration and reporting. Annual credits provide reusable testing capacity across agreed scopes. Each assessment has confirmed access, readiness and a testing window.
Explore the PTaaS service and current plans, or talk to an expert about your applications, testing objectives and assurance requirements.