The NIS2 implementing regulation, Commission Implementing Regulation (EU) 2024/2690, requires covered entities to establish and apply security testing policies and procedures. The need, scope, frequency and type of tests must follow a risk assessment. Tests must use a documented methodology, results must be recorded, and critical findings require mitigating action.
For security and compliance teams, the practical task is to connect those obligations to the systems being tested, the reasons for choosing each assessment, and the evidence of follow-up. ENISA's technical implementation guidance offers methods and evidence examples, but it is non-binding and does not prescribe every example for every organization.
This guide is written primarily for security and compliance teams at the digital-service entities covered by Regulation 2024/2690. Other organizations within NIS2's scope can use its testing approach for planning, while checking their own applicable national and sector requirements.
This guide focuses on security testing and the supporting risk-management requirements. The regulation also defines significant-incident criteria, which are outside this article's testing focus. For the directive's wider scope and obligations, see our NIS2 Directive overview.
Who does the NIS2 implementing regulation apply to?
Adopted by the European Commission, Regulation 2024/2690 sets technical and methodological requirements for cybersecurity risk management for specified types of essential and important entities within NIS2's scope:
Domain name system service providers (DNS service providers) and top-level domain name registries.
Cloud computing service providers, data center service providers and content delivery network providers.
Managed service providers (MSPs) and managed security service providers (MSSPs).
Providers of online marketplaces, online search engines and social networking services platforms.
Trust service providers.
The regulation is not a testing checklist for every organization covered by NIS2. Determine whether the relevant legal entity and services fall within its scope, which authority has jurisdiction, and what applicable national guidance requires. A supplier or SaaS label alone does not establish applicability.
The official text of Regulation 2024/2690 is the reference for legal requirements. Its Annex organizes cybersecurity risk-management measures into 13 areas: policy on the security of network and information systems; risk management; incident handling; business continuity and crisis management; supply chain security; secure acquisition, development and maintenance; effectiveness assessment; basic cyber hygiene practices and security training; cryptography; human resources security; access control; asset management; and environmental and physical security. Security testing supports parts of this framework, rather than replacing those other measures.
What is binding, and what is ENISA guidance?
The regulation's requirements and ENISA's implementation advice serve different purposes. Keeping them separate helps avoid turning a useful testing technique into an unsupported claim about what the law mandates.
Regulation: binding requirements for relevant entities, subject to the conditions and qualifications in the legal text.
ENISA guidance: indicative implementation advice, examples of evidence, tips and mappings to standards and national frameworks.
Blaze implementation examples: practical ways to apply testing to a particular environment, selected according to risk and operational constraints.
The European Union Agency for Cybersecurity (ENISA) published its NIS2 Technical Implementation Guidance in June 2025. The final guidance is version 1.0. Following the guidance does not itself establish conformity, and its evidence examples are not a universal mandatory document list. Entities should also follow relevant guidance from their national competent authority.
Security testing requirements and evidence
Security testing appears across several parts of the Annex. The table separates the regulatory requirement from ENISA guidance and possible evidence. Evidence should match the actual implementation and assessment scope.
Annex point | Regulatory requirement | ENISA guidance or evidence examples |
|---|---|---|
6.2: Secure development life cycle | Establish security testing processes in the development life cycle and appropriately select, protect and manage test data. | Choose suitable software testing methods; retain development/testing records, results and evidence of test-data protection. |
6.4: Change management | Apply controlled procedures to releases, modifications, emergency changes and configuration changes, including documentation and risk-based testing and impact assessment before implementation. If emergency procedures cannot be followed, document the result and the reason. | Keep change records, assessment results, approvals and evidence of the procedures used. |
6.5: Security testing | Establish and apply a testing policy and procedures; determine need, scope, frequency and type from risk; use a documented methodology; record results and mitigating actions; mitigate critical findings; review policies at planned intervals. | Consider suitable assessment methods and retain policies, schedules, responsibilities and test reports. |
6.8: Network segmentation | Segment networks according to risk; review and, where appropriate, update segmentation at planned intervals and after significant incidents or changes to operations or risks. | Pentest or scan reports, segmentation review records and architecture/change documentation can support the evidence trail. |
6.10: Vulnerability handling and disclosure | Monitor vulnerability information; perform scans where appropriate at planned intervals and record results; address vulnerabilities critical to operations without undue delay. | Assessment reports, vulnerability records, mitigation plans and verification of fixes can support the process. |
Section 7: Effectiveness assessment | Establish and apply policies and procedures to assess whether cybersecurity risk-management measures are effectively implemented and maintained. | Possible assessment methods include vulnerability assessments, pentesting, code review, audits and performance monitoring. |
The final ENISA guidance reproduces the requirements and explains implementation options: secure development on pages 79–82, change management on pages 85–88, security testing on pages 89–91, segmentation on pages 98–100, vulnerability handling on pages 103–106, and effectiveness assessment from page 107.
Does NIS2 require penetration testing?
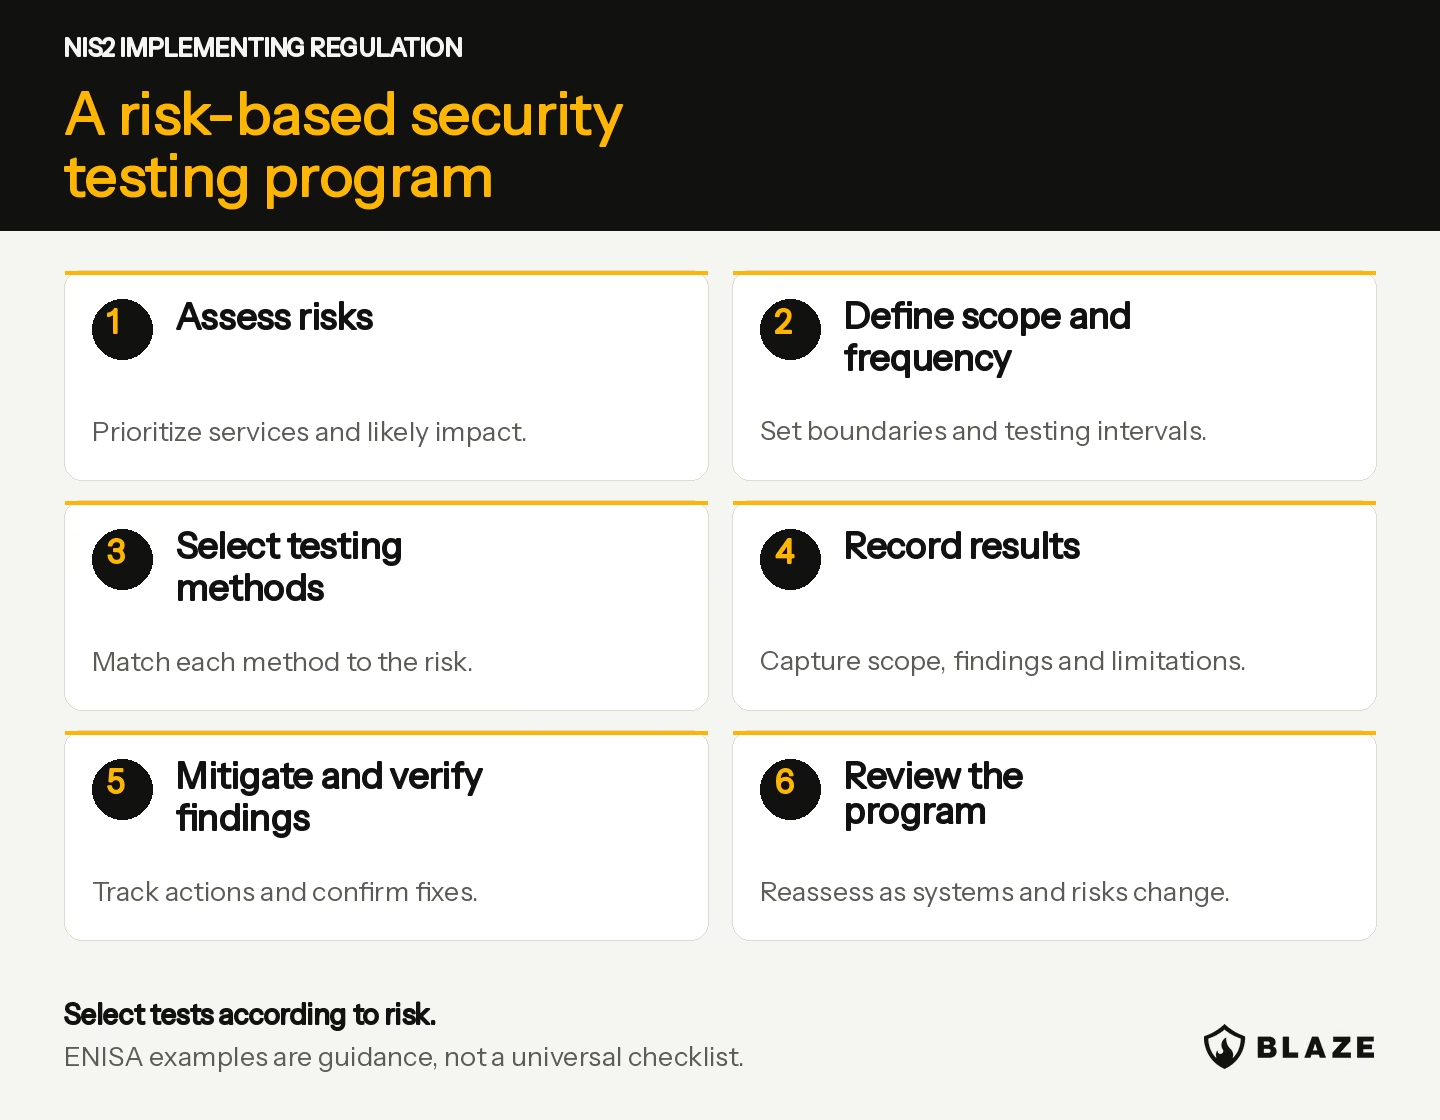
Regulation 2024/2690 requires a risk-based security testing process; it does not impose one identical penetration test on every covered entity. Under Annex point 6.5.2, the organization determines the need, scope, frequency and type of security tests from its risk assessment.
ENISA lists penetration testing among the methods to consider alongside vulnerability assessments, code reviews, red teaming, attack simulations and other techniques. It calls for selecting appropriate methods for the procedure, service or tool being tested. It does not require commissioning every technique.
Penetration testing is useful when the question concerns exploitability or attack paths: whether an exposed application permits access to another tenant, for example, or whether a compromised account can reach a protected service. A scan serves a different purpose. Our penetration testing versus vulnerability scanning comparison explains how the methods complement each other.
What should a security testing policy contain?
Annex point 6.5.1 establishes the policy and procedure obligation; points 6.5.2 and 6.5.3 address how testing is chosen, performed, documented and reviewed. A usable policy should connect these requirements to day-to-day decisions.
Use the following as a practical drafting checklist, rather than an additional statutory document template:
Purpose and ownership: identify the policy owner, decision makers, testing responsibilities and escalation contacts.
Risk basis: explain how risk assessments determine testing need, priorities, scope, methods and frequency.
Scope and methodology: identify relevant systems, test objectives, exclusions and the documented methods to follow.
Authorization and safeguards: define permission to test, permitted activities, production constraints, test-data handling and third-party boundaries.
Records: capture test type, scope, timing, results, finding criticality and mitigating actions.
Follow-up: assign findings, track mitigation, define how important fixes are verified and escalate unresolved risk.
Review: set policy review intervals and triggers for reassessing the program.
Keep the distinction between a policy review interval and a testing interval. ENISA recommends reviewing the testing policy and procedures at least once every two years; that does not mean penetration testing is required only every two years, or that every system should follow the same schedule.
How should you choose testing scope and frequency?
The regulation does not set a universal annual penetration testing interval. Establish a defensible cadence for your environment, considering the services and systems involved, their exposure, the consequences of compromise and changes in risk. Check any additional applicable requirements before finalizing that cadence.
For practical planning, consider:
Systems supporting critical operations and the business impact of failure.
Internet-facing applications, APIs, remote access and privileged administration.
Changes to software, identity controls, architecture, integrations and network boundaries.
Previous findings, incidents, threat information and the status of mitigations.
Supplier permissions, production safety, access to test environments and maintenance windows.
These are planning considerations, not a mandated frequency formula. Record why a method and scope answer the identified risks. Reassess the plan when conditions change rather than treating the previous year's scope as a permanent default.
What should you include in a security testing brief?
Translate the policy and risk assessment into a brief that your internal team or testing provider can use. This is a practical planning checklist, not an additional regulatory template:
Service and impact: identify the service being protected and the consequences of disruption or compromise.
Systems and dependencies: list supporting applications, APIs, cloud environments, networks, identities and supplier integrations.
Objectives and starting access: define the questions testing should answer, available accounts, privilege levels and trust boundaries.
Authorization and safeguards: agree targets, supplier permissions, exclusions, production constraints, test-data handling and escalation contacts.
Reporting and follow-up: specify methodology and limitation records, validated findings, remediation guidance, internal owners and how progress will be tracked.
Fix validation: agree whether retesting is included, which fixes it covers and how results will be documented.
Practical testing examples for implementation
The examples below are Blaze implementation suggestions. They illustrate how security testing can answer operational questions; they are not separate ENISA mandates. Blaze's NIS2 penetration testing services can support this work through scoped assessments, validated findings and remediation guidance.
Secure development and changes
For an application handling customer administration, combine automated checks with web application and API penetration testing focused on authorization and sensitive workflows. After a change to tenant access controls, test the changed behavior and relevant regression paths. Retain the scope, results, release decision and remediation records.
Network segmentation and privileged access
Test whether defined starting accounts and systems can reach services they should not access. Network penetration testing can assess these paths across internal or external infrastructure. In cloud environments, cloud penetration testing can assess whether an identity's permissions allow access to another workload or escalation to a privileged role. Compare the observed paths with the intended network and access-control design. Results can show where segmentation restricts the tested paths and where it fails; they do not prove that all lateral movement is impossible.
Vulnerability handling and retesting
Within vulnerability management, connect scan and assessment findings to affected assets, business impact, owners and mitigation decisions. Verify important fixes with a suitable retest or other relevant evidence, and retain the outcome. A completed ticket alone may not answer whether the exploitable condition was removed.
Suppliers, recovery and detection
For supplier-connected systems, assess your own integration and authorized boundaries. Testing a supplier's infrastructure requires appropriate permission. Where detection and response are the objectives, Adversary Simulation, including red and purple teaming, can assess selected attack scenarios and the defensive response. Select these exercises according to risk and readiness rather than treating them as a mandatory addition to every pentest. Recovery exercises address restoration separately; do not assume a pentest proves recovery capability or complete monitoring coverage.
How does testing fit into wider cybersecurity risk management?
A testing program should sit within the organization’s risk management framework. Organizations that need help assigning ownership, developing practical policies or coordinating a testing roadmap can consider Fractional CISO / vCISO & Advisory support. Management retains its approval and oversight responsibilities. Security audits, assessments and operational metrics answer different questions about security measures; together they help management bodies decide what to improve and which residual risks need attention.
For essential and important entities providing digital services, useful test objectives follow the service: which security flaws could interrupt delivery, expose customer data or compromise privileged access? Choose appropriate security measures and assessment methods for those risks, then use the results to update security policies and relevant procedures.
Business continuity management: business continuity plans and backup recovery need exercises that assess restoration. A penetration test can identify weaknesses that contribute to disruption, but it cannot establish that recovery works without testing that capability.
Incident response: incident response readiness depends on people, escalation routes, logging and response actions. As a Blaze implementation example, an authorized detection exercise can assess how teams handle selected cyber threats. Record its scope and limitations rather than extrapolating to every incident.
Control-specific validation: a test of access control, network security or multi-factor authentication should state what was assessed and under what conditions. This makes evidence useful for improving the cybersecurity posture and protecting sensitive data, without implying that one report validates the whole program.
How to document testing and remediation evidence
A useful evidence trail explains the decision, activity, result and response. Organize it so a reviewer can trace a requirement or risk to the work performed:
Requirement and risk: identify the relevant Annex point, service, asset and reason for testing.
Test plan: record objectives, methodology, authorization, scope, dates and limitations.
Findings: retain results, affected components, severity reasoning and operational implications.
Action: assign ownership, mitigation steps, target dates and any documented risk decisions.
Verification: record retest results or other evidence that addresses the finding, including remaining limitations.
Review: update risk assessments, procedures or future testing priorities where the findings justify it.
For an external penetration testing engagement, agree the expected deliverables before work begins: scope and methodology, limitations, validated findings with reproduction steps and business impact, remediation guidance and an executive summary. When fix validation is included, retain the retest results alongside the original findings. Your organization still needs to assign remediation owners and record its risk decisions.
This workflow is a practical way to organize records, not a guarantee of regulatory acceptance. A pentest report can support specific controls, but it does not replace the wider risk-management program, management responsibilities or national supervision.