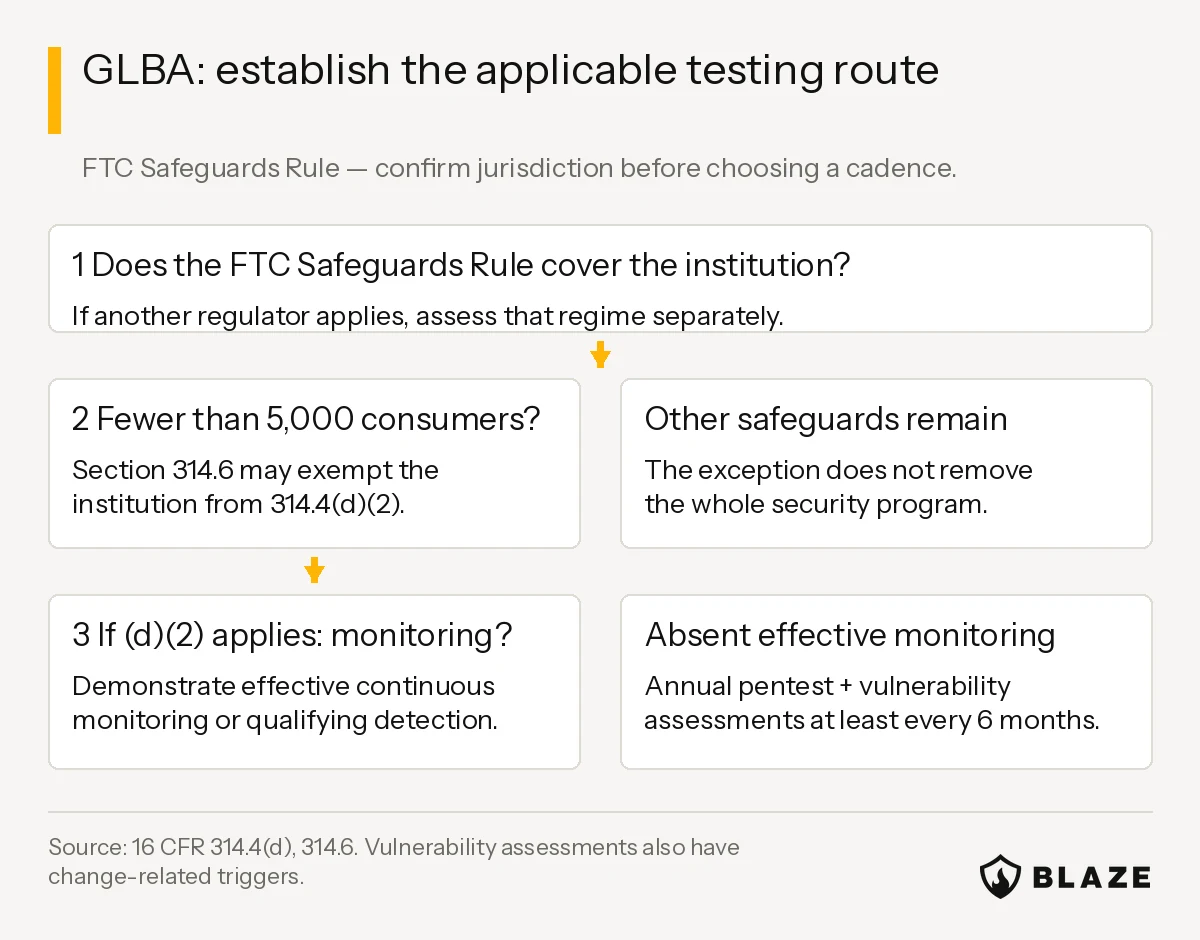
The FTC Safeguards Rule has a conditional annual penetration-testing requirement, not a universal rule for every organization associated with GLBA. For institutions subject to 16 CFR 314.4(d)(2), the rule allows effective continuous monitoring or other qualifying ongoing detection systems. Without those, it specifies annual penetration tests and vulnerability assessments at least every six months, with additional change-related triggers.
A separate small-institution exception also matters. This guide explains the decision points, newer FTC guidance and how to prepare a useful assessment without turning a report into a promise of compliance.
Which GLBA obligations does this guide cover?
The Gramm-Leach-Bliley Act spans multiple regulators. This article focuses on the FTC Safeguards Rule, which covers financial institutions within the FTC’s jurisdiction rather than institutions supervised under another GLBA regulator. Determine coverage from the business’s activities and regulator, not from its name.
Nonbank lenders, certain financial advisers and businesses that arrange consumer financing may fall within the rule. Banks and insurers require analysis under their applicable supervisory regimes. A service provider handling customer information can also face contractual security requirements without becoming a covered financial institution on that fact alone.
Have the compliance owner confirm the applicable rule before using a testing frequency in a procurement document. A customer’s questionnaire, a contractual commitment and a statutory duty are different sources of obligation.
Does GLBA require penetration testing?
Under 16 CFR 314.4(d)(2), absent effective ongoing monitoring or qualifying detection, the baseline is annual risk-informed penetration testing, plus vulnerability assessments at least every six months and when material operational/business changes or other circumstances materially affect the program. The regulation does not make buying a monitoring product sufficient on its own.
Assess and document whether the implemented monitoring actually provides the relevant ongoing visibility. If that case cannot be demonstrated, use the periodic-testing path. The Qualified Individual and compliance owner should be able to explain the decision and the supporting evidence.
The fewer-than-5,000-consumers exception
Section 314.6 excludes institutions maintaining customer information about fewer than 5,000 consumers from specified provisions, including 314.4(d)(2). It does not remove the entire information-security-program obligation, and 314.4(d)(1)’s general control-testing or monitoring requirement remains. The threshold concerns consumer information, not employee count, office size or the number of applications.
Maintain the population calculation and reassess it as the business changes. An institution below the threshold may still need a pentest because of its risk profile or customer commitments. Present that as a justified security or contractual decision rather than an automatic statutory annual requirement.
A practical testing decision sequence
- Confirm jurisdiction: identify the covered legal entity and the applicable regulator.
- Check the exception: document whether Section 314.6 applies and which duties remain.
- Assess monitoring effectiveness: record coverage, gaps, ownership and evidence supporting any reliance on ongoing monitoring.
- Set the testing plan: define the periodic and change-triggered work appropriate to the applicable provisions.
- Close the loop: route findings into remediation and program decisions.
Avoid importing PCI DSS scanning terminology or NYDFS cadence into this decision. For example, a GLBA vulnerability assessment should not be described as a PCI Approved Scanning Vendor requirement. If multiple frameworks apply, map each obligation separately and reuse compatible technical evidence.
What newer FTC guidance adds for buyers
In June 2025, the FTC published dealer-specific guidance. Its automobile-dealer FAQs explain how financing and leasing activities can bring dealers within scope and clarify customer-information handling. These are FTC staff guidance, not a new 2026 annual-pentest amendment.
For a dealer assessment, map the financing journey: application forms, document uploads, credit information, dealership systems, lender connections and access by staff or suppliers. Confirm which records contain protected customer information rather than treating every sales or service record identically. Those distinctions help allocate testing effort to the paths with meaningful exposure.
The FTC also added breach-notification provisions effective in May 2024. A qualifying event involving at least 500 consumers requires notice as soon as possible and no later than 30 days after discovery. This is separate from the pentest cadence. A planned test should use a clear escalation process if evidence suggests an actual incident; the incident team must evaluate reporting obligations rather than assume every test finding is a reportable breach.
Scope the assessment around customer-information flows
For GLBA-related security testing, start with where information is collected, used, stored, shared and deleted. Translate the map into systems and security assumptions the assessment can examine. A narrow perimeter test might miss an authorization failure in a document portal or a privileged cloud role that can access financing records.
- Customer applications and APIs: authentication, account recovery, object-level authorization, sensitive exports and transaction workflows.
- Identity and administration: privileged roles, delegated access, remote administration and paths from ordinary users to sensitive functions.
- Infrastructure and cloud: exposed services, storage access, secrets and permitted attack paths.
- Third-party connections: data transfers and trust relationships the institution can authorize for testing.
Create representative accounts and synthetic records so the tester can evaluate access controls without copying real customer files unnecessarily. Agree restrictions for production systems, shared services and any supplier-operated environment.
Continuous monitoring and a pentest answer different questions
Ongoing monitoring helps observe changes and suspicious activity. A scoped penetration test attempts to demonstrate whether a security boundary can be crossed. A vulnerability assessment inventories and evaluates potential weaknesses. These capabilities can complement each other, but the evidence for one should not be relabeled as another.
For example, an asset-monitoring system may detect a new internet-facing endpoint. That does not establish whether an authenticated user can retrieve another customer’s application. Conversely, a successful application pentest does not prove that the organization can detect newly exposed assets between assessments.
When buying either service, ask what it covers, what it cannot observe and how failures are escalated. Record those limitations in the security program rather than leaving them inside a vendor’s product description.
Evidence and remediation: what to request
Ask for a clear scope record, testing dates, methodology, starting access, exclusions and evidence supporting each finding. Useful reports explain attack prerequisites and business impact, not just severity labels or lists of vulnerable software versions.
- Link each finding to an affected asset and business owner.
- Prioritize remediation according to exposure and impact, with tracked actions.
- Keep risk acceptance explicit and separate from technical closure.
- Validate fixes against the original exploit conditions and preserve remaining limitations.
- Use results to improve the next assessment and monitoring plan.
A practical management summary should identify what was tested, what remains uncertain and what decisions are needed. Do not treat a clean scan or a pentest attestation as a certification that the entire institution complies with GLBA.
How often should you retest after changes?
Set an intake process for security-relevant changes such as new financing integrations, authentication changes, migrations or acquisitions. Determine which controls and customer-information flows changed, then select proportionate testing. A targeted review after a change and the annual assessment can serve different purposes; one should not silently replace the other.
Agree fix-validation scope and timing when purchasing the assessment. The engagement should state what retesting includes, how evidence is shared and how newly introduced weaknesses will be handled.