TISAX penetration testing should be scoped around the applicable ISA requirements, assessment objectives and the systems supporting them. Avoid assuming that every participant needs the same test, or that a single report guarantees a successful TISAX assessment.
This guide explains where technical testing fits, how to prepare evidence and what the ISA2027 transition means for assessments ordered in 2027. It distinguishes the security testing Blaze can perform from the formal TISAX assessment carried out by an approved audit provider.
What is TISAX, and what does a successful assessment produce?
TISAX, the Trusted Information Security Assessment Exchange, is an automotive-industry assessment and results-sharing mechanism operated by ENX. Participants select objectives and an assessment scope reflecting business-partner requirements. An approved audit provider evaluates the relevant information-security arrangements.
The outcome is an assessment result and corresponding TISAX labels, shared through the ENX Portal. Use that terminology rather than presenting TISAX as an ISO-style certification. The ENX Participant Handbook explains registration, assessment and exchange.
An independent penetration test can supply technical evidence, but the pentest provider does not award the TISAX label. Confirm the expected evidence and applicable catalogue with your audit provider before commissioning the work.
Does TISAX require penetration testing?
The answer depends on the applicable ISA catalogue, protection needs and requirements relevant to the assessment. Read the actual requirement and its applicability rather than turning an example technique into a universal annual mandate—or declaring that technical verification is always optional.
ISA 6 includes technical-checking and application-security requirements where penetration testing is a possible method of verification. Controls 5.2.6 and 5.3.1 address technical checks and security in new or changed systems. A testing plan should explain how it supports the applicable requirement and which other evidence remains necessary.
Use the official ENX ISA downloads and agree applicability with the assessment owner. Control identifiers and wording must be interpreted in the specific version being used.
ISA2027: what changes for new assessment orders?
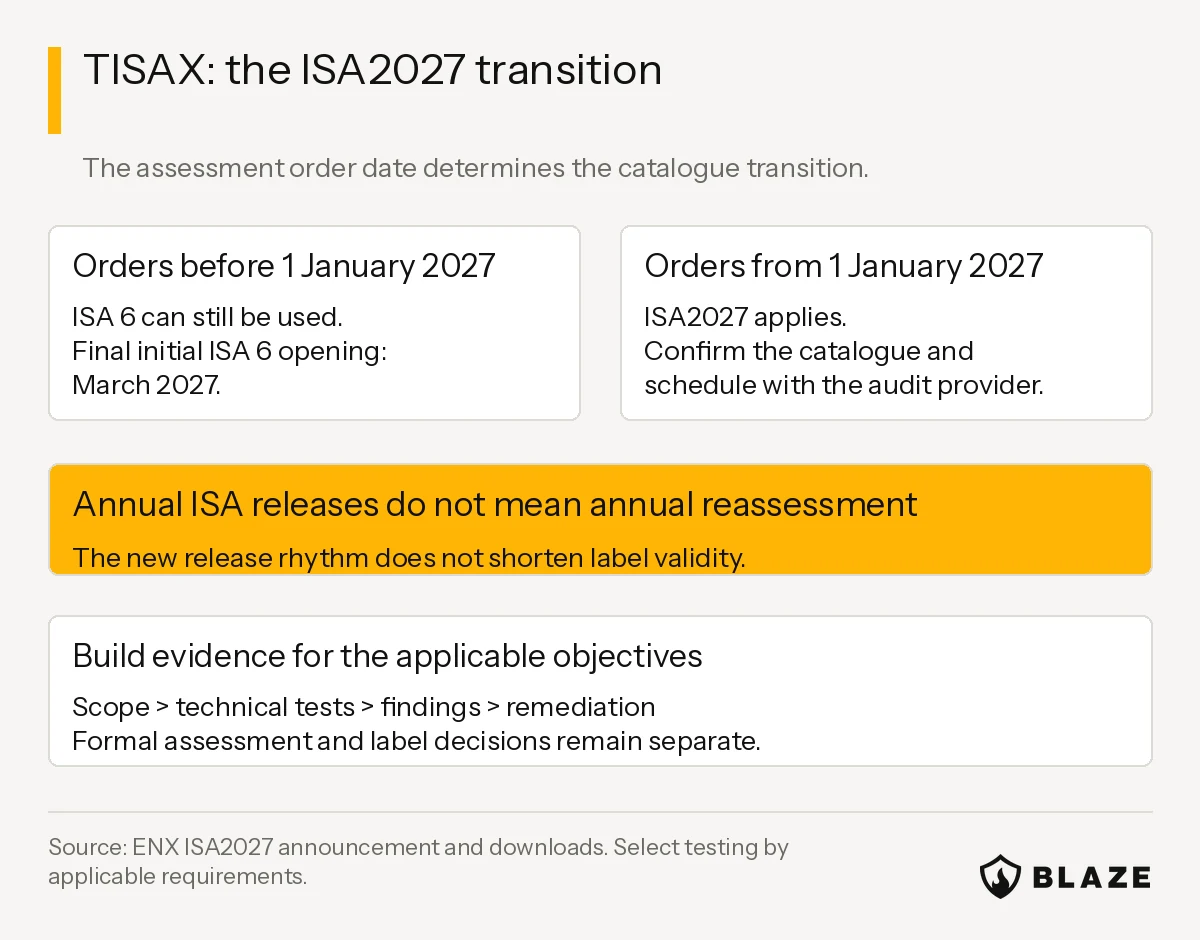
ENX announced ISA2027 in July 2026. It applies to TISAX assessments ordered from January 1, 2027. Assessments ordered before that date can still use ISA 6; ENX’s download guidance notes March 2027 as the final month to open an initial ISA 6 assessment.
The new year-based catalogue naming also introduces annual releases. Annual catalogue publication does not mean annual TISAX reassessment or an automatic annual pentest requirement. ENX states that label validity is unaffected by the new publication rhythm and remains up to three years.
For work spanning the transition, confirm the order date, applicable catalogue and assessment schedule with the audit provider. Map your testing objectives to that catalogue before execution. Do not reuse ISA 6 control references as though their numbers and wording are guaranteed to remain unchanged in ISA2027.
Define the technical scope from the assessment scope
A useful pentest scope describes the assets and security boundaries supporting the protected information or business process. It should be specific enough for a tester to execute and for an assessor to understand the evidence.
- Information and process: identify the relevant engineering, supplier, customer or prototype-related information and where it flows.
- Applications and APIs: include relevant portals, file exchanges, authorization roles and sensitive operations.
- Identity and infrastructure: consider privileged access, remote connectivity, segmentation and paths into sensitive environments.
- Cloud and suppliers: identify customer-controlled resources and the permissions needed to test integrations.
- Boundaries and exclusions: record sites, systems and techniques outside the engagement, and how their risks will be addressed.
For example, a supplier portal may be within the assessment scope while its document storage sits in a separate cloud account. Testing only the portal’s public landing page would not answer whether one supplier can retrieve another supplier’s documents. Representative roles and safe test records are needed to assess that boundary.
Choose methods that fit the target
Select procedures from the technology and agreed objectives. OWASP WSTG can structure web testing; OWASP ASVS can help specify application security requirements. NIST SP 800-115 provides a planning and execution reference for technical assessments.
These references do not automatically make a test TISAX-compliant. The report must show the assets, checks, results and limitations relevant to your objectives. If source review, firmware, industrial systems or physical security are needed, agree that work explicitly rather than assuming it comes with a web pentest.
Vulnerability scanning and penetration testing
Scanning helps identify potential weaknesses repeatedly. A pentest investigates whether selected weaknesses and control failures can be exploited in context. Determine which scanning, technical review and exploit validation activities are needed against the applicable catalogue; a generic statement that scans are merely optional is not a reliable applicability analysis.
Record authenticated scan coverage, unreachable systems and manual checks for gaps. Use a controlled exploit demonstration where it adds evidence. Avoid treating thousands of scanner observations as thousands of verified vulnerabilities.
When should technical testing happen?
Plan work early enough to remediate and validate fixes before the evidence is needed. Use risk, relevant control wording, commissioning, significant changes and assessment timing to determine the cadence. Customer contracts may introduce additional expectations.
A new remote-access service, redesigned identity system or substantial supplier-portal release can justify targeted testing even when an earlier report is recent. Conversely, a new calendar year alone does not establish that an unchanged scope needs the same full assessment again. Document the rationale and confirm it with the responsible assessment owner.
What evidence should you retain?
- The applicable ISA version, assessment objectives and a mapping from relevant requirements to test objectives.
- Written authorization, assets, environments, dates, roles and agreed techniques.
- Coverage, exclusions, access failures and other limitations.
- Reproduced findings with prerequisites, impact and practical remediation.
- Assigned owners, action tracking and retest results.
- A summary explaining which questions the technical work answers and which require other evidence.
Protect the full technical report according to the sensitivity of its contents. Share evidence with the assessor through an agreed channel and avoid unnecessary disclosure of exploitable details to wider audiences. An executive summary and a detailed exploit record serve different readers.
How much time should you allow?
Effort depends on the scope, number of roles and trust boundaries, technology, access, test depth and production restrictions. Allow separate time for preparation, execution, remediation and fix validation. A fixed generic person-day range can be misleading when those assumptions are unstated.
Provide the target inventory, architecture, role matrix and desired evidence when requesting a quote. Ask what is included in retesting and how blockers or scope changes affect delivery. A short engagement can be appropriate for a narrow target; duration alone does not prove quality.
Prepare information for scoping
When requesting TISAX-related penetration testing, supply the applicable catalogue, assessment objectives, target inventory and role matrix. Agree the technical questions the engagement will answer and how findings will be remediated. Formal assessment and label decisions remain with the TISAX process.