SaaS penetration testing is not just web application testing with a different label. A SaaS product usually combines a browser-based application, APIs, cloud infrastructure, tenant data, SSO, integrations, admin tooling, support workflows, and business logic that changes constantly. Testing only the visible application can miss the risks that matter most.
This guide explains what SaaS penetration testing covers, how it differs from a standard web application pentest, which vulnerabilities matter most, and how SaaS companies should approach testing for SOC 2, customer assurance and real risk reduction.
What is SaaS penetration testing?
SaaS penetration testing is a security assessment of a software-as-a-service product and the systems that support it. Unlike a narrow web application pentest, a SaaS pentest usually needs to evaluate the full product attack surface: web application, APIs, tenant boundaries, authentication flows, authorization logic, cloud infrastructure, integrations, admin tooling, support workflows, and sometimes mobile or desktop clients.
SaaS penetration testing may include elements of several types of penetration tests — typically web application, API, cloud, and external infrastructure testing — but it is not the same as any single one of them.
The goal is to understand whether an attacker could access customer data, abuse business logic, cross tenant boundaries, escalate privileges, compromise accounts, manipulate workflows, or use one part of the platform to reach another. That’s why a strong SaaS security assessment tests the product as attackers would experience it: as a connected system.
How SaaS pentesting differs from a standard web application pentest
A standard web application penetration test focuses on a web application and its exposed functionality. That is still an important part of SaaS security testing, but it is not enough for most SaaS products.
SaaS platforms usually introduce additional risk because they are multi-tenant, API-driven, cloud-hosted, integration-heavy, and continuously changing. They often include customer workspaces, role-based access control, billing logic, SSO, OAuth integrations, background jobs, admin panels, support impersonation, data exports, audit logs, and cloud-managed services.
That means SaaS pentesting has to answer questions that a basic web app test may not cover deeply enough:
Can one tenant access another tenant’s data? Can a user change object IDs or API parameters to reach resources they do not own? Can a low-privilege user access admin functions through the API? Can support tooling bypass customer controls? Can cloud storage expose files outside the application? Can SSO, invitations, billing, or integrations be abused to escalate access?
In SaaS environments, the highest-impact findings often come from broken assumptions between layers. The application assumes the API enforces access control. The API assumes the UI hides privileged actions. The cloud storage layer assumes the application has already checked authorization. The support tool assumes employees only use it for legitimate reasons. A SaaS pentest should challenge those assumptions.
What does a SaaS penetration test cover?
The exact scope depends on the product architecture, customer data flows, and business risk. A simple SaaS application may only need web, API, and external infrastructure testing. A mature platform may require a broader scope that includes cloud services, SSO, integrations, internal admin tooling, mobile clients, and tenant-isolation testing.
These are the areas that matter most:
Web application security
The web application is still the main user-facing surface for many SaaS products. Web application penetration testing typically covers authentication, session management, authorization, input validation, access control, file uploads, data exposure, error handling, security headers, workflow abuse, and OWASP Top 10 risks such as cross-site scripting, SQL injection, server-side request forgery, and broken access control.
For SaaS products, authenticated testing is essential. Many meaningful findings only appear after login, when penetration testers can exercise real user roles, account settings, billing flows, exports, admin features, and workspace-level functionality.
A scanner can find some common web issues. It will not understand whether a user in one customer workspace can access another customer’s report, bypass a subscription boundary, or trigger a privileged workflow in an unintended state.
API security
APIs are often the real attack surface of a SaaS product. SaaS platforms use APIs for the web interface, mobile apps, third-party integrations, partner access, internal services, automation, and data export. If API authorization fails, attackers may not need to compromise the front end at all.
API penetration testing should cover broken object-level authorization, broken function-level authorization, weak authentication, excessive data exposure, mass assignment, injection vulnerabilities, rate limiting weaknesses, insecure pagination or filtering, undocumented endpoints, legacy endpoints, and business logic abuse.
The most important API question in SaaS is usually not “does this endpoint work?” It is “who should be allowed to do this, against which object, in which tenant, and under what business condition?”
That is why useful API testing requires context: roles, tenants, example objects, API documentation, Postman collections, OpenAPI or Swagger files, and accounts with different permission levels.
Multi-tenant isolation
Multi-tenant isolation is one of the defining risks of SaaS security.
SaaS platforms serve multiple customers on shared infrastructure while promising that each customer’s data, users, settings, files, and workflows remain separate. A single tenant-isolation failure can expose data across customers and create a much larger blast radius than a single-account vulnerability.
Testing tenant isolation means actively trying to cross those boundaries. Pen testers may manipulate object IDs, workspace IDs, organization IDs, API parameters, export functions, invitations, file paths, search features, reporting endpoints, background jobs, and admin functions to see whether one tenant can access another tenant’s resources.
Common failures include missing ownership checks, improperly scoped database queries, IDOR/BOLA vulnerabilities, authorization enforced in the UI but not the API, shared storage paths, weak tenant scoping in background tasks, and internal tooling that can access customer data without proper restrictions.
This is where automated tools are insufficient and manual testing techniques are especially important. Tenant isolation issues are usually context-specific and depend on understanding how the application is supposed to behave.
Authentication, SSO, and OAuth
Authentication and identity flows are critical in SaaS environments because customers often connect the product to their own identity providers and internal access models.
A SaaS pentest should review login, registration, password reset, MFA, session handling, invitation flows, account linking, SAML, OAuth, OpenID Connect, SSO configuration, role mapping, SCIM provisioning, and tenant membership changes.
Common issues include weak password reset flows, insecure invitation logic, broken account linking, OAuth misconfiguration, overbroad OAuth scopes, weak session invalidation, MFA bypasses, privilege changes that do not invalidate sessions, and SSO role-mapping mistakes that grant unintended access.
These security flaws can be subtle. A flow may look secure in isolation but fail when combined with invitations, workspace switching, billing roles, SSO provisioning, or account recovery.
Admin and support tooling
SaaS products often include internal tooling for support, billing, customer success, fraud review, debugging, impersonation, data correction, and administrative operations.
These tools are high-value targets because they frequently have privileged access to customer data or production workflows. They may also receive less security attention than the customer-facing product.
SaaS pen testing should evaluate whether admin and support tooling is properly authenticated, authorized, logged, segmented, and restricted. It should also test whether support impersonation, customer lookup, data exports, role changes, billing adjustments, and account recovery workflows can be abused.
The key question is not only whether external attackers can reach these tools. It is whether a compromised employee account, overly broad internal role, weak support workflow, or missing approval step could create customer impact.
Cloud infrastructure and storage
Most SaaS products run on cloud infrastructure. That makes cloud security part of SaaS security.
A SaaS pen test may need to include cloud IAM, storage permissions, managed databases, queues, serverless functions, Kubernetes clusters, logs, secrets, CI/CD pipelines, and external infrastructure. If the product stores or processes customer data in AWS, Azure, or Google Cloud, cloud configuration and cloud attack paths can directly affect SaaS risk.
Cloud issues that matter for SaaS include exposed storage buckets, overly permissive IAM roles, leaked access keys, public snapshots, weak security groups, insecure metadata access, secrets in build pipelines, overexposed Kubernetes services, and logging gaps.
Blaze’s 2025 penetration testing data found that cloud security assessments had the highest average vulnerability density of any assessment type, with 14.40 vulnerabilities per project. That is especially relevant for SaaS companies, because their products often depend heavily on cloud infrastructure and managed services.
Integrations and webhooks
SaaS products rarely operate alone. They connect to identity providers, payment processors, CRMs, ticketing systems, chat platforms, code repositories, analytics tools, data warehouses, and customer environments.
Each integration creates trust relationships and data flows that need to be tested.
A SaaS pentest should review OAuth scopes, token storage, webhook signature validation, callback URLs, integration permissions, third-party app installation flows, import/export features, error handling, and whether integrated services can be abused to access data or trigger privileged actions.
Webhook and integration flaws are often missed because they sit between teams: part application security, part API security, part business logic, and part third-party risk.
Business logic and workflow abuse
Business logic vulnerabilities are one of the clearest reasons SaaS pentesting cannot be reduced to automated scanning.
These issues occur when the application works as designed, but the design can be abused. Examples include bypassing subscription limits through direct API calls, exporting data without the same authorization checks as the UI, skipping approval steps in multi-stage workflows, reusing invitation links, manipulating billing states, abusing trial-to-paid transitions, or changing role assignments in unexpected sequences.
There may be no CVE, no missing patch, and no scanner signature. The tester needs to understand the intended workflow, then find where the application fails under adversarial use.
For SaaS companies, these findings are often among the most valuable because they map directly to customer data exposure, privilege abuse, fraud, revenue loss, or compliance impact.
Common vulnerabilities found in SaaS penetration tests
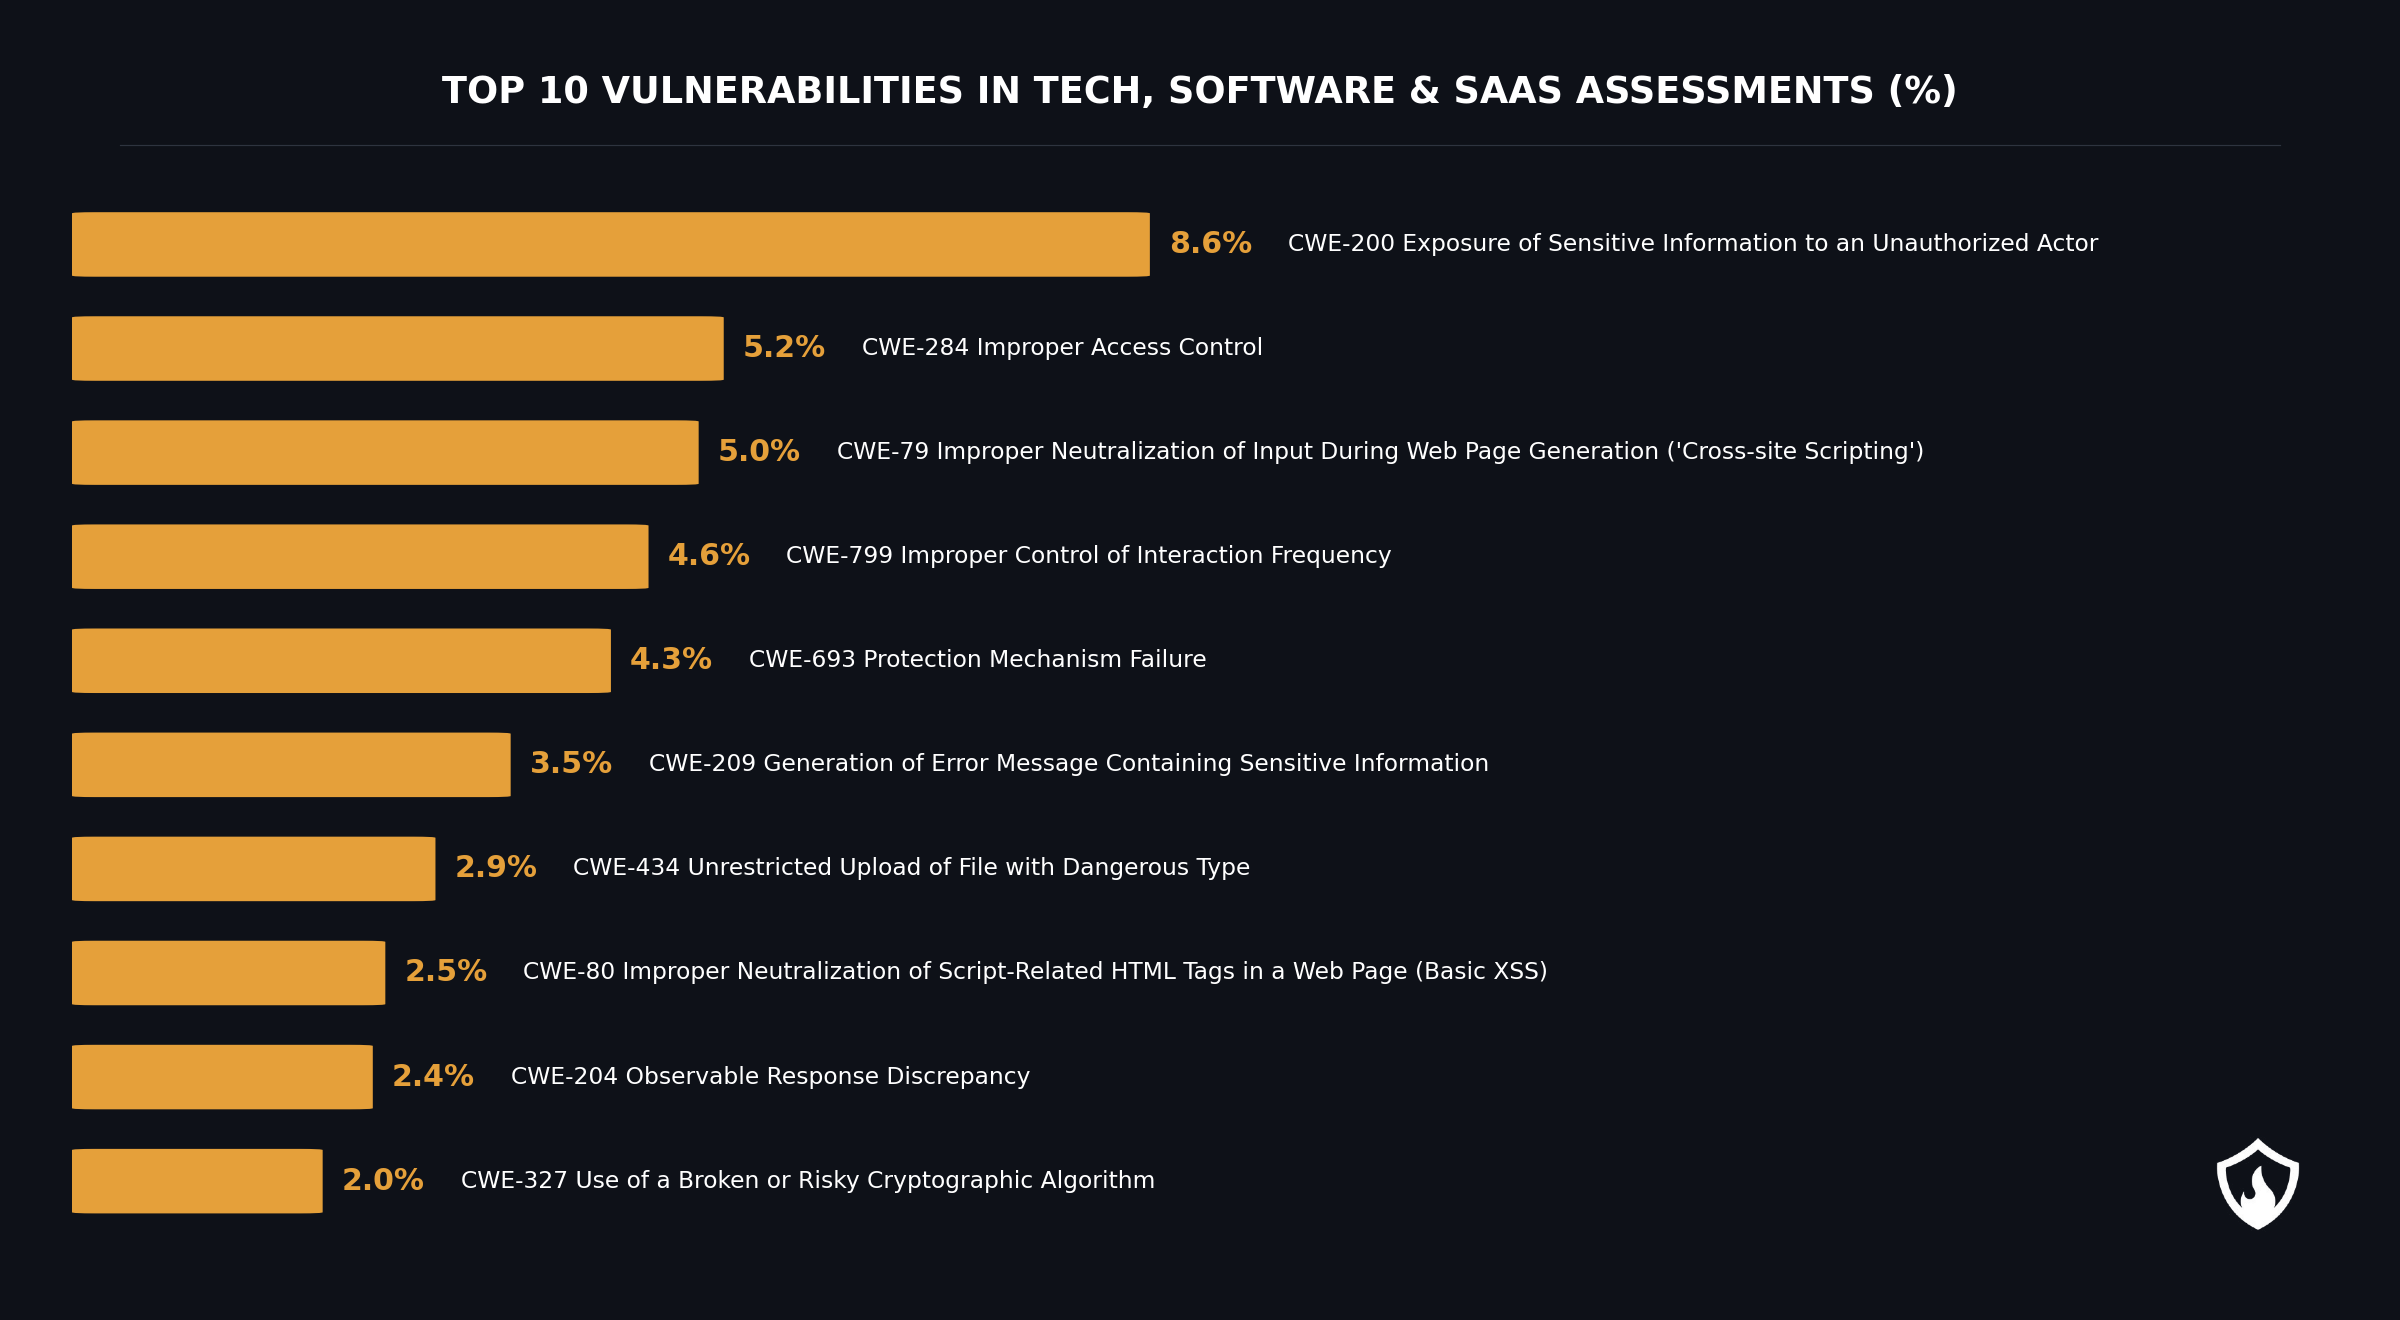
SaaS vulnerabilities vary by product, but the same patterns appear repeatedly in real assessments. The most serious findings are rarely isolated technical bugs. They usually involve broken assumptions about users, tenants, roles, APIs, cloud services, and internal workflows.
For a deeper breakdown of recurring issues we see in SaaS assessments, read our guide to common SaaS vulnerabilities found in penetration tests based on our security assessments of SaaS applications.
Broken access control
Broken access control is one of the most common and highest-impact SaaS findings. It includes users accessing objects, features, tenants, reports, files, exports, or admin functions they should not be able to reach. In SaaS products, broken access control often appears as IDOR, BOLA, missing tenant checks, weak role enforcement, or authorization applied only in the UI.
Tenant isolation failures
Tenant isolation failures occur when one customer can access or influence another customer’s data, configuration, files, reports, users, or workflows.
These vulnerabilities are especially serious because SaaS products are built around shared infrastructure, and one weak boundary can affect many customers.
API authorization gaps
APIs often expose the same business actions as the user interface, but with fewer guardrails. A role that cannot perform an action in the UI may still be able to call the underlying endpoint directly.
API authorization gaps commonly affect object access, admin actions, export functions, hidden endpoints, internal APIs, and legacy functionality.
Authentication and identity flaws
SaaS identity flows are complex. Issues may appear in SSO, OAuth, password reset, invitation logic, MFA, account linking, session handling, SCIM provisioning, and role mapping. A small mistake in identity logic can allow account takeover, unauthorized tenant access, or privilege escalation.
Cloud and storage misconfigurations
SaaS data often lives in cloud storage, managed databases, queues, logs, analytics systems, or backups. Weak storage permissions, overbroad IAM roles, exposed snapshots, or leaked secrets can bypass the application layer entirely.
Insecure admin and support workflows
Internal tools can create serious risk when they allow support impersonation, customer data access, role changes, billing changes, or account recovery without sufficient controls, logging, approval, or segmentation.
Business logic abuse
Business logic flaws occur when attackers abuse intended functionality in unintended ways. In SaaS products, these often affect billing, subscriptions, exports, integrations, approvals, invitations, and workflow state transitions.
SaaS penetration testing for SOC 2 and enterprise security reviews
Many SaaS companies first request penetration testing because of SOC 2, ISO 27001, enterprise procurement, vendor risk assessments, cyber insurance, or customer security reviews.
That is understandable. Buyers want evidence that the product has been tested by an independent third party. Auditors and security reviewers often ask when the last penetration test was performed, what was in scope, what was found, and whether findings were remediated.
SOC 2 does not universally require penetration testing for every company. However, many auditors and enterprise customers expect evidence that relevant security controls have been tested. For SaaS companies, a recent pentest report is often one of the clearest ways to support that conversation.
The important point is that regulatory compliance should not define the entire scope by itself. A SaaS pentest should cover the systems that actually store, process, transmit, or provide access to customer data. That may include the web application, APIs, cloud infrastructure, external assets, authentication flows, admin tooling, integrations, and tenant-isolation controls.
A narrow test may satisfy a checkbox but still miss the risk that an enterprise customer actually cares about.
Black box, gray box, or white box for SaaS pentesting?
Most SaaS penetration tests are strongest as gray box or white box assessments.
O teste de caixa preta pode mostrar o que um invasor externo não autenticado consegue descobrir, mas geralmente oferece cobertura limitada para produtos SaaS, pois os riscos mais importantes surgem após o login e através de funções de usuário, tenants, APIs e fluxos de trabalho.
O teste de caixa cinza é o modelo mais comum. A equipe de teste recebe contas de teste, funções de usuário, documentação limitada, detalhes de API e contexto suficiente para testar cenários autenticados realistas. Este costuma ser o melhor equilíbrio entre realismo, eficiência e profundidade.
O teste de caixa branca oferece aos engenheiros de segurança acesso mais profundo a diagramas de arquitetura, código-fonte, detalhes de infraestrutura, documentação de API, contexto de configuração de nuvem e ambientes de teste completos. É útil quando o objetivo é profundidade máxima, revisão complexa de autorização ou testes de alta garantia antes da adoção corporativa, financiamento ou lançamento importante.
Para empresas SaaS, o segredo não é o rótulo. O segredo é se os pentesters têm acesso e contexto suficientes para testar adequadamente os limites de tenant, permissões de função, autorização de API, fluxos de SSO, ferramentas de administração e lógica de negócios.
Com que frequência as empresas SaaS devem realizar testes de penetração?
A maioria das empresas SaaS deve realizar testes de penetração pelo menos anualmente, especialmente quando SOC 2, ISO 27001, auditorias de clientes corporativos ou seguro cibernético fazem parte do contexto de negócios.
Mas o teste anual é uma base, não uma estratégia completa para produtos em desenvolvimento ativo.
As empresas SaaS devem considerar testes adicionais após grandes lançamentos, mudanças de autenticação ou autorização, novas APIs, novas integrações, mudanças na arquitetura de nuvem, mudanças no modelo de tenant, mudanças nas ferramentas de administração/suporte, grandes migrações de infraestrutura, incidentes de segurança ou antes de ciclos importantes de aquisição corporativa.
Empresas SaaS de alto crescimento, plataformas fintech, produtos de healthtech, SaaS habilitados por IA e empresas que lidam com dados confidenciais de clientes podem se beneficiar de testes direcionados mais frequentes ou de um modelo PTaaS.
A frequência correta de pentest para SaaS deve acompanhar a velocidade do produto e o risco do negócio. Uma empresa que faz lançamentos toda semana não deve depender apenas de uma avaliação anual para validar suas superfícies de ataque mais importantes.
Como se preparar para um teste de penetração em SaaS
Uma boa preparação torna o pentest de SaaS mais eficaz. O objetivo não é sobrecarregar a equipe de pentest com todos os documentos internos. O objetivo é fornecer contexto suficiente para que os pentesters possam focar na validação de caminhos de ataque significativos, em vez de reconstruir o produto do zero.
Antes do início, prepare a URL da aplicação, detalhes do ambiente de teste, funções de usuário, estrutura de tenant, contas de teste, documentação de API, arquivos OpenAPI ou Swagger, coleções do Postman, fluxos de autenticação, detalhes de SSO ou OAuth, diagramas de arquitetura, componentes de nuvem no escopo, fluxos de trabalho de administração/suporte, integrações, documentação de webhook, notas sobre sensibilidade de dados, restrições de segurança de produção e contatos de escalonamento.
Se o isolamento de tenant estiver no escopo, forneça pelo menos dois tenants de teste com múltiplas funções de usuário. Se o teste de API estiver no escopo, forneça autenticação funcional e exemplos de solicitações. Se a infraestrutura de nuvem estiver no escopo, forneça o contexto da arquitetura e defina o que é permitido testar em produção. Se as ferramentas de administração estiverem no escopo, defina quais ações os pentesters podem realizar e como a atividade será monitorada.
Como escolher um provedor de testes de penetração para SaaS
O pentest de SaaS exige mais do que experiência genérica em testes de aplicações web. Um provedor sólido de pentest para SaaS deve entender arquitetura multitenant, autorização de API, infraestrutura de nuvem, SSO e OAuth, lógica de negócios, ferramentas de administração/suporte, integrações, expectativas de SOC 2 e fluxos de remediação. Eles devem ser capazes de testar jornadas de usuários autenticados, raciocinar sobre limites de tenant, validar o impacto e explicar as descobertas de uma forma que as partes interessadas de engenharia, segurança e negócios possam agir.
Pergunte aos potenciais provedores como eles testam o isolamento de tenant, como abordam a autorização de API, se podem avaliar componentes de nuvem, como lidam com retestes, se fornecem relatórios detalhados e se podem oferecer suporte a cronogramas de garantia do cliente ou de conformidade.
O melhor provedor de pentest para SaaS não é aquele que promete a varredura mais ampla. É aquele que entende onde o risco de SaaS realmente reside. Para um guia completo sobre escolher um provedor de testes de penetração, leia nosso artigo sobre o assunto.
Conclusão
O teste de penetração em SaaS não se resume a encontrar vulnerabilidades em aplicações web. Trata-se de testar toda a superfície de ataque do produto: aplicações web, APIs, limites de tenant, infraestrutura em nuvem, fluxos de identidade, integrações, ferramentas administrativas e lógica de negócio.
É aí que geralmente residem os riscos de SaaS de maior impacto. Não em um endpoint isolado ou em uma atualização ausente, mas na forma como sistemas, funções, serviços e fluxos de trabalho confiam uns nos outros.
Para empresas de SaaS que estão se preparando para a SOC 2, vendendo para clientes corporativos, lidando com dados sensíveis ou lançando novos recursos rapidamente, o teste de penetração deve ser estruturado em torno de caminhos de ataque reais e da exposição de dados do cliente, e não apenas em uma lista de verificação.